{
"version": "Notebook/1.0",
"items": [
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"parameters": [
{
"id": "a4b4e975-fa7c-46a3-b669-850aacc88134",
"version": "KqlParameterItem/1.0",
"name": "Help",
"label": "🔎 Guide",
"type": 10,
"isRequired": true,
"typeSettings": {
"additionalResourceOptions": [],
"showDefault": false
},
"jsonData": "[\r\n {\"value\": \"Yes\", \"label\": \"Yes\", \"selected\":true},\r\n {\"value\": \"No\", \"label\": \"No\"}\r\n]",
"value": "No"
},
{
"version": "KqlParameterItem/1.0",
"name": "AzureLighthouse",
"label": "🔦 Azure Lighthouse",
"type": 10,
"isRequired": true,
"value": "No",
"typeSettings": {
"additionalResourceOptions": [],
"showDefault": false
},
"jsonData": "[\r\n {\"value\": \"Yes\", \"label\": \"Yes\", \"selected\":true},\r\n {\"value\": \"No\", \"label\": \"No\"}\r\n]",
"id": "dd4d0170-c366-44b5-beab-9211b2a273cb"
},
{
"version": "KqlParameterItem/1.0",
"name": "DefaultSubscription_Internal",
"type": 1,
"isRequired": true,
"query": "where type =~ 'microsoft.operationalinsights/workspaces'\r\n| take 1\r\n| project subscriptionId",
"crossComponentResources": [
"value::selected"
],
"isHiddenWhenLocked": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"id": "314d02bf-4691-43fa-af59-d67073c8b8fa"
},
{
"id": "e6ded9a1-a83c-4762-938d-5bf8ff3d3d38",
"version": "KqlParameterItem/1.0",
"name": "Subscription",
"type": 6,
"isRequired": true,
"multiSelect": true,
"quote": "'",
"delimiter": ",",
"query": "summarize by subscriptionId\r\n| project value = strcat(\"/subscriptions/\", subscriptionId), label = subscriptionId, selected = iff(subscriptionId =~ '{DefaultSubscription_Internal}', true, false)",
"crossComponentResources": [
"value::all"
],
"typeSettings": {
"additionalResourceOptions": [
"value::all"
],
"showDefault": false
},
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"value": [
"value::all"
]
},
{
"id": "e3225ed0-6210-40a1-b2d0-66e42ffa71d6",
"version": "KqlParameterItem/1.0",
"name": "Workspace",
"type": 5,
"isRequired": true,
"multiSelect": true,
"quote": "'",
"delimiter": ",",
"query": "resources\r\n| where type =~ 'microsoft.operationalinsights/workspaces'\r\n| order by name asc\r\n| summarize Selected = makelist(id, 10), All = makelist(id, 1000)\r\n| mvexpand All limit 100\r\n| project value = tostring(All), label = tostring(All), selected = iff(Selected contains All, true, false)",
"crossComponentResources": [
"{Subscription}"
],
"typeSettings": {
"additionalResourceOptions": [
"value::all"
],
"showDefault": false
},
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"value": [
"value::all"
]
},
{
"id": "15b2c181-7397-43c1-900a-28e175ae8a6f",
"version": "KqlParameterItem/1.0",
"name": "TimeRange",
"type": 4,
"isRequired": true,
"value": {
"durationMs": 604800000
},
"typeSettings": {
"selectableValues": [
{
"durationMs": 14400000
},
{
"durationMs": 43200000
},
{
"durationMs": 86400000
},
{
"durationMs": 259200000
},
{
"durationMs": 604800000
}
],
"allowCustom": true
}
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"name": "Parameter Selectors"
},
{
"type": 1,
"content": {
"json": " Please take time to answer a quick survey,\r\n[ click here. ](https://forms.office.com/r/UjQS9t0TSr)"
},
"name": "Survey"
},
{
"type": 1,
"content": {
"json": "## Getting Started\r\nThis workbook leverages Azure Policy, Azure Resource Graph, and Azure Log Analytics to align directly with the MITRE ATT&CK® Cloud Matrix. A filter set in guide, subscription, workspace, time are available for customized reporting and review. The documentation below provides getting started recommendations for centralizing log analytics data and enabling Microsoft Defender for Cloud Continuous Export. There is telemetry from 25+ Microsoft Security products included in this offering. Common use cases include conducting threat assessments with custom reporting, time filtering, subscription filtering, workspace filtering, and guides. The report is exportable for print or PDF with the Print Workbook feature. The workbook is organized by MITRE ATT&CK® Cloud Matrix tactics, each tactic has multiple technique cards. Technique cards include MITRE ATT&CK® guidance, recommended logs, mitigation steps, Microsoft product portal links, controls crosswalk to NIST SP 800-53 R4, security incidents by technique, and security recommendations
\r\n\r\n### [Recommended Microsoft Sentinel Roles](https://docs.microsoft.com/azure/sentinel/roles) / [Recommended Microsoft Defender for Cloud Roles](https://docs.microsoft.com/azure/defender-for-cloud/permissions#roles-and-allowed-actions)\r\n| Roles | Rights | \r\n|:--|:--|\r\n|Security Reader | View Workbooks, Analytics, Hunting, Security Recommendations |\r\n|Security Contributor| Deploy/Modify Workbooks, Analytics, Hunting, Apply Security Recommendations |\r\n|Owner| Assign Regulatory Compliance Initiatives|\r\n\r\n\r\n1️⃣ [Configure Analytics & Hunting with Microsoft Sentinel: MITRE Blade](https://docs.microsoft.com/azure/sentinel/mitre-coverage)
\r\n2️⃣ [Onboard Microsoft Defender for Cloud](https://docs.microsoft.com/azure/defender-for-cloud/get-started)
\r\n3️⃣ [Add the NIST SP 800-53 R4 Assessment to Your Dashboard](https://docs.microsoft.com/azure/security-center/update-regulatory-compliance-packages#add-a-regulatory-standard-to-your-dashboard)
\r\n4️⃣ [Continuously Export Security Center Data: SecurityRegulatoryCompliance & SecurityRecommendation Data Tables](https://docs.microsoft.com/azure/security-center/continuous-export)
\r\n5️⃣ [Review Security Coverage by the MITRE ATT&CK® Framework](https://docs.microsoft.com/azure/sentinel/mitre-coverage)
\r\n\r\n### Print/Export Report\r\n1️⃣ Set Background Theme: Settings > Appearance > Theme: Azure > Apply
\r\n2️⃣ Print/Export Report: More Content Actions (...) > Print Content
\r\n3️⃣ Settings: Layout (Landscape), Pages (All), Print (One Sided), Scale (60), Pages Per Sheet (1), Quality (1,200 DPI), Margins (None) > Print
\r\n\r\n## Disclaimer\r\nThis workbook demonstrates best practice guidance, but Microsoft does not guarantee nor imply compliance. All requirements, tactics, validations, and controls are governed by respective organizations. This solution provides visibility and situational awareness for security capabilities delivered with Microsoft technologies in predominantly cloud-based environments. Customer experience will vary by user and some panels may require additional configurations for operation. Recommendations do not imply coverage of respective controls as they are often one of several courses of action for approaching requirements which is unique to each customer. Recommendations should be considered a starting point for planning full or partial coverage of respective requirements. ",
"style": "info"
},
"conditionalVisibility": {
"parameterName": "Help",
"comparison": "isEqualTo",
"value": "Yes"
},
"name": "text - 22"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Azure Lighthouse](https://azure.microsoft.com/services/azure-lighthouse/)\r\n---\r\nAzure Lighthouse helps service providers simplify customer engagement and onboarding experiences, while managing delegated resources at scale with agility and precision. Authorized users, groups, and service principals can work directly in the context of a customer subscription without having an account in that customer's Microsoft Entra ID (Entra ID) tenant or being a co-owner of the customer's tenant. The mechanism used to support this access is called Azure delegated resource management. "
},
"customWidth": "40",
"name": "text - 5"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "10",
"name": "text - 2"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "1cf637a7-121d-4722-b511-b0c460625e31",
"linkTarget": "OpenBlade",
"linkLabel": "Access Azure Lighthouse",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "LighthouseBlade",
"extensionName": "Microsoft_Azure_CustomerHub",
"bladeParameters": []
}
}
]
},
"customWidth": "50",
"name": "links - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "managedservicesresources\r\n| where type == \"microsoft.managedservices/registrationassignments\"\r\n| where properties.provisioningState == \"Succeeded\"\r\n| extend ManageeTenantName = properties.registrationDefinition.properties.manageeTenantName\r\n| extend ManagedByTenantName = properties.registrationDefinition.properties.managedByTenantName\r\n| extend ManagedByTenantId = properties.registrationDefinition.properties.managedByTenantId\r\n| extend ManageeTenantId = tostring(properties.registrationDefinition.properties.manageeTenantId)\r\n| extend PermanentAccess = properties.registrationDefinition.properties.authorizations\r\n| extend JITAccess = properties.registrationDefinition.properties.eligibleAuthorizations\r\n| extend AddedDate = properties.registrationDefinition.systemData.createdAt\r\n| extend CreatedBy = systemData.createdBy\r\n| project ManageeTenantName, ManageeTenantId, ManagedByTenantName, ManagedByTenantId, AddedDate, CreatedBy",
"size": 1,
"showAnalytics": true,
"title": "Azure Lighthouse Delegations",
"noDataMessage": "No Azure Lighthouse Delegations/Customers Detected",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Subscription}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "ManageeTenantName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Download",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ManageeTenantId",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": true
}
},
{
"columnMatch": "ManagedByTenantName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Upload",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ManagedByTenantId",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": true
}
},
{
"columnMatch": "AddedDate",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Clock",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "CreatedBy",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Person",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "PermanentAccess",
"formatter": 1
},
{
"columnMatch": "JITAccess",
"formatter": 1
}
],
"filter": true
}
},
"name": "query - 21 - Copy"
}
]
},
"conditionalVisibility": {
"parameterName": "AzureLighthouse",
"comparison": "isEqualTo",
"value": "Yes"
},
"name": "group - 21"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Dynamic Threat Modeling & Response](https://techcommunity.microsoft.com/t5/microsoft-sentinel-blog/i-m-being-attacked-now-what/ba-p/3481937)\n\nThis solution enables SecOps Analysts, Threat Intelligence Professionals, and Threat Hunters to gain situational awareness for threats in cloud, multi-cloud, hybrid, and on-premise environments. This solution is designed to augment staffing through automation, artificial intelligence, machine learning, alert generation, and visualizations. Threat modeling is an advanced cybersecurity discipline requiring detailed knowledge of identifying and acting on the attacker based on observation of indicators in various stages of the attack cycle. This offering provides granular situational awareness across the MITRE ATT&CK® for Cloud Matrix including 75+ Tactic/Technique cards demonstrating a red versus blue approach to threat modeling. "
},
"name": "text - 2"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "nav",
"links": [
{
"id": "1bad541e-219a-4277-9510-876b0e8cad51",
"cellValue": "https://techcommunity.microsoft.com/t5/microsoft-sentinel-blog/i-m-being-attacked-now-what/ba-p/3481937",
"linkTarget": "Url",
"linkLabel": "Solution Blog",
"style": "link"
},
{
"id": "b9a6293e-1c7b-4ec2-ad2a-d72b5ee01722",
"cellValue": "https://youtu.be/8Qb8p-WjpXY",
"linkTarget": "Url",
"linkLabel": "Video Demo",
"style": "link"
},
{
"id": "7e8ff8aa-f632-4a4d-90cf-a71da0dc6b31",
"cellValue": "https://github.com/Azure/Azure-Sentinel/tree/master/Solutions/ThreatAnalysis%26Response",
"linkTarget": "Url",
"linkLabel": "GitHub Repo",
"style": "link"
}
]
},
"name": "links - 29"
}
]
},
"customWidth": "80",
"name": "group - 2"
},
{
"type": 1,
"content": {
"json": " "
},
"customWidth": "18",
"name": "Microsoft Sentinel Logo"
}
]
},
"name": "group - 24"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "{\"version\":\"1.0.0\",\"content\":\"[\\r\\n\\t{ \\\"Capabilities\\\": \\\"Dynamic Threat Modeling\\\", \\\"tab\\\": \\\"AT\\\" },\\r\\n\\t{ \\\"Capabilities\\\": \\\"Controls Crosswalk\\\", \\\"tab\\\": \\\"CO\\\" },\\r\\n\\t{ \\\"Capabilities\\\": \\\"Posture Assessment\\\", \\\"tab\\\": \\\"PA\\\" },\\r\\n\\t{ \\\"Capabilities\\\": \\\"Initial Access\\\", \\\"tab\\\": \\\"IN\\\" },\\r\\n\\t{ \\\"Capabilities\\\": \\\"Execution\\\", \\\"tab\\\": \\\"EX\\\" },\\r\\n\\t{ \\\"Capabilities\\\": \\\"Persistence\\\", \\\"tab\\\": \\\"PE\\\" },\\r\\n\\t{ \\\"Capabilities\\\": \\\"Privilege Escalation\\\", \\\"tab\\\": \\\"PR\\\" },\\r\\n\\t{ \\\"Capabilities\\\": \\\"Defense Evasion\\\", \\\"tab\\\": \\\"DE\\\" }\\r\\n]\",\"transformers\":null}",
"size": 3,
"exportMultipleValues": true,
"exportedParameters": [
{
"fieldName": "tab",
"parameterName": "Tab",
"parameterType": 1
}
],
"queryType": 8,
"gridSettings": {
"formatters": [
{
"columnMatch": "Section",
"formatter": 8,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "tab",
"formatter": 5
}
]
}
},
"customWidth": "40",
"name": "Control Areas",
"styleSettings": {
"showBorder": true
}
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"parameters": [
{
"id": "a30d01d0-38f1-4a91-9cf6-cdb181d676b5",
"version": "KqlParameterItem/1.0",
"name": "isATVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "AT",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"id": "c01e9b8b-b285-4aae-8510-68741e0315c3",
"version": "KqlParameterItem/1.0",
"name": "isCOVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "CO",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"id": "d41cb044-86ef-4603-ae24-c61e864c067d",
"version": "KqlParameterItem/1.0",
"name": "isPAVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "PA",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"version": "KqlParameterItem/1.0",
"name": "isINVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "IN",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "06d92f6d-52f4-4224-9617-fa756b9d5527"
},
{
"id": "7b682fc9-cb6b-4475-a24c-41dcb43d0cef",
"version": "KqlParameterItem/1.0",
"name": "isEXVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "EX",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"id": "0077d493-a27d-49d7-b49d-5888805d501e",
"version": "KqlParameterItem/1.0",
"name": "isPEVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "PE",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"id": "33690532-5a73-4ac3-8fbd-6fc449a6d166",
"version": "KqlParameterItem/1.0",
"name": "isPRVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "PR",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"version": "KqlParameterItem/1.0",
"name": "isDEVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "DE",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "31f5993f-f7f6-4b52-8cb2-80c8eab76d1f"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "10",
"name": "Hidden Parameters"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "{\"version\":\"1.0.0\",\"content\":\"[\\r\\n\\r\\n\\t{ \\\"Capabilities\\\": \\\"Credential Access\\\", \\\"tab\\\": \\\"CR\\\" },\\r\\n\\t{ \\\"Capabilities\\\": \\\"Discovery\\\", \\\"tab\\\": \\\"DI\\\" },\\r\\n\\t{ \\\"Capabilities\\\": \\\"Lateral Movement\\\", \\\"tab\\\": \\\"LA\\\" },\\r\\n\\t{ \\\"Capabilities\\\": \\\"Collection\\\", \\\"tab\\\": \\\"CN\\\" },\\r\\n\\t{ \\\"Capabilities\\\": \\\"Exfiltration\\\", \\\"tab\\\": \\\"EN\\\" },\\r\\n\\t{ \\\"Capabilities\\\": \\\"Impact\\\", \\\"tab\\\": \\\"IM\\\" },\\r\\n\\t{ \\\"Capabilities\\\": \\\"Recommended Data Connectors\\\", \\\"tab\\\": \\\"DC\\\" },\\r\\n\\t{ \\\"Capabilities\\\": \\\"Recommended Content\\\", \\\"tab\\\": \\\"GC\\\" }\\r\\n]\",\"transformers\":null}",
"size": 3,
"exportMultipleValues": true,
"exportedParameters": [
{
"fieldName": "tab",
"parameterName": "Tab",
"parameterType": 1
}
],
"queryType": 8,
"gridSettings": {
"formatters": [
{
"columnMatch": "Section",
"formatter": 8,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "tab",
"formatter": 5
}
]
}
},
"customWidth": "40",
"name": "Control Areas - Copy",
"styleSettings": {
"showBorder": true
}
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"parameters": [
{
"id": "73cdc7ea-4324-442e-bbdd-d77310b97b17",
"version": "KqlParameterItem/1.0",
"name": "isCRVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "CR",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"id": "75a1b8a2-16cf-4f2f-a763-b1b9e94d93e2",
"version": "KqlParameterItem/1.0",
"name": "isDIVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "DI",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"id": "ece98177-94fd-4ea4-8651-82906721d371",
"version": "KqlParameterItem/1.0",
"name": "isLAVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "LA",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"id": "46dc2fbb-711c-49d1-af4d-7339120290ea",
"version": "KqlParameterItem/1.0",
"name": "isCNVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "CN",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"id": "35eafbc4-7586-436c-bb12-88ae110903e1",
"version": "KqlParameterItem/1.0",
"name": "isENVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "EN",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"id": "6f1ec4c5-6e03-4947-a8a8-8f2b1917e3bb",
"version": "KqlParameterItem/1.0",
"name": "isIMVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "IM",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"version": "KqlParameterItem/1.0",
"name": "isDCVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "DC",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "4b981058-a759-4ce4-9d3f-1bfb661efdcb"
},
{
"version": "KqlParameterItem/1.0",
"name": "isGCVisible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "GC",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "3650a515-a590-4451-8a2a-489f09410514"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "10",
"name": "Hidden Parameters - Copy"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [MITRE ATT&CK® for Cloud Tactics](https://attack.mitre.org/matrices/enterprise/cloud/)\r\n----------------------------------------------------------------------------------------------------"
},
"name": "text - 30"
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"crossComponentResources": [
"{Workspace}"
],
"parameters": [
{
"id": "9aec751b-07bd-43ba-80b9-f711887dce45",
"version": "KqlParameterItem/1.0",
"name": "ImpactedUser",
"label": "Targeted User/Account",
"type": 2,
"query": "SecurityAlert\r\n| where Entities <> \"\"\r\n| mv-expand parse_json(Entities)\r\n| parse-where Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\r\n| summarize count() by ImpactedUser\r\n| where ImpactedUser <> \"\"\r\n| sort by count_ desc\r\n| project-away count_\r\n| limit 250",
"crossComponentResources": [
"{Workspace}"
],
"value": null,
"typeSettings": {
"additionalResourceOptions": [],
"showDefault": false
},
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
{
"id": "eff6c9b5-b930-4e95-91c2-cba7a6b58fa7",
"version": "KqlParameterItem/1.0",
"name": "DestinationHostName",
"label": "Targeted Hostname",
"type": 2,
"query": "SecurityAlert\r\n| where Entities <> \"\"\r\n| mv-expand parse_json(Entities)\r\n| parse-where Entities with * '\"HostName\":\"' DestinationHostName '\"' *\r\n| summarize count() by DestinationHostName\r\n| where DestinationHostName <> \"\"\r\n| sort by count_ desc\r\n| project-away count_\r\n| limit 250",
"crossComponentResources": [
"{Workspace}"
],
"value": null,
"typeSettings": {
"additionalResourceOptions": [],
"showDefault": false
},
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
{
"id": "55909726-6744-4191-ba0e-eec6ec7a6282",
"version": "KqlParameterItem/1.0",
"name": "SourceIP",
"label": "Source IP",
"type": 2,
"query": "SecurityAlert\r\n| where Entities <> \"\"\r\n| mv-expand parse_json(Entities)\r\n| parse-where Entities with * '\"Address\":\"' SourceIP '\"' *\r\n| summarize count() by SourceIP\r\n| where SourceIP <> \"\"\r\n| sort by count_ desc\r\n| project-away count_\r\n| limit 250",
"crossComponentResources": [
"{Workspace}"
],
"value": null,
"typeSettings": {
"additionalResourceOptions": [],
"showDefault": false
},
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
{
"id": "cfd60144-b03b-4497-bf4a-59f0ccf25aff",
"version": "KqlParameterItem/1.0",
"name": "SourceCountry",
"label": "Source Country",
"type": 2,
"query": "SecurityAlert\r\n| where Entities <> \"\"\r\n| mv-expand parse_json(Entities)\r\n| parse-where Entities with * '\"CountryName\":\"' SourceCountry '\"' *\r\n| summarize count() by SourceCountry\r\n| where SourceCountry <> \"\"\r\n| sort by count_ desc\r\n| project-away count_\r\n| limit 250",
"crossComponentResources": [
"{Workspace}"
],
"value": null,
"typeSettings": {
"additionalResourceOptions": [],
"showDefault": false
},
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
{
"id": "96bfefa4-13de-447b-b949-d876f9b50f60",
"version": "KqlParameterItem/1.0",
"name": "AssignedAnalyst",
"label": "Assigned Analyst",
"type": 2,
"query": "SecurityIncident\r\n| where Owner <> \"\"\r\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\r\n| summarize count() by AssignedAnalyst\r\n| where AssignedAnalyst <> \"\"\r\n| sort by count_ desc\r\n| project-away count_\r\n| limit 250",
"crossComponentResources": [
"{Workspace}"
],
"value": null,
"typeSettings": {
"additionalResourceOptions": [],
"showDefault": false
},
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
{
"id": "76c1da14-3cee-40c5-9208-19d85f89af2e",
"version": "KqlParameterItem/1.0",
"name": "DetectingProduct",
"label": "Detecting Product",
"type": 2,
"query": "SecurityAlert\r\n| where ProductName <> \"\"\r\n| extend DetectingProduct = ProductName\r\n| summarize count() by DetectingProduct\r\n| where DetectingProduct <> \"\"\r\n| sort by count_ desc\r\n| project-away count_\r\n| limit 250",
"crossComponentResources": [
"{Workspace}"
],
"value": null,
"typeSettings": {
"additionalResourceOptions": [],
"showDefault": false
},
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"name": "Threat Research Parameters"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\n| where Tactics <> \"\"\n| where Entities <> \"\"\n| where Tactics contains \"initial\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/tactics/TA0001/\")",
"size": 4,
"showAnalytics": true,
"title": "Initial Access",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumFractionDigits": 0,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "TA0001"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "Initial Access",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\n| where Tactics <> \"\"\n| where Entities <> \"\"\n| where Tactics contains \"execution\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/tactics/TA0002/\")",
"size": 4,
"showAnalytics": true,
"title": "Execution",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumFractionDigits": 0,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "TA0002"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "Execution",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\n| where Tactics <> \"\"\n| where Entities <> \"\"\n| where Tactics contains \"persistence\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/tactics/TA0003/\")\n\n\n",
"size": 4,
"showAnalytics": true,
"title": "Persistence",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "TA0003"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "Persistence",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\n| where Tactics <> \"\"\n| where Entities <> \"\"\n| where Tactics contains \"privilege\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/tactics/TA0004/\")\n\n",
"size": 4,
"showAnalytics": true,
"title": "Privilege Escalation",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "TA0004"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "Privilege Escalation",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\n| where Tactics <> \"\"\n| where Entities <> \"\"\n| where Tactics contains \"defense\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/tactics/TA0005/\")\n",
"size": 4,
"showAnalytics": true,
"title": "Defense Evasion",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "TA0005"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "Defense Evasion",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\n| where Tactics <> \"\"\n| where Entities <> \"\"\n| where Tactics contains \"credential\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/tactics/TA0006/\")\n\n",
"size": 4,
"showAnalytics": true,
"title": "Credential Access",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumFractionDigits": 2
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "TA0006"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "Credential Access",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\n| where Tactics <> \"\"\n| where Entities <> \"\"\n| where Tactics contains \"discovery\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/tactics/TA0007/\")\n\n",
"size": 4,
"showAnalytics": true,
"title": "Discovery",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumFractionDigits": 2,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "TA0007"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "Discovery",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\n| where Tactics <> \"\"\n| where Entities <> \"\"\n| where Tactics contains \"lateral\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/tactics/TA0008/\")\n\n",
"size": 4,
"showAnalytics": true,
"title": "Lateral Movement",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "TA0008"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "Lateral Movement",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\n| where Tactics <> \"\"\n| where Entities <> \"\"\n| where Tactics contains \"collection\"\n| mv-expand parse_json(Entities)| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/tactics/TA0008/\")\n\n\n",
"size": 4,
"showAnalytics": true,
"title": "Collection",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "TA0008"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "Collection",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\n| where Tactics <> \"\"\n| where Entities <> \"\"\n| where Tactics contains \"exfiltration\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/tactics/TA0010/\")\n\n",
"size": 4,
"showAnalytics": true,
"title": "Exfiltration",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "TA0010"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "Exfiltration",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\n| where Tactics <> \"\"\n| where Entities <> \"\"\n| where Tactics contains \"impact\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/tactics/TA0040/\")\n\n",
"size": 4,
"showAnalytics": true,
"title": "Impact",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "TA0040"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "Impact",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": "# [MITRE ATT&CK® for Cloud Techniques](https://attack.mitre.org/matrices/enterprise/cloud/)\r\n----------------------------------------------------------------------------------------------------"
},
"name": "text - 15"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1189\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1189/\")",
"size": 4,
"showAnalytics": true,
"title": "Drive-by Compromise",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1189"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 18",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1204\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1204/\")",
"size": 4,
"showAnalytics": true,
"title": "User Execution",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1204"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 16",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1098\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1098/\")",
"size": 4,
"showAnalytics": true,
"title": "Account Manipulation",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1098"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 18",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1484\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1484/\")",
"size": 4,
"showAnalytics": true,
"title": "Domain Policy Modification",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1484"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 18",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1484\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1484/\")",
"size": 4,
"showAnalytics": true,
"title": "Domain Policy Modification",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1484"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 19",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1110\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1110/\")\n",
"size": 4,
"showAnalytics": true,
"title": "Brute Force",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1110"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 20",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1087\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1087/\")",
"size": 4,
"showAnalytics": true,
"title": "Account Discovery",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1087"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 21",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1534\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1534/\")",
"size": 4,
"showAnalytics": true,
"title": "Internal Spear-phishing",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1534"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 23",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1530\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1530/\")",
"size": 4,
"showAnalytics": true,
"title": "Data from Cloud Storage Object",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1530"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 23",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1537\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1537/\")",
"size": 4,
"showAnalytics": true,
"title": "Transfer Data to Cloud Account",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1537"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 24",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1485\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1485/\")",
"size": 4,
"showAnalytics": true,
"title": "Data Destruction",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1485"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 25",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1190\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1190/\")",
"size": 4,
"showAnalytics": true,
"title": "Exploit Public-Facing Application",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1190"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 26",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 27"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1136\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1136/\")",
"size": 4,
"showAnalytics": true,
"title": "Create Account",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1136"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 28",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1078\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1078/\")",
"size": 4,
"showAnalytics": true,
"title": "Valid Accounts",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1078"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 29",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1564\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1564/\")",
"size": 4,
"showAnalytics": true,
"title": "Hide Artifacts",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1564"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 30",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1606\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1606/\")",
"size": 4,
"showAnalytics": true,
"title": "Forge Web Credentials",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1606"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 31",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1580\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1580/\")",
"size": 4,
"showAnalytics": true,
"title": "Cloud Infrastructure Discovery",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1580"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 32",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1080\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1080/\")",
"size": 4,
"showAnalytics": true,
"title": "Taint Shared Content",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1080"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 33",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1213\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1213/\")",
"size": 4,
"showAnalytics": true,
"title": "Data from Information Repositories",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1213"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 34",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 35"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1486\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1486/\")",
"size": 4,
"showAnalytics": true,
"title": "Data Encrypted for Impact",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1486"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 35",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1566\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1566/\")",
"size": 4,
"showAnalytics": true,
"title": "Phishing",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1566"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 37",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 38"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1525\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1525/\")",
"size": 4,
"showAnalytics": true,
"title": "Implant Internal Image",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1525"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 39",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 40"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1562\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1562/\")",
"size": 4,
"showAnalytics": true,
"title": "Impair Defenses",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1562"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 40",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1528\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1528/\")",
"size": 4,
"showAnalytics": true,
"title": "Steal Application Access Token",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1528"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 40 - Copy",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1538\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1538/\")",
"size": 4,
"showAnalytics": true,
"title": "Cloud Service Dashboard",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1538"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 43",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1550\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1550/\")",
"size": 4,
"showAnalytics": true,
"title": "Use Alternate Authentication Material",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1550"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 45",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1074\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1074/\")",
"size": 4,
"showAnalytics": true,
"title": "Data Staged",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1074"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 45",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 46"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1491\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1491/\")",
"size": 4,
"showAnalytics": true,
"title": "Defacement",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1491"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 46",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1199\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1199/\")",
"size": 4,
"showAnalytics": true,
"title": "Trusted Relationship",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1199"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 48",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 49"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1137\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1137/\")",
"size": 4,
"showAnalytics": true,
"title": "Office Application Startup",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1137"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 49",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 51"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1578\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1578/\")",
"size": 4,
"showAnalytics": true,
"title": "Modify Cloud Compute Infrastructure",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1578"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 51",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1539\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1539/\")",
"size": 4,
"showAnalytics": true,
"title": "Steal Web Session Cookie",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1539"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 53",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1526\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1526/\")",
"size": 4,
"showAnalytics": true,
"title": "Cloud Service Discovery",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1526"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 54",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 55"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1114\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1114/\")",
"size": 4,
"showAnalytics": true,
"title": "Email Collection",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1114"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 55",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 57"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1499\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1499/\")",
"size": 4,
"showAnalytics": true,
"title": "Endpoint Denial of Service",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1499"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 57",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1078\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1078/\")",
"size": 4,
"showAnalytics": true,
"title": "Valid Accounts",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1078"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 59",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 60"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1078\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1078/\")",
"size": 4,
"showAnalytics": true,
"title": "Valid Accounts",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1078"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 60",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 62"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1535\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1535/\")",
"size": 4,
"showAnalytics": true,
"title": "Unused/Unsupported Cloud Regions",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1535"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 62",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1552\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1552/\")",
"size": 4,
"showAnalytics": true,
"title": "Unsecured Credentials",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1552"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 64",
"styleSettings": {
"showBorder": true
}
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1619\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1619/\")",
"size": 4,
"showAnalytics": true,
"title": "Cloud Storage Object Discovery",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1619"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 65",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 66"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 66 - Copy"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 66 - Copy - Copy"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1498\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1498/\")",
"size": 4,
"showAnalytics": true,
"title": "Network Denial of Service",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1498"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 66",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 70"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 70 - Copy"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 70 - Copy - Copy"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 70 - Copy - Copy - Copy"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1550\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1550/\")",
"size": 4,
"showAnalytics": true,
"title": "Use Alternate Authentication Material",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1550"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 70",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 70 - Copy - Copy - Copy - Copy"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1046\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1046/\")",
"size": 4,
"showAnalytics": true,
"title": "Network Service Scanning",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1046"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 76",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 70 - Copy - Copy - Copy - Copy - Copy"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 70 - Copy - Copy - Copy - Copy - Copy - Copy"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 70 - Copy - Copy - Copy - Copy - Copy - Copy - Copy"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1496\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1496/\")",
"size": 4,
"showAnalytics": true,
"title": "Resource Hijacking",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1496"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 78",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "36",
"name": "text - 80"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1078\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1078/\")",
"size": 4,
"showAnalytics": true,
"title": "Valid Accounts",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1078"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 60",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "9",
"name": "text - 98"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1201\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1201/\")",
"size": 4,
"showAnalytics": true,
"title": "Password Policy Discovery",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1201"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 78",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "36",
"name": "text - 82"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "54",
"name": "text - 82 - Copy"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1069\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1069/\")",
"size": 4,
"showAnalytics": true,
"title": "Permission Groups Discovery",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1069"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 78",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "36",
"name": "text - 85"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "54",
"name": "text - 85 - Copy"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1518\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1518/\")",
"size": 4,
"showAnalytics": true,
"title": "Software Discovery",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1518"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 88",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "36",
"name": "text - 88"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "54",
"name": "text - 88 - Copy"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1082\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1082/\")",
"size": 4,
"showAnalytics": true,
"title": "System Information Discovery",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1082"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 78",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "36",
"name": "text - 91"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "54",
"name": "text - 91 - Copy"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1614\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1614/\")",
"size": 4,
"showAnalytics": true,
"title": "System Location Discovery",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1614"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 78",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "36",
"name": "text - 94"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "54",
"name": "text - 95"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\n| extend SystemAlertId = tostring(AlertIds[0])\n| join kind=fullouter (SecurityAlert) on SystemAlertId\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\n| where Techniques contains \"T1082\"\n| mv-expand parse_json(Entities)\n| extend AssignedAnalyst = tostring(Owner.assignedTo)\n| extend DetectingProduct = ProductName\n| parse Entities with * '\"DisplayName\":\"' ImpactedUser '\"' *\n| parse Entities with * '\"HostName\":\"' DestinationHostName '\"' *\n| parse Entities with * '\"CountryName\":\"' SourceCountry '\"' *\n| parse Entities with * '\"Address\":\"' SourceIP '\"' *\n| where AssignedAnalyst contains '{AssignedAnalyst}' or AssignedAnalyst == \"*\"\n| where ImpactedUser contains '{ImpactedUser}' or ImpactedUser == \"*\"\n| where DetectingProduct contains '{DetectingProduct}' or DetectingProduct == \"*\"\n| where DestinationHostName contains '{DestinationHostName}' or DestinationHostName == \"*\"\n| where SourceIP contains '{SourceIP}' or SourceIP == \"*\"\n| where SourceCountry contains '{SourceCountry}' or SourceCountry == \"*\"\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\n| summarize count()\n| extend Link = strcat(\"https://attack.mitre.org/techniques/T1082/\")",
"size": 4,
"showAnalytics": true,
"title": "System Network Connections Discovery",
"noDataMessage": "No Alerts/Incidents Observed Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"visualization": "tiles",
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "60%"
}
},
{
"columnMatch": "name",
"formatter": 0,
"formatOptions": {
"customColumnWidthSetting": "5%"
}
},
{
"columnMatch": "severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "Critical",
"representation": "critical",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Major",
"representation": "2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": null,
"text": "{0}{1}"
}
],
"customColumnWidthSetting": "5"
}
},
{
"columnMatch": "message",
"formatter": 7,
"formatOptions": {
"linkTarget": "CellDetails",
"linkIsContextBlade": false,
"customColumnWidthSetting": "70%"
}
}
]
},
"sortBy": [],
"tileSettings": {
"titleContent": {
"formatter": 1
},
"leftContent": {
"columnMatch": "count_",
"formatter": 8,
"formatOptions": {
"min": 0,
"palette": "greenRed"
},
"numberFormat": {
"unit": 17,
"options": {
"style": "decimal",
"useGrouping": false,
"maximumSignificantDigits": 3
}
}
},
"secondaryContent": {
"columnMatch": "Link",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "T1082"
}
},
"showBorder": false,
"size": "auto"
}
},
"customWidth": "9",
"name": "query - 78",
"styleSettings": {
"showBorder": true
}
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "36",
"name": "text - 97"
}
]
},
"conditionalVisibility": {
"parameterName": "isATVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Attacks Observed",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Controls Crosswalk](https://github.com/Azure/Azure-Sentinel/tree/master/Solutions/ThreatAnalysis%26Response)\r\n---\r\nControls crosswalk provides a mapping of MITRE ATT&CK® Cloud Matrix tactics across NIST controls for mitigation. This provides free-text search capabilities mapping NIST SP 800-53 R4 to MITRE ATT&CK® techniques. There is also a mapping for recommended Microsoft products for each of these control requirements. This panel facilitates exploring specific tactics, techniques, controls, and recommended products at scale. For example, searching \"T1189\", \"exploit\", \"exfiltration\", \"AC-2\", or \"Microsoft Sentinel\" all product respective insights. Below this panel is an assessment of Security Alerts by Tactics over Time and Detecting products. "
},
"customWidth": "40",
"name": "Controls Mapping"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "let Crosswalk = datatable([\"MITRE ATT&CK® Techniques\"]: string, [\"MITRE ATT&CK® Tactics\"]: string, [\"Mitigation Controls: NIST SP 800-53 R4\"]: string, [\"Recommended Products\"]: string) [\r\n\"[T1189] Drive-by Compromise\",\t\"Initial Access\",\t\"AC-4 | AC-6 | CA-7 | CM-2 | CM-6 | CM-8 | SA-22 | SC-18 | SC-2 | SC-29 | SC-3 | SC-30 | SC-39 | SC-7 | SI-2 | SI-3 | SI-4 | SI-7\",\t\"Microsoft Defender for Endpoint | Azure Web Application Firewall | Azure Automation | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1190] Exploit Public-Facing Application\",\t\"Initial Access\",\t\"AC-2 | AC-3 | AC-4 | AC-5 | AC-6 | CA-2 | CA-7 | CM-5 | CM-6 | CM-7 | CM-8 | IA-2 | IA-8 | RA-5 | SA-8 | SC-18 | SC-2 | SC-29 | SC-3 | SC-30 | SC-39 | SC-7 | SI-10 | SI-2 | SI-3 | SI-4 | SI-7\",\t\"Microsoft Defender for Endpoint | Network Security Groups | Azure Active Directory | Azure Web Application Firewall | Azure Automation | Azure Firewall | Virtual Network | Microsoft Defender for Cloud Apps | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1566] Phishing\",\t\"Initial Access\",\t\"AC-4 | CA-7 | CM-2 | CM-6 | IA-9 | SC-20 | SC-44 | SC-7 | SI-2 | SI-3 | SI-4 | SI-8\",\t\"Microsoft Defender for Office 365 | Azure Firewall | Microsoft Learn | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1199] Trusted Relationship\",\t\"Initial Access\",\t\"AC-3 | AC-4 | AC-6 | AC-8 | CM-6 | CM-7 | SC-7\",\t\"Azure Active Directory | Network Security Groups | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1078] Valid Accounts\",\t\"Initial Access\",\t\"AC-2 | AC-3 | AC-5 | AC-6 | CA-7 | CA-8 | CM-5 | CM-6 | IA-2 | IA-5 | RA-5 | SA-10 | SA-11 | SA-12 | SA-15 | SA-16 | SA-17 | SA-3 | SA-4 | SA-8 | SC-28 | SI-4\",\t\"Azure Active Directory | Microsoft 365 Defender | Microsoft Defender for Cloud Apps | Key Vault | Privileged Identity Management | Microsoft Defender for Endpoint | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1204] User Execution\",\t\"Execution\",\t\"AC-4 | CA-7 | CM-2 | CM-6 | CM-7 | SC-44 | SC-7 | SI-10 | SI-2 | SI-3 | SI-4 | SI-7 | SI-8\",\t\"Microsoft Defender for Endpoint | Azure Firewall | Microsoft Learn | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1098] Account Manipulation\",\t\"Persistence\",\t\"AC-2 | AC-3 | AC-4 | AC-5 | AC-6 | CM-5 | CM-6 | CM-7 | IA-2 | SC-7 | SI-4\",\t\"Azure Active Directory | Microsoft 365 Defender | Virtual Machines | Network Security Groups | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1136] Create Account\",\t\"Persistence\",\t\"AC-2 | AC-20 | AC-3 | AC-4 | AC-5 | AC-6 | CM-5 | CM-6 | CM-7 | IA-2 | IA-5 | SC-7 | SI-4 | SI-7\",\t\"Azure Active Directory | Microsoft 365 Defender | Privileged Identity Management | Network Security Groups | Virtual Machines | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1525] Implant Internal Image\",\t\"Persistence\",\t\"AC-2 | AC-3 | AC-5 | AC-6 | CA-8 | CM-2 | CM-5 | CM-6 | CM-7 | IA-2 | IA-9 | RA-5 | SI-2 | SI-3 | SI-4 | SI-7\",\t\"Privileged Identity Management | Microsoft 365 Defender | Microsoft Defender for Cloud Apps | Key Vaults | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1137] Office Application Startup\",\t\"Persistence\",\t\"AC-10 | AC-17 | AC-6 | CM-2 | CM-6 | CM-8 | RA-5 | SC-18 | SI-2 | SI-3 | SI-4 | SI-8\",\t\"Microsoft 365 Defender | Microsoft Defender for Endpoint | Microsoft Defender for Cloud Apps | Automation Accounts |Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1078] Valid Accounts\",\t\"Persistence\",\t\"AC-2 | AC-3 | AC-5 | AC-6 | CA-7 | CA-8 | CM-5 | CM-6 | IA-2 | IA-5 | RA-5 | SA-10 | SA-11 | SA-12 | SA-15 | SA-16 | SA-17 | SA-3 | SA-4 | SA-8 | SC-28 | SI-4\",\t\"Microsoft Defender for Endpoint | Network Security Groups | Azure Active Directory | Azure Web Application Firewall | Azure Automation | Azure Firewall | Virtual Network | Microsoft Defender for Cloud Apps | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1484] Domain Policy Modification\",\t\"Privilege Escalation\",\t\"AC-2 | AC-3 | AC-4 | AC-5 | AC-6 | CA-8 | CM-2 | CM-5 | CM-6 | CM-7 | IA-2 | RA-5 | SI-4\",\t\"Privileged Identity Management | Microsoft 365 Defender | Microsoft Defender for Cloud Apps | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1078] Valid Accounts\",\t\"Privilege Escalation\",\t\"AC-2 | AC-3 | AC-5 | AC-6 | CA-7 | CA-8 | CM-5 | CM-6 | IA-2 | IA-5 | RA-5 | SA-10 | SA-11 | SA-12 | SA-15 | SA-16 | SA-17 | SA-3 | SA-4 | SA-8 | SC-28 | SI-4\",\t\"Microsoft Defender for Endpoint | Network Security Groups | Azure Active Directory | Azure Web Application Firewall | Azure Automation | Azure Firewall | Virtual Network | Microsoft Defender for Cloud Apps | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1484] Domain Policy Modification\",\t\"Defense Evasion\",\t\"AC-2 | AC-3 | AC-4 | AC-5 | AC-6 | CA-8 | CM-2 | CM-5 | CM-6 | CM-7 | IA-2 | RA-5 | SI-4\",\t\"Privileged Identity Management | Microsoft 365 Defender | Microsoft Defender for Cloud Apps | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1564] Hide Artifacts\",\t\"Defense Evasion\",\t\"N/A\",\t\"Privileged Identity Management | Security Baselines | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1562] Impair Defenses\",\t\"Defense Evasion\",\t\"AC-2 | AC-3 | AC-5 | AC-6 | CA-7 | CA-8 | CM-2 | CM-5 | CM-6 | CM-7 | IA-2 | IA-4 | RA-5 | SI-3 | SI-4 | SI-7\",\t\"Azure Active Directory | Microsoft Defender for Cloud Apps | Azure Information Protection | Microsoft 365 Defender | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1578] Modify Cloud Compute Infrastructure\",\t\"Defense Evasion\",\t\"AC-2 | AC-3 | AC-5 | AC-6 | CA-8 | CM-5 | IA-2 | IA-4 | IA-6 | RA-5 | SI-4\",\t\"Microsoft 365 Defender | Microsoft Defender for Cloud Apps | Azure Active Directory | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1535] Unused/Unsupported Cloud Regions\",\t\"Defense Evasion\",\t\"SC-23\",\t\"Azure Policy | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1550] Use Alternate Authentication Material\",\t\"Defense Evasion\",\t\"AC-2 | AC-3 | AC-5 | AC-6 | CM-5 | CM-6 | IA-2\",\t\"Microsoft Defender for Identity | Microsoft 365 Defender | Azure Active Directory | Microsoft Defender for Cloud Apps | Privileged Identity Management | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1078] Valid Accounts\",\t\"Defense Evasion\",\t\"AC-2 | AC-3 | AC-5 | AC-6 | CA-7 | CA-8 | CM-5 | CM-6 | IA-2 | IA-5 | RA-5 | SA-10 | SA-11 | SA-12 | SA-15 | SA-16 | SA-17 | SA-3 | SA-4 | SA-8 | SC-28 | SI-4\",\t\"Microsoft Defender for Endpoint | Network Security Groups | Azure Active Directory | Azure Web Application Firewall | Azure Automation | Azure Firewall | Virtual Network | Microsoft Defender for Cloud Apps | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1110] Brute Force\",\t\"Credential Access\",\t\"AC-2 | AC-20 | AC-3 | AC-5 | AC-6 | AC-7 | CA-7 | CM-2 | CM-6 | IA-11 | IA-2 | IA-4 | IA-5 | SI-4\",\t\"Azure Active Directory | Azure Policy | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1606] Forge Web Credentials\",\t\"Credential Access\",\t\"AC-2 | AC-3 | AC-5 | AC-6 | MA-5 | SC-17 | SI-2\",\t\"Azure Active Directory | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1528] Steal Application Access Token\",\t\"Credential Access\",\t\"AC-10 | AC-2 | AC-3 | AC-4 | AC-5 | AC-6 | CA-7 | CA-8 | CM-2 | CM-5 | CM-6 | IA-2 | IA-4 | IA-5 | IA-8 | RA-5 | SA-11 | SA-15 | SI-4\",\t\"Azure Active Directory | Microsoft 365 Defender | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1539] Steal Web Session Cookie\",\t\"Credential Access\",\t\"AC-20 | AC-3 | AC-6 | CA-7 | CM-2 | CM-6 | IA-2 | IA-5 | SI-3 | SI-4\",\t\"Azure Active Directory | Azure Policy | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1552] Unsecured Credentials\",\t\"Credential Access\",\t\"AC-16 | AC-17 | AC-18 | AC-19 | AC-2 | AC-20 | AC-3 | AC-4 | AC-5 | AC-6 | CA-7 | CA-8 | CM-2 | CM-5 | CM-6 | CM-7 | IA-2 | IA-3 | IA-4 | IA-5 | RA-5 | SA-11 | SA-15 | SC-12 | SC-28 | SC-4 | SC-7 | SI-10 | SI-12 | SI-15 | SI-2 | SI-4 | SI-7\",\t\"Microsoft Defender for Cloud Apps | Key Vault | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1087] Account Discovery\",\t\"Discovery\",\t\"CM-6 | CM-7 | SI-4\",\t\"Microsoft 365 Defender | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1580] Cloud Infrastructure Discovery\",\t\"Discovery\",\t\"AC-2 | AC-3 | AC-5 | AC-6 | IA-2\",\t\"Azure Active Directory | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1538] Cloud Service Dashboard\",\t\"Discovery\",\t\"AC-2 | AC-3 | AC-5 | AC-6 | IA-2 | IA-8\",\t\"Azure Active Directory | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1526] Cloud Service Discovery\",\t\"Discovery\",\t\"N/A\",\t\"Microsoft Sentinel\",\r\n\"[T1619] Cloud Storage Object Discovery\",\t\"Discovery\",\t\"AC-17 | AC-2 | AC-3 | AC-5 | AC-6 | CM-5 | IA-2\",\t\"Azure Active Directory | Microsoft Defender for Cloud Apps | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1046] Network Service Scanning\",\t\"Discovery\",\t\"AC-4 | CA-7 | CM-2 | CM-6 | CM-7 | CM-8 | RA-5 | SC-7 | SI-3 | SI-4\",\t\"Azure Firewall | Network Security Groups | Microsoft Defender for Cloud Apps | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1201] Password Policy Discovery\",\t\"Discovery\",\t\"CA-7 | CM-2 | CM-6 | SI-3 | SI-4\",\t\"Azure Active Directory | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1069] Permission Groups Discovery\",\t\"Discovery\",\t\"N/A\",\t\"Microsoft Sentinel\",\r\n\"[T1518] Software Discovery\",\t\"Discovery\",\t\"N/A\",\t\"Microsoft Sentinel\",\r\n\"[T1082] System Information Discovery\",\t\"Discovery\",\t\"N/A\",\t\"Microsoft Sentinel\",\r\n\"[T1614] System Location Discovery\",\t\"Discovery\",\t\"N/A\",\t\"Microsoft Sentinel\",\r\n\"[T1049] System Network Connections Discovery\",\t\"Discovery\",\t\"N/A\",\t\"Microsoft Sentinel\",\r\n\"[T1534] Internal Spear-phishing\",\t\"Lateral Movement\",\t\"N/A\",\t\"Microsoft Sentinel\",\r\n\"[T1080] Taint Shared Content\",\t\"Lateral Movement\",\t\"AC-3 | CA-7 | CM-2 | CM-7 | SC-4 | SC-7 | SI-10 | SI-3 | SI-4 | SI-7\",\t\"Microsoft 365 Defender | Azure Active Directory | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1550] Use Alternate Authentication Material\",\t\"Lateral Movement\",\t\"AC-2 | AC-3 | AC-5 | AC-6 | CM-5 | CM-6 | IA-2\",\t\"Azure Active Directory | Privileged Identity Management | Microsoft Defender for Cloud Apps | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1530] Data from Cloud Storage Object\",\t\"Collection\",\t\"AC-17 | AC-2 | AC-3 | AC-5 | AC-6 | CM-5 | IA-2\",\t\"Azure Active Directory | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1213] Data from Information Repositories\",\t\"Collection\",\t\"AC-16 | AC-17 | AC-2 | AC-21 | AC-23 | AC-3 | AC-4 | AC-5 | AC-6 | CA-7 | CA-8 | CM-2 | CM-3 | CM-5 | CM-6 | CM-7 | CM-8 | IA-2 | IA-4 | IA-8 | RA-5 | SC-28 | SI-4 | SI-7\",\t\"Azure Active Directory | Microsoft 365 Defender | Microsoft Learn | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1074] Data Staged\",\t\"Collection\",\t\"N/A\",\t\"Microsoft Sentinel\",\r\n\"[T1114] Email Collection\",\t\"Collection\",\t\"AC-16 | AC-17 | AC-19 | AC-20 | AC-3 | AC-4 | CM-2 | CM-6 | IA-2 | IA-5 | SC-7 | SI-12 | SI-4 | SI-7\",\t\"Microsoft 365 Defender | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1537] Transfer Data to Cloud Account\",\t\"Exfiltration\",\t\"AC-16 | AC-17 | AC-2 | AC-20 | AC-3 | AC-4 | AC-5 | AC-6 | CA-7 | CM-5 | CM-6 | CM-7 | IA-2 | IA-3 | IA-4 | IA-8 | SC-7 | SI-10 | SI-15 | SI-4\",\t\"Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1485] Data Destruction\",\t\"Impact\",\t\"AC-3 | AC-6 | CM-2 | CP-10 | CP-2 | CP-7 | CP-9 | SI-3 | SI-4 | SI-7\",\t\"Backup Vaults | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1486] Data Encrypted for Impact\",\t\"Impact\",\t\"AC-3 | AC-6 | CM-2 | CP-10 | CP-2 | CP-6 | CP-7 | CP-9 | SI-3 | SI-4 | SI-7\",\t\"Backup Vaults | Backup Center | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1491] Defacement\",\t\"Impact\",\t\"AC-3 | AC-6 | CM-2 | CP-10 | CP-2 | CP-7 | CP-9 | SI-3 | SI-4 | SI-7\",\t\"Backup Vaults | Azure Web Application Firewall | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1499] Endpoint Denial of Service\",\t\"Impact\",\t\"AC-3 | AC-4 | CA-7 | CM-6 | CM-7 | SC-7 | SI-10 | SI-15 | SI-4\",\t\"Microsoft 365 Defender | Azure DDoS | Network Security Groups | Azure Firewall | Virtual Networks | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1498] Network Denial of Service\",\t\"Impact\",\t\"AC-3 | AC-4 | CA-7 | CM-6 | CM-7 | SC-7 | SI-10 | SI-15\",\t\"Azure DDoS | Network Security Groups | Azure Firewall | Virtual Networks | Microsoft Sentinel | Microsoft Defender for Cloud\",\r\n\"[T1496] Resource Hijacking\",\t\"Impact\",\t\"N/A\",\t\"Microsoft Sentinel\"\r\n];\r\nCrosswalk\r\n| project [\"MITRE ATT&CK® Techniques\"], [\"MITRE ATT&CK® Tactics\"], [\"Mitigation Controls: NIST SP 800-53 R4\"], [\"Recommended Products\"]",
"size": 0,
"showAnalytics": true,
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "MITRE ATT&CK® Techniques",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Recommended Products",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "success",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Control Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
}
],
"filter": true
}
},
"name": "query - 1"
}
]
},
"conditionalVisibility": {
"parameterName": "isCOVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Controls Mapping"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Posture Assessment](https://docs.microsoft.com/azure/defender-for-cloud/regulatory-compliance-dashboard)\r\n---\r\n\r\nThis section leverages Microsoft Defender for Cloud: Regulatory Compliance for policy assessments. Find, fix, and resolve recommendations aligned to the NIST SP 800-53 Regulatory Compliance Initiative. A selector provides capability to filter by all, specific, or groups of controls by level. Upon selection, subordinate panels will summarize recommendations by control family, status over time, recommendations, and resources identified."
},
"customWidth": "40",
"name": "text - 5"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "10",
"name": "text - 2"
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"crossComponentResources": [
"{Workspace}"
],
"parameters": [
{
"id": "99a47f97-1aa4-4840-91ee-119aad6d6217",
"version": "KqlParameterItem/1.0",
"name": "ComplianceDomain",
"label": "Control Family",
"type": 2,
"isRequired": true,
"multiSelect": true,
"quote": "'",
"delimiter": ",",
"query": "SecurityRegulatoryCompliance\r\n| where ComplianceStandard == \"NIST-SP-800-53-R4\"\r\n| extend ComplianceDomain=iff(ComplianceControl contains \"AC.\", \"Access Control\", iff(ComplianceControl contains \"AT.\", \"Security Awareness & Training\", iff(ComplianceControl contains \"AU.\", \"Audit & Accountability\", iff(ComplianceControl contains \"CA.\", \"Security Assessment\", iff(ComplianceControl contains \"CM.\", \"Configuration Management\", iff(ComplianceControl contains \"CP.\", \"Contingency Planning\", iff(ComplianceControl contains \"IA.\", \"Identification & Authentication\", iff(ComplianceControl contains \"IR.\", \"Incident Response\", iff(ComplianceControl contains \"MA.\", \"System Maintenance\", iff(ComplianceControl contains \"MP.\", \"Media Protection\", iff(ComplianceControl contains \"PE.\", \"Physical Protection\", iff(ComplianceControl contains \"PL.\", \"Security Planning\", iff(ComplianceControl contains \"PS.\", \"Personnel Security\",iff(ComplianceControl contains \"RA.\", \"Risk Assessment\",iff(ComplianceControl contains \"SA.\", \"System & Services Acquisition\",iff(ComplianceControl contains \"SC.\", \"System & Communications Protection\",iff(ComplianceControl contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n| summarize count() by ComplianceDomain\r\n| sort by count_ desc\r\n| project-away count_",
"crossComponentResources": [
"{Workspace}"
],
"typeSettings": {
"additionalResourceOptions": [
"value::all"
],
"showDefault": false
},
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"defaultValue": "value::all",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"value": [
"value::all"
]
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "40",
"name": "parameters - 26"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId == \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId == \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId == \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink) on RecommendationName\r\n | extend ComplianceDomain=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n| where ComplianceDomain in ({ComplianceDomain}) \r\n | distinct RecommendationName, ComplianceDomain, tostring(RecommendationLink), tostring(state), tostring(complianceState)\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), NotApplicable = countif(state == \"NotApplicable\"), Applicable = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\"),Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\" or state == \"NotApplicable\") by ComplianceDomain\r\n | extend PassedControls = (Passed/todouble(Applicable))*100\r\n | project ControlFamily=ComplianceDomain, Total, PassedControls, Passed, Failed, Applicable, NotApplicable\r\n | sort by Total, Passed desc\r\n ",
"size": 0,
"showAnalytics": true,
"title": "Recommendations by Control Family",
"noDataMessage": "Select Getting Started in Top Left of Workbook. Follow Guidance for Steps 3-5",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "[\"Passed\"]/[\"Applicable\"]",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
},
{
"columnName": "NotApplicable",
"color": "gray"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "Passed",
"formatter": 5
},
{
"columnMatch": "Failed",
"formatter": 5
},
{
"columnMatch": "Applicable",
"formatter": 5
},
{
"columnMatch": "NotApplicable",
"formatter": 5
},
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "Remediate >>"
}
}
],
"filter": true
},
"sortBy": []
},
"customWidth": "50",
"name": "query - 3 - Copy"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId == \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId == \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), NotApplicable = countif(state == \"NotApplicable\"), Applicable = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\"),Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\" or state == \"NotApplicable\") by RecommendationName, ControlID = controlId\r\n | extend PassedControls = (Passed/todouble(Applicable))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId == \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | extend ComplianceDomain=iff(ControlID contains \"AC.\", \"Access Control\", iff(ControlID contains \"AT.\", \"Security Awareness & Training\", iff(ControlID contains \"AU.\", \"Audit & Accountability\", iff(ControlID contains \"CA.\", \"Security Assessment\", iff(ControlID contains \"CM.\", \"Configuration Management\", iff(ControlID contains \"CP.\", \"Contingency Planning\", iff(ControlID contains \"IA.\", \"Identification & Authentication\", iff(ControlID contains \"IR.\", \"Incident Response\", iff(ControlID contains \"MA.\", \"System Maintenance\", iff(ControlID contains \"MP.\", \"Media Protection\", iff(ControlID contains \"PE.\", \"Physical Protection\", iff(ControlID contains \"PL.\", \"Security Planning\", iff(ControlID contains \"PS.\", \"Personnel Security\",iff(ControlID contains \"RA.\", \"Risk Assessment\",iff(ControlID contains \"SA.\", \"System & Services Acquisition\",iff(ControlID contains \"SC.\", \"System & Communications Protection\",iff(ControlID contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n| where ComplianceDomain in ({ComplianceDomain}) \r\n | distinct RecommendationName, Total, RecommendationLink, PassedControls, Passed, Failed, NotApplicable, Applicable, name\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "Recommendations ",
"noDataMessage": "Select Getting Started in Top Left of Workbook. Follow Guidance for Steps 3-5",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "[\"Passed\"]/[\"Applicable\"]",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
},
{
"columnName": "NotApplicable",
"color": "gray"
}
]
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 5,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "Passed",
"formatter": 5
},
{
"columnMatch": "Failed",
"formatter": 5
},
{
"columnMatch": "NotApplicable",
"formatter": 5
},
{
"columnMatch": "Applicable",
"formatter": 5
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"customWidth": "50",
"name": "query - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId == \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId == \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ComplianceDomain=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n| where ComplianceDomain in ({ComplianceDomain}) \r\n| distinct RecommendationName, resourceId, tostring(state), tostring(complianceState)\r\n| summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), NotApplicable = countif(state == \"NotApplicable\"), Applicable = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\"),Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\" or state == \"NotApplicable\") by resourceId\r\n| extend PassedControls = (Passed/todouble(Applicable))*100\r\n| where Failed > 0\r\n| project AssessedResourceId=resourceId, Total, PassedControls, Passed, Failed, Applicable, NotApplicable\r\n| sort by Total, Passed desc\r\n| limit 250\r\n",
"size": 0,
"showAnalytics": true,
"title": "Recommendations by Asset",
"noDataMessage": "Select Getting Started in Top Left of Workbook. Follow Guidance for Steps 3-5",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "AssessedResourceId",
"formatter": 13,
"formatOptions": {
"linkTarget": "Resource",
"showIcon": true
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "[\"Passed\"]/[\"Applicable\"]",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
},
{
"columnName": "NotApplicable",
"color": "gray"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "Passed",
"formatter": 5
},
{
"columnMatch": "Failed",
"formatter": 5
},
{
"columnMatch": "Applicable",
"formatter": 5
},
{
"columnMatch": "NotApplicable",
"formatter": 5
},
{
"columnMatch": "resourceId",
"formatter": 13,
"formatOptions": {
"linkTarget": null,
"showIcon": true
}
},
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "Url",
"linkLabel": "Remediate >>"
}
}
],
"filter": true
},
"sortBy": []
},
"customWidth": "50",
"name": "query - 9"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityRegulatoryCompliance\r\n| where ComplianceStandard == \"NIST-SP-800-53-R4\"\r\n| extend ComplianceDomain=iff(ComplianceControl contains \"AC.\", \"Access Control\", iff(ComplianceControl contains \"AT.\", \"Security Awareness & Training\", iff(ComplianceControl contains \"AU.\", \"Audit & Accountability\", iff(ComplianceControl contains \"CA.\", \"Security Assessment\", iff(ComplianceControl contains \"CM.\", \"Configuration Management\", iff(ComplianceControl contains \"CP.\", \"Contingency Planning\", iff(ComplianceControl contains \"IA.\", \"Identification & Authentication\", iff(ComplianceControl contains \"IR.\", \"Incident Response\", iff(ComplianceControl contains \"MA.\", \"System Maintenance\", iff(ComplianceControl contains \"MP.\", \"Media Protection\", iff(ComplianceControl contains \"PE.\", \"Physical Protection\", iff(ComplianceControl contains \"PL.\", \"Security Planning\", iff(ComplianceControl contains \"PS.\", \"Personnel Security\",iff(ComplianceControl contains \"RA.\", \"Risk Assessment\",iff(ComplianceControl contains \"SA.\", \"System & Services Acquisition\",iff(ComplianceControl contains \"SC.\", \"System & Communications Protection\",iff(ComplianceControl contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n| where ComplianceDomain in ({ComplianceDomain})\r\n| where State == \"Failed\"\r\n| make-series count() default=0 on TimeGenerated from startofday({TimeRange:start}) to startofday({TimeRange:end}) step 1d by ComplianceDomain\r\n| render timechart ",
"size": 0,
"showAnalytics": true,
"title": "Recommendations over Time",
"noDataMessage": "Select Getting Started in Top Left of Workbook. Follow Guidance for Steps 3-5",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "AssessedResourceId",
"formatter": 13,
"formatOptions": {
"linkTarget": "Resource",
"showIcon": true
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "ComplianceDomain",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "count_",
"formatter": 4,
"formatOptions": {
"palette": "yellowOrangeRed"
}
}
],
"filter": true
},
"sortBy": []
},
"customWidth": "50",
"name": "query - 6 - Copy"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId == \"NIST SP 800 53 R4\"\r\n | extend failedResources = toint(properties.failedResources), passedResources = toint(properties.passedResources),skippedResources = toint(properties.skippedResources)\r\n | where failedResources + passedResources + skippedResources > 0\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationDisplayName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend azurePortalRecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId == \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | where state == \"Unhealthy\"\r\n | extend Recommendation = strcat(\"https://\",azurePortalRecommendationLink), ResourceID = resourceId, ResourceType = resourceType, ResourceGroup = resourceGroup1, Severity = severity, State = state, ControlID = controlId\r\n | extend ComplianceDomain=iff(ControlID contains \"AC.\", \"Access Control\", iff(ControlID contains \"AT.\", \"Security Awareness & Training\", iff(ControlID contains \"AU.\", \"Audit & Accountability\", iff(ControlID contains \"CA.\", \"Security Assessment\", iff(ControlID contains \"CM.\", \"Configuration Management\", iff(ControlID contains \"CP.\", \"Contingency Planning\", iff(ControlID contains \"IA.\", \"Identification & Authentication\", iff(ControlID contains \"IR.\", \"Incident Response\", iff(ControlID contains \"MA.\", \"System Maintenance\", iff(ControlID contains \"MP.\", \"Media Protection\", iff(ControlID contains \"PE.\", \"Physical Protection\", iff(ControlID contains \"PL.\", \"Security Planning\", iff(ControlID contains \"PS.\", \"Personnel Security\",iff(ControlID contains \"RA.\", \"Risk Assessment\",iff(ControlID contains \"SA.\", \"System & Services Acquisition\",iff(ControlID contains \"SC.\", \"System & Communications Protection\",iff(ControlID contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | extend FirstObserved = properties1.status.statusChangeDate\r\n | where ComplianceDomain in ({ComplianceDomain})\r\n | project ResourceID, RecommendationName=RecommendationDisplayName, ControlFamily=ComplianceDomain, ControlID, Severity=tostring(Severity), CurrentState=State, RecommendationLink=Recommendation, name, FirstObserved\r\n| extend Rank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, 0)))\r\n| sort by Rank desc\r\n| limit 2500\r\n",
"size": 0,
"showAnalytics": true,
"title": "Current Recommendation Details",
"noDataMessage": "Select Getting Started in Top Left of Workbook. Follow Guidance for Steps 3-5",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "ResourceID",
"formatter": 13,
"formatOptions": {
"linkTarget": "Resource",
"showIcon": true
}
},
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlID",
"formatter": 1
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "State",
"formatter": 1
},
{
"columnMatch": "Recommendation",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
},
{
"columnMatch": "FirstObserved",
"formatter": 6
},
{
"columnMatch": "Rank",
"formatter": 5
}
],
"rowLimit": 2500,
"filter": true
}
},
"name": "query - 8"
}
]
},
"conditionalVisibility": {
"parameterName": "isPAVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Assessment",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Initial Access](https://attack.mitre.org/tactics/TA0001/) \r\n---\r\nThe adversary is trying to get into your network. Initial Access consists of techniques that use various entry vectors to gain their initial foothold within a network. Techniques used to gain a foothold include targeted spear-phishing and exploiting weaknesses on public-facing web servers. Footholds gained through initial access may allow for continued access, like valid accounts and use of external remote services, or may be limited-use due to changing passwords."
},
"customWidth": "40",
"name": "text - 7"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "10",
"name": "text - 8"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "{\"version\":\"1.0.0\",\"content\":\"[\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1189] Drive-by Compromise\\\", \\\"tab\\\": \\\"T1189\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1190] Exploit Public-Facing Application\\\", \\\"tab\\\": \\\"T1190\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1566] Phishing\\\", \\\"tab\\\": \\\"T1566\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1199] Trusted Relationship\\\", \\\"tab\\\": \\\"T1199\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1078] Valid Accounts\\\", \\\"tab\\\": \\\"T1078\\\" }\\r\\n]\",\"transformers\":null}",
"size": 3,
"exportMultipleValues": true,
"exportedParameters": [
{
"fieldName": "tab",
"parameterName": "Tab",
"parameterType": 1
}
],
"queryType": 8,
"gridSettings": {
"formatters": [
{
"columnMatch": "Section",
"formatter": 8,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "tab",
"formatter": 5
}
]
}
},
"customWidth": "40",
"name": "Control Areas",
"styleSettings": {
"showBorder": true
}
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"parameters": [
{
"id": "a30d01d0-38f1-4a91-9cf6-cdb181d676b5",
"version": "KqlParameterItem/1.0",
"name": "isT1189Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1189",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1190Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1190",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "7cdaa20d-616e-46b4-a1e0-0b32be69de6c"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1566Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1566",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "b89bdf83-1d1f-4814-8b45-9198fbf86a4f"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1199Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1199",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "978e1814-6d20-4d36-946d-5171f0d80d92"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1078Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1078",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "2f63a507-8422-4009-8c65-5f3575a29b4b"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "10",
"name": "Hidden Parameters"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Drive-by Compromise (T1189)](https://attack.mitre.org/techniques/T1189)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Application Isolation and Sand-boxing (M1048)](https://attack.mitre.org/mitigations/M1048)
\r\n🟦 [Exploit Protection (M1050)](https://attack.mitre.org/mitigations/M1050)
\r\n🟦 [Restrict Web-Based Content (M1021)](https://attack.mitre.org/mitigations/M1021)
\r\n🟦 [Update Software (M1051)](https://attack.mitre.org/mitigations/M1051)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Application Isolation and Sand-boxing) Leverage Microsoft Defender Application Guard](https://docs.microsoft.com/windows/security/threat-protection/microsoft-defender-application-guard/md-app-guard-overview)
\r\n💡 [(Exploit Protection) Create and Deploy an Exploit Guard Policy](https://docs.microsoft.com/mem/configmgr/protect/deploy-use/create-deploy-exploit-guard-policy)
\r\n💡 [(Restrict Web-Based Content) Deploy Azure Web Application Firewall](https://docs.microsoft.com/azure/web-application-firewall/ag/application-gateway-web-application-firewall-portal)
\r\n💡 [(Update Software) Leverage Azure Automation Accounts for Updates/Patching](https://docs.microsoft.com/azure/automation/update-management/enable-from-portals)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
\r\n🔀 [Web Application Firewall Policies](https://portal.azure.com/#blade/Microsoft_Azure_Network/LoadBalancingHubMenuBlade/loadBalancers)
\r\n🔀 [Automation Accounts](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Automation%2FAutomationAccounts) \r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-4, AC-6, CA-7, CM-2, CM-6, CM-8, SA-22, SC-18, SC-2, SC-29, SC-3, SC-30, SC-39, SC-7, SI-2, SI-3, SI-4, SI-7](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1189\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ ('AC.4.*','AC.6*','CA.7.*','CM.2.*','CM.6.*','CM.8.*','SA.22*','SC.18.*','SC.2.*','SC.29.*','SC.3*','SC.30.*','SC.39.*','SC.7.*','SI.2.*','SI.3.*','SI.4.*','SI.7.*')\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1189Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Drive-by Compromise",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Exploit Public-Facing Application (T1190)](https://attack.mitre.org/techniques/T1190/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Application Isolation and Sand-boxing (M1048)](https://attack.mitre.org/mitigations/M1048)
\r\n🟦 [Exploit Protection (M1050)](https://attack.mitre.org/mitigations/M1050)
\r\n🟦 [Network Segmentation (M1030)](https://attack.mitre.org/mitigations/M1030)
\r\n🟦 [Privileged Account Management (M1026)](https://attack.mitre.org/mitigations/M1026)
\r\n🟦 [Restrict Web-Based Content (M1021)](https://attack.mitre.org/mitigations/M1021)
\r\n🟦 [Update Software (M1051)](https://attack.mitre.org/mitigations/M1051)
\r\n🟦 [Vulnerability Scanning (M1016)](https://attack.mitre.org/mitigations/M1016)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Application Isolation and Sand-boxing) Leverage Microsoft Defender Application Guard](https://docs.microsoft.com/windows/security/threat-protection/microsoft-defender-application-guard/md-app-guard-overview)
\r\n💡 [(Exploit Protection) Create and Deploy an Exploit Guard Policy](https://docs.microsoft.com/mem/configmgr/protect/deploy-use/create-deploy-exploit-guard-policy)
\r\n💡 [(Network Segmentation) Leverage Network Security Groups](https://docs.microsoft.com/azure/virtual-network/manage-network-security-group)
\r\n💡 [(Privileged Account Management) Deploy Entra ID Privileged Identity Management (PIM)](https://docs.microsoft.com/azure/active-directory/privileged-identity-management/pim-deployment-plan)
\r\n💡 [(Restrict Web-Based Content) Deploy Azure Web Application Firewall](https://docs.microsoft.com/azure/web-application-firewall/ag/application-gateway-web-application-firewall-portal)
\r\n💡 [(Restrict Web-Based Content) Deploy Microsoft Defender for Endpoint](https://docs.microsoft.com/microsoft-365/security/defender-endpoint/deployment-phases)
\r\n💡 [(Restrict Web-Based Content) Deploy Azure Application Gateway](https://docs.microsoft.com/azure/application-gateway/quick-create-portal)
\r\n💡 [(Restrict Web-Based Content) Deploy Azure Web Application Firewall](https://docs.microsoft.com/azure/web-application-firewall/ag/application-gateway-web-application-firewall-portal)
\r\n💡 [(Update Software) Leverage Azure Automation Accounts for Updates/Patching](https://docs.microsoft.com/azure/automation/update-management/enable-from-portals)
\r\n💡 [(Update Software) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n💡 [(Vulnerability Scanning) Deploy Microsoft Defender for Cloud Apps for Integrated Vulnerability Assessments](https://docs.microsoft.com/azure/security-center/deploy-vulnerability-assessment-vm)
\r\n💡 [(Vulnerability Scanning) Deploy Microsoft Defender for Endpoint for Threat Vulnerability Management](https://docs.microsoft.com/microsoft-365/security/defender-endpoint/next-gen-threat-and-vuln-mgt)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft 365 Security Center](https://security.microsoft.com/)
\r\n🔀 [Network Security Groups](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Network%2FNetworkSecurityGroups)
\r\n🔀 [Privileged Identity Management](https://portal.azure.com/#blade/Microsoft_Azure_PIMCommon/CommonMenuBlade/quickStart)
\r\n🔀 [Web Application Firewall Policies](https://portal.azure.com/#blade/Microsoft_Azure_Network/LoadBalancingHubMenuBlade/loadBalancers)
\r\n🔀 [Application Security Groups](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Network%2FvirtualNetworks)
\r\n🔀 [Firewall Manager](https://portal.azure.com/#blade/Microsoft_Azure_HybridNetworking/FirewallManagerMenuBlade/firewallManagerOverview)
\r\n🔀 [Virtual Networks](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Network%2FvirtualNetworks)
\r\n🔀 [Privileged Identity Management](https://portal.azure.com/#blade/Microsoft_Azure_PIMCommon/CommonMenuBlade/quickStart)
\r\n🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
\r\n🔀 [Automation Accounts](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Automation%2FAutomationAccounts)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-2, AC-3, AC-4, AC-5, AC-6, CA-2, CA-7, CM-5, CM-6, CM-7, CM-8, IA-2, IA-8, RA-5, SA-8, SC-18, SC-2, SC-29, SC-3, SC-30, SC-39, SC-7, SI-10, SI-2, SI-3, SI-4, SI-7](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1190\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.4.*\", \"AC.5.*\", \"AC.6.*\", \"CA.2.*\", \"CA.7.*\", \"CM.5.*\", \"CM.6.*\", \"CM.7.*\", \"CM.8.*\", \"IA.2.*\", \"IA.8.*\", \"RA.5.*\", \"SA.8.*\", \"SC.18.*\", \"SC.2.*\", \"SC.29.*\", \"SC.3.*\", \"SC.30.*\", \"SC.39.*\", \"SC.7.*\", \"SI.10.*\", \"SI.2.*\", \"SI.3.*\", \"SI.4.*\", \"SI.7.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1190Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Exploit Public-Facing Application",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Phishing (T1566)](https://attack.mitre.org/techniques/T1566)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Spear-Phishing Attachment (T1566.001)](https://attack.mitre.org/techniques/T1566/001/)
\r\n🟥 ️[Spear-Phishing Link (T1566.002)](https://attack.mitre.org/techniques/T1566/002/)
\r\n🟥 ️[Spear-Phishing via Service (T1566.003)](https://attack.mitre.org/techniques/T1566/003/)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityAlert](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityalert) 🔷 [OfficeActivity](https://docs.microsoft.com/azure/azure-monitor/reference/tables/officeactivity) ✳️ [Microsoft Defender for Office 365](https://www.microsoft.com/microsoft-365/security/office-365-defender)
\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Antivirus/Antimalware (M1049)](https://attack.mitre.org/mitigations/M1049)
\r\n🟦 [Network Intrusion Prevention (M1031)](https://attack.mitre.org/mitigations/M1031)
\r\n🟦 [Restrict Web-Based Content (M1021)](https://attack.mitre.org/mitigations/M1021)
\r\n🟦 [Software Configuration (M1054)](https://attack.mitre.org/mitigations/M1054)
\r\n🟦 [User Training (M1017)](https://attack.mitre.org/mitigations/M1017)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Antivirus/Antimalware) Configure Anti-Phishing Policies in Microsoft Defender for Office 365](https://docs.microsoft.com/microsoft-365/security/office-365-security/configure-mdo-anti-phishing-policies)
\r\n💡 [(Network Intrusion Prevention) Enable Azure Firewall: IPDS](https://docs.microsoft.com/azure/firewall/premium-features#idps)
\r\n💡 [(Restrict Web-Based Content) Leverage Safe Links in Microsoft Defender for Office 365](https://docs.microsoft.com/microsoft-365/security/office-365-security/atp-safe-links)
\r\n💡 [(Software Configuration) Leverage Microsoft 365 & Microsoft Defender XDR for Email Security](https://docs.microsoft.com/microsoft-365/security/office-365-security/use-dmarc-to-validate-email)
\r\n💡 [(User Training) Leverage Microsoft Learn for Security Threat Training](https://docs.microsoft.com/learn/browse/?terms=security%20threat)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
\r\n🔀 [Firewall Policies: IPDS](https://portal.azure.com/#blade/HubsExtension/BrowseResourceBlade/resourceType/Microsoft.Network%2FfirewallPolicies)
\r\n🔀 [Microsoft Learn](https://docs.microsoft.com/learn)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-4, CA-7, CM-2, CM-6, IA-9, SC-20, SC-44, SC-7, SI-2, SI-3, SI-4, SI-8](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1566\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.4.*\", \"CA.7.*\", \"CM.2.*\", \"CM.6.*\", \"IA.9.*\", \"SC.20.*\", \"SC.44.*\", \"SC.7.*\", \"SI.2.*\", \"SI.3.*\", \"SI.4.*\", \"SI.8.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1566Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Phishing",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Trusted Relationship (T1199)](https://attack.mitre.org/techniques/T1199)\r\n\r\n### Recommended Logs\r\n🔷 [SigninLogs](https://docs.microsoft.com/azure/azure-monitor/reference/tables/signinlogs) ✳️ [Microsoft Entra ID](https://azure.microsoft.com/services/active-directory/)
\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Network Segmentation (M1030)](https://attack.mitre.org/mitigations/M1030)
\r\n🟦 [User Account Control (M1052)](https://attack.mitre.org/mitigations/M1052)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Network Segmentation) Leverage Network Security Groups](https://docs.microsoft.com/azure/virtual-network/manage-network-security-group)
\r\n💡 [(User Account Control) Microsoft Entra ID: Monitor Non-Organizational Account Sign-Ins](https://docs.microsoft.com/azure/active-directory/reports-monitoring/concept-all-sign-ins)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n🔀 [Network Security Groups](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Network%2FNetworkSecurityGroups)
\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-3, AC-4, AC-6, AC-8, CM-6, CM-7, SC-7](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1199\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.3.*\", \"AC.4.*\", \"AC.6.*\", \"AC.8.*\", \"CM.6.*\", \"CM.7.*\", \"SC.7.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1199Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Trusted Relationship",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Valid Accounts (T1078)](https://attack.mitre.org/techniques/T1078/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Default Accounts (T1078.001)](https://attack.mitre.org/techniques/T1078/001/)
\r\n🟥 ️[Cloud Accounts (T1078.004)](https://attack.mitre.org/techniques/T1078/004/)\r\n\r\n### Recommended Logs\r\n🔷 [SigninLogs](https://docs.microsoft.com/azure/azure-monitor/reference/tables/signinlogs) ✳️ [Microsoft Entra ID](https://azure.microsoft.com/services/active-directory/)
🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) 🔷 [SecurityBaselines](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securitybaseline) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Multi-Factor Authentication (M1032)](https://attack.mitre.org/mitigations/M1032)
\r\n🟦 [Application Developer Guidance (M1013)](https://attack.mitre.org/mitigations/M1013)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n🟦 [Privileged Account Management (M1026)](https://attack.mitre.org/mitigations/M1026)
\r\n🟦 [Password Policies (M1027)](https://attack.mitre.org/mitigations/M1027)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Multi-Factor Authentication) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n💡 [(Application Developer Guidance) Secure Identity with Zero Trust](https://docs.microsoft.com/security/zero-trust/identity)
\r\n💡 [(Application Developer Guidance) Secure Secrets with Azure Key Vault](https://docs.microsoft.com/azure/key-vault/general/basic-concepts)
\r\n💡 [(Privileged Account Management) Deploy Entra ID Privileged Identity Management (PIM)](https://docs.microsoft.com/azure/active-directory/privileged-identity-management/pim-deployment-plan)
\r\n💡 [(Password Policies) Password and Account Lockout Policies on Microsoft Entra ID Domain Services Managed Domains](https://docs.microsoft.com/azure/active-directory-domain-services/password-policy#)
\r\n💡 [(User Account Management) What are Entra ID access reviews?](https://docs.microsoft.com/azure/active-directory/governance/access-reviews-overview)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
\r\n🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
\r\n🔀 [Key Vaults](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.KeyVault%2Fvaults)
\r\n🔀 [Privileged Identity Management](https://portal.azure.com/#blade/Microsoft_Azure_PIMCommon/CommonMenuBlade/quickStart)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-2, AC-3, AC-5, AC-6, CA-7, CA-8, CM-5, CM-6, IA-2, IA-5, RA-5, SA-10, SA-11, SA-12, SA-15, SA-16, SA-17, SA-3, SA-4, SA-8, SC-28, SI-4](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1078\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"CA.7.*\", \"CA.8.*\", \"CM.5.*\", \"CM.6.*\", \"IA.2.*\", \"IA.5.*\", \"RA.5.*\", \"SA.10.*\", \"SA.11.*\", \"SA.12.*\", \"SA.15.*\", \"SA.16.*\", \"SA.17.*\", \"SA.3.*\", \"SA.4.*\", \"SA.8.*\", \"SC.28.*\", \"SI.4.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "let FailedAssets=SecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"password\"\r\n| where AnalyzeResult == \"Failed\"\r\n| summarize FailedAssets = makelist(Computer) by Description;\r\nlet PassedAssets=SecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"password\"\r\n| where AnalyzeResult == \"Passed\"\r\n| summarize PassedAssets = makelist(Computer) by Description;\r\nSecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"password\"\r\n| summarize\r\n Failed = countif(AnalyzeResult == \"Failed\"),\r\n Passed = countif(AnalyzeResult == \"Passed\"),\r\n Total = countif(AnalyzeResult == \"Failed\" or AnalyzeResult == \"Passed\")\r\n by Description\r\n| extend PassedControls = (Passed / todouble(Total)) * 100\r\n| join kind=fullouter(FailedAssets) on Description\r\n| join kind=fullouter(PassedAssets) on Description\r\n| project Description, Total, PassedControls, Passed, Failed, PassedAssets, FailedAssets\r\n| sort by Total, Passed desc\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 ️[Password Policies] Review Security Baselines",
"noDataMessage": "An Empty Panel Provides Opportunity To Explore Further and Implement Hardening. Controls: Confirm Licensing, Availability, and Health of Respective Offerings. Logging: Confirm Log Source is Onboarded to the Log Analytics Workspace. Time: Adjust the Time Parameter for a Larger Data-Set. ",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationDisplayName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "ControlNumber",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "AllServices",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "RecommendationState",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "!=",
"thresholdValue": "Healthy",
"representation": "3",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "success",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "count_",
"formatter": 4,
"formatOptions": {
"palette": "blue"
}
}
],
"filter": true
}
},
"customWidth": "50",
"name": "query - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "let LastObserved = SigninLogs\r\n| where ResultType == 0\r\n| summarize arg_max(TimeGenerated, *) by UserPrincipalName\r\n| project UserPrincipalName, LastSignIn=TimeGenerated;\r\nSigninLogs\r\n| extend UserProfile = strcat(\"#blade/Microsoft_AAD_IAM/UserDetailsMenuBlade/Profile/userId/\", UserId)\r\n| where ResultType == 0\r\n| summarize count() by UserPrincipalName, UserProfile, UserId\r\n| join (LastObserved) on UserPrincipalName\r\n| project UserPrincipalName, SignInCount=count_, UserProfile, LastSignIn, UserId\r\n| sort by SignInCount desc\r\n| limit 250\r\n",
"size": 0,
"showAnalytics": true,
"title": "🟦 ️[User Account Management] Review Valid Accounts",
"noDataMessage": "An Empty Panel Provides Opportunity To Explore Further and Implement Hardening. Controls: Confirm Licensing, Availability, and Health of Respective Offerings. Logging: Confirm Log Source is Onboarded to the Log Analytics Workspace. Time: Adjust the Time Parameter for a Larger Data-Set. ",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "UserPrincipalName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Person",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "SignInCount",
"formatter": 4,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "UserProfile",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Entra ID User Profile >>",
"bladeOpenContext": {
"bladeName": "UserDetailsMenuBlade",
"extensionName": "Microsoft_AAD_IAM",
"bladeParameters": [
{
"name": "userId",
"source": "column",
"value": "UserId"
}
]
}
}
},
{
"columnMatch": "UserId",
"formatter": 5
},
{
"columnMatch": "count_",
"formatter": 4,
"formatOptions": {
"palette": "yellowOrangeRed"
}
}
],
"filter": true
},
"sortBy": [],
"mapSettings": {
"locInfo": "LatLong",
"locInfoColumn": "Location",
"latitude": "latitude_",
"longitude": "longitude_",
"sizeSettings": "city_",
"sizeAggregation": "Count",
"labelSettings": "city_",
"legendMetric": "city_",
"numberOfMetrics": 100,
"legendAggregation": "Count",
"itemColorSettings": {
"nodeColorField": "state_",
"colorAggregation": "Count",
"type": "heatmap",
"heatmapPalette": "coldHot"
}
}
},
"customWidth": "50",
"name": "query - 9"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1078Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Valid Accounts",
"styleSettings": {
"showBorder": true
}
}
]
},
"conditionalVisibility": {
"parameterName": "isINVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Initial Access Group"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Execution](https://attack.mitre.org/tactics/TA0002/)\r\n---\r\nThe adversary is trying to run malicious code. Execution consists of techniques that result in adversary-controlled code running on a local or remote system. Techniques that run malicious code are often paired with techniques from all other tactics to achieve broader goals, like exploring a network or stealing data. For example, an adversary might use a remote access tool to run a PowerShell script that does Remote System Discovery.\r\n"
},
"customWidth": "40",
"name": "Execution Guide"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "10",
"name": "text - 4"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "{\"version\":\"1.0.0\",\"content\":\"[\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1204] User Execution\\\", \\\"tab\\\": \\\"T1204\\\" }\\r\\n]\",\"transformers\":null}",
"size": 3,
"exportMultipleValues": true,
"exportedParameters": [
{
"fieldName": "tab",
"parameterName": "Tab",
"parameterType": 1
}
],
"queryType": 8,
"gridSettings": {
"formatters": [
{
"columnMatch": "Section",
"formatter": 8,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "tab",
"formatter": 5
}
]
}
},
"customWidth": "40",
"name": "Control Areas",
"styleSettings": {
"showBorder": true
}
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"parameters": [
{
"id": "a30d01d0-38f1-4a91-9cf6-cdb181d676b5",
"version": "KqlParameterItem/1.0",
"name": "isT1204Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1204",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "10",
"name": "Hidden Parameters"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [User Execution (T1204)](https://attack.mitre.org/techniques/T1204)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Malicious Link (T1204.001)](https://attack.mitre.org/techniques/T1204/001/)
\r\n🟥 ️[Malicious File (T1204.002)](https://attack.mitre.org/techniques/T1204/002/)
\r\n🟥 ️[Malicious Image (T1204.003)](https://attack.mitre.org/techniques/T1204/003/)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Execution Prevention (M1038)](https://attack.mitre.org/mitigations/M1038)
\r\n🟦 [Network Intrusion Prevention (M1031)](https://attack.mitre.org/mitigations/M1031)
\r\n🟦 [Restrict Web-Based Content (M1021)](https://attack.mitre.org/mitigations/M1021)
\r\n🟦 [User Training (M1017)](https://attack.mitre.org/mitigations/M1017)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Execution Prevention) Leverage Microsoft Defender Application Guard](https://docs.microsoft.com/windows/security/threat-protection/microsoft-defender-application-guard/md-app-guard-overview)
\r\n💡 [(Network Intrusion Prevention) Leverage Azure Firewall for Network Intrusion Prevention](https://docs.microsoft.com/azure/firewall/premium-features#idpst)
\r\n💡 [(Restrict Web-Based Content) Leverage Microsoft Defender for Endpoint for Web Content Filtering](https://docs.microsoft.com/microsoft-365/security/defender-endpoint/web-content-filtering)
\r\n💡 [(User Training) Leverage Microsoft Learn for Security Threat Training](https://docs.microsoft.com/learn/browse/?terms=security%20threat)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
\r\n🔀 [Firewall Manager](https://portal.azure.com/#blade/Microsoft_Azure_HybridNetworking/FirewallManagerMenuBlade/firewallManagerOverview)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-4, CA-7, CM-2, CM-6, CM-7, SC-44, SC-7, SI-10, SI-2, SI-3, SI-4, SI-7, SI-8](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1204\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.4.*\", \"CA.7.*\", \"CM.2.*\", \"CM.6.*\", \"CM.7.*\", \"SC.44.*\", \"SC.7.*\", \"SI.10.*\", \"SI.2.*\", \"SI.3.*\", \"SI.4.*\", \"SI.7.*\", \"SI.8.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1204Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "User Execution",
"styleSettings": {
"showBorder": true
}
}
]
},
"conditionalVisibility": {
"parameterName": "isEXVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Execution Group"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Persistence](https://attack.mitre.org/tactics/TA0003/) \r\n---\r\nThe adversary is trying to maintain their foothold. Persistence consists of techniques that adversaries use to keep access to systems across restarts, changed credentials, and other interruptions that could cut off their access. Techniques used for persistence include any access, action, or configuration changes that let them maintain their foothold on systems, such as replacing or hijacking legitimate code or adding startup code.\r\n"
},
"customWidth": "40",
"name": "Persistence Guide"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "10",
"name": "text - 7"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "{\"version\":\"1.0.0\",\"content\":\"[\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1098] Account Manipulation\\\", \\\"tab\\\": \\\"T1098\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1136] Create Account\\\", \\\"tab\\\": \\\"T1136\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1525] Implant Internal Image\\\", \\\"tab\\\": \\\"T1525\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1137] Office Application Startup\\\", \\\"tab\\\": \\\"T1137\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1078] Valid Accounts\\\", \\\"tab\\\": \\\"T1078\\\" }\\r\\n]\",\"transformers\":null}",
"size": 3,
"exportMultipleValues": true,
"exportedParameters": [
{
"fieldName": "tab",
"parameterName": "Tab",
"parameterType": 1
}
],
"queryType": 8,
"gridSettings": {
"formatters": [
{
"columnMatch": "Section",
"formatter": 8,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "tab",
"formatter": 5
}
]
}
},
"customWidth": "40",
"name": "Control Areas",
"styleSettings": {
"showBorder": true
}
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"parameters": [
{
"id": "a30d01d0-38f1-4a91-9cf6-cdb181d676b5",
"version": "KqlParameterItem/1.0",
"name": "isT1098Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1098",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"id": "2ea28d27-88d9-4b34-896f-af0c4b3a4f83",
"version": "KqlParameterItem/1.0",
"name": "isT1136Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1136",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"id": "f81aaf9e-f762-4816-8783-5bd68387da92",
"version": "KqlParameterItem/1.0",
"name": "isT1525Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1525",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"id": "b864a970-fb05-45e0-8104-9582152381a1",
"version": "KqlParameterItem/1.0",
"name": "isT1137Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1137",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"id": "8882356a-47ca-498f-a51f-dbab21e5d17a",
"version": "KqlParameterItem/1.0",
"name": "isT1078Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1078",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "10",
"name": "Hidden Parameters"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Account Manipulation (T1098)](https://attack.mitre.org/techniques/T1098)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Additional Cloud Credentials (T1098.001)](https://attack.mitre.org/techniques/T1098/001)
\r\n🟥 ️[Exchange Email Delegate Permissions (T1098.002)](https://attack.mitre.org/techniques/T1098/002)
\r\n🟥 ️[Add Office 365 Global Administrator Role (T1098.003)](https://attack.mitre.org/techniques/T1098/003)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Multi-factor Authentication (M1032)](https://attack.mitre.org/mitigations/M1032)
\r\n🟦 [Network Segmentation (M1030)](https://attack.mitre.org/mitigations/M1030)
\r\n🟦 [Operating System Configuration(M1028)](https://attack.mitre.org/mitigations/M1028)
\r\n🟦 [Privileged Account Management (M1026)](https://attack.mitre.org/mitigations/M1026)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Multi-Factor Authentication) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n💡 [(Network Segmentation) Leverage Network Security Groups](https://docs.microsoft.com/azure/virtual-network/manage-network-security-group)
\r\n💡 [(Operating System Configuration) Tutorial: Monitor Changes and Update a Windows Virtual Machine in Azure](https://docs.microsoft.com/azure/virtual-machines/windows/tutorial-config-management)
\r\n💡 [(Privileged Account Management) Deploy Entra ID Privileged Identity Management (PIM)](https://docs.microsoft.com/azure/active-directory/privileged-identity-management)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
🔀 [Virtual Machines](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Compute%2FVirtualMachines)
\r\n🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n🔀 [Network Security Groups](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Network%2FNetworkSecurityGroups)
"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1098\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.4.*\", \"AC.5.*\", \"AC.6.*\", \"CM.5.*\", \"CM.6.*\", \"CM.7.*\", \"IA.2.*\", \"SC.7.*\", \"SI.4.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1098Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Account Manipulation",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Create Account (T1136)](https://attack.mitre.org/techniques/T1136)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Cloud Account (T1136.003)](https://attack.mitre.org/techniques/T1136/003)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Multi-factor Authentication (M1032)](https://attack.mitre.org/mitigations/M1032)
\r\n🟦 [Network Segmentation (M1030)](https://attack.mitre.org/mitigations/M1030)
\r\n🟦 [Operating System Configuration (M1028)](https://attack.mitre.org/mitigations/M1028)
\r\n🟦 [Privileged Account Management (M1026)](https://attack.mitre.org/mitigations/M1026)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Multi-Factor Authentication) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n💡 [(Network Segmentation) Leverage Network Security Groups](https://docs.microsoft.com/azure/virtual-network/manage-network-security-group)
\r\n💡 [(Operating System Configuration) Tutorial: Monitor Changes and Update a Windows Virtual Machine in Azure](https://docs.microsoft.com/azure/virtual-machines/windows/tutorial-config-management)
\r\n💡 [(Privileged Account Management) Deploy Entra ID Privileged Identity Management (PIM)](https://docs.microsoft.com/azure/active-directory/privileged-identity-management/pim-deployment-plan)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
\r\n🔀 [Privileged Identity Management](https://portal.azure.com/#blade/Microsoft_Azure_PIMCommon/CommonMenuBlade/quickStart)
\r\n🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n🔀 [Network Security Groups](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Network%2FNetworkSecurityGroups)
🔀 [Virtual Machines](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Compute%2FVirtualMachines)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-2, AC-20, AC-3, AC-4, AC-5, AC-6, CM-5, CM-6, CM-7, IA-2, IA-5, SC-7, SI-4, SI-7](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1136\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.20.*\", \"AC.3.*\", \"AC.4.*\", \"AC.5.*\", \"AC.6.*\", \"CM.5.*\", \"CM.6.*\", \"CM.7.*\", \"IA.2.*\", \"IA.5.*\", \"SC.7.*\", \"SI.4.*\", \"SI.7.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1136Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Create Account",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Implant Internal Image (T1525)](https://attack.mitre.org/techniques/T1525)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Audit (M1047)](https://attack.mitre.org/mitigations/M1047)
\r\n🟦 [Code Signing (M1045)](https://attack.mitre.org/mitigations/M1045)
\r\n🟦 [Privileged Account Management (M1026)](https://attack.mitre.org/mitigations/M1026)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Audit) Azure Security Logging and Auditing](https://docs.microsoft.com/azure/security/fundamentals/log-audit)
\r\n💡 [(Code Signing) Create and merge a CSR in Key Vault](https://docs.microsoft.com/azure/key-vault/certificates/create-certificate-signing-request)
\r\n💡 [(Privileged Account Management) Deploy Entra ID Privileged Identity Management (PIM)](https://docs.microsoft.com/azure/active-directory/privileged-identity-management/pim-deployment-plan)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
🔀 [Key Vaults](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.KeyVault%2Fvaults)
🔀 [Privileged Identity Management](https://portal.azure.com/#blade/Microsoft_Azure_PIMCommon/CommonMenuBlade/quickStart)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-2, AC-3, AC-5, AC-6, CA-8, CM-2, CM-5, CM-6, CM-7, IA-2, IA-9, RA-5, SI-2, SI-3, SI-4, SI-7](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1525\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"CA.8.*\", \"CM.2.*\", \"CM.5.*\", \"CM.6.*\", \"CM.7.*\", \"IA.2.*\", \"IA.9.*\", \"RA.5.*\", \"SI.2.*\", \"SI.3.*\", \"SI.4.*\", \"SI.7.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1525Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Implant Internal Image",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Office Application Startup (T1137)](https://attack.mitre.org/techniques/T1137)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Office Template Macros (T1137.001)](https://attack.mitre.org/techniques/T1137/001)
\r\n🟥 ️[Office Test (T1137.002)](https://attack.mitre.org/techniques/T1137/002)
\r\n🟥 ️[Outlook Forms (T1137.003)](https://attack.mitre.org/techniques/T1137/003)
\r\n🟥 ️[Outlook Home Page (T1137.004)](https://attack.mitre.org/techniques/T1137/004)
\r\n🟥 ️[Outlook Rules (T1137.005)](https://attack.mitre.org/techniques/T1137/005)
\r\n🟥 ️[Add-ins (T1137.006)](https://attack.mitre.org/techniques/T1137/006)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Disable or Remove Feature or Program (M1042)](https://attack.mitre.org/mitigations/M1042)
\r\n🟦 [Software Configuration (M1054)](https://attack.mitre.org/mitigations/M1054)
\r\n🟦 [Update Software (M1051)](https://attack.mitre.org/mitigations/M1051)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Disable or Remove Feature or Program) Deploy Microsoft Defender for Cloud Apps for Integrated Vulnerability Assessments](https://docs.microsoft.com/azure/security-center/deploy-vulnerability-assessment-vm)
\r\n💡 [(Software Configuration) Leverage Azure Automation Accounts for Updates/Patching](https://docs.microsoft.com/azure/automation/update-management/enable-from-portals)
\r\n💡 [(Update Software) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
🔀 [Automation Accounts](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Automation%2FAutomationAccounts)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-10, AC-17, AC-6, CM-2, CM-6, CM-8, RA-5, SC-18, SI-2, SI-3, SI-4, SI-8](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1137\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.10.*\", \"AC.17.*\", \"AC.6.*\", \"CM.2.*\", \"CM.6.*\", \"CM.8.*\", \"RA.5.*\", \"SC.18.*\", \"SI.2.*\", \"SI.3.*\", \"SI.4.*\", \"SI.8.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1137Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Office Application Startup",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Valid Accounts (T1078)](https://attack.mitre.org/techniques/T1078/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Default Accounts (T1078.001)](https://attack.mitre.org/techniques/T1078/001/)
\r\n🟥 ️[Cloud Accounts (T1078.004)](https://attack.mitre.org/techniques/T1078/004/)\r\n\r\n### Recommended Logs\r\n🔷 [SigninLogs](https://docs.microsoft.com/azure/azure-monitor/reference/tables/signinlogs) ✳️ [Microsoft Entra ID](https://azure.microsoft.com/services/active-directory/)
🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) 🔷 [SecurityBaselines](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securitybaseline) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Multi-Factor Authentication (M1032)](https://attack.mitre.org/mitigations/M1032)
\r\n🟦 [Application Developer Guidance (M1013)](https://attack.mitre.org/mitigations/M1013)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n🟦 [Privileged Account Management (M1026)](https://attack.mitre.org/mitigations/M1026)
\r\n🟦 [Password Policies (M1027)](https://attack.mitre.org/mitigations/M1027)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Multi-Factor Authentication) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n💡 [(Application Developer Guidance) Secure Identity with Zero Trust](https://docs.microsoft.com/security/zero-trust/identity)
\r\n💡 [(Application Developer Guidance) Secure Secrets with Azure Key Vault](https://docs.microsoft.com/azure/key-vault/general/basic-concepts)
\r\n💡 [(Privileged Account Management) Deploy Entra ID Privileged Identity Management (PIM)](https://docs.microsoft.com/azure/active-directory/privileged-identity-management/pim-deployment-plan)
\r\n💡 [(Password Policies) Password and Account Lockout Policies on Microsoft Entra ID Domain Services Managed Domains](https://docs.microsoft.com/azure/active-directory-domain-services/password-policy#)
\r\n💡 [(User Account Management) What are Entra ID access reviews?](https://docs.microsoft.com/azure/active-directory/governance/access-reviews-overview)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
\r\n🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
\r\n🔀 [Key Vaults](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.KeyVault%2Fvaults)
\r\n🔀 [Privileged Identity Management](https://portal.azure.com/#blade/Microsoft_Azure_PIMCommon/CommonMenuBlade/quickStart)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-2, AC-3, AC-5, AC-6, CA-7, CA-8, CM-5, CM-6, IA-2, IA-5, RA-5, SA-10, SA-11, SA-12, SA-15, SA-16, SA-17, SA-3, SA-4, SA-8, SC-28, SI-4](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1078\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"CA.7.*\", \"CA.8.*\", \"CM.5.*\", \"CM.6.*\", \"IA.2.*\", \"IA.5.*\", \"RA.5.*\", \"SA.10.*\", \"SA.11.*\", \"SA.12.*\", \"SA.15.*\", \"SA.16.*\", \"SA.17.*\", \"SA.3.*\", \"SA.4.*\", \"SA.8.*\", \"SC.28.*\", \"SI.4.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "let FailedAssets=SecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"password\"\r\n| where AnalyzeResult == \"Failed\"\r\n| summarize FailedAssets = makelist(Computer) by Description;\r\nlet PassedAssets=SecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"password\"\r\n| where AnalyzeResult == \"Passed\"\r\n| summarize PassedAssets = makelist(Computer) by Description;\r\nSecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"password\"\r\n| summarize\r\n Failed = countif(AnalyzeResult == \"Failed\"),\r\n Passed = countif(AnalyzeResult == \"Passed\"),\r\n Total = countif(AnalyzeResult == \"Failed\" or AnalyzeResult == \"Passed\")\r\n by Description\r\n| extend PassedControls = (Passed / todouble(Total)) * 100\r\n| join kind=fullouter(FailedAssets) on Description\r\n| join kind=fullouter(PassedAssets) on Description\r\n| project Description, Total, PassedControls, Passed, Failed, PassedAssets, FailedAssets\r\n| sort by Total, Passed desc\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 ️[Password Policies] Review Security Baselines",
"noDataMessage": "An Empty Panel Provides Opportunity To Explore Further and Implement Hardening. Controls: Confirm Licensing, Availability, and Health of Respective Offerings. Logging: Confirm Log Source is Onboarded to the Log Analytics Workspace. Time: Adjust the Time Parameter for a Larger Data-Set. ",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationDisplayName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "ControlNumber",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "AllServices",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "RecommendationState",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "!=",
"thresholdValue": "Healthy",
"representation": "3",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "success",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "count_",
"formatter": 4,
"formatOptions": {
"palette": "blue"
}
}
],
"filter": true
}
},
"customWidth": "50",
"name": "query - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "let LastObserved = SigninLogs\r\n| where ResultType == 0\r\n| summarize arg_max(TimeGenerated, *) by UserPrincipalName\r\n| project UserPrincipalName, LastSignIn=TimeGenerated;\r\nSigninLogs\r\n| extend UserProfile = strcat(\"/#blade/Microsoft_AAD_IAM/UserDetailsMenuBlade/Profile/userId/\", UserId)\r\n| where ResultType == 0\r\n| summarize count() by UserPrincipalName, UserProfile, UserId\r\n| join (LastObserved) on UserPrincipalName\r\n| project UserPrincipalName, SignInCount=count_, UserProfile, LastSignIn, UserId\r\n| sort by SignInCount desc\r\n| limit 250\r\n",
"size": 0,
"showAnalytics": true,
"title": "🟦 ️[User Account Management] Review Valid Accounts",
"noDataMessage": "An Empty Panel Provides Opportunity To Explore Further and Implement Hardening. Controls: Confirm Licensing, Availability, and Health of Respective Offerings. Logging: Confirm Log Source is Onboarded to the Log Analytics Workspace. Time: Adjust the Time Parameter for a Larger Data-Set. ",
"timeContext": {
"durationMs": 43200000
},
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "UserPrincipalName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Person",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "SignInCount",
"formatter": 4,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "UserProfile",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Entra ID User Profile >>",
"bladeOpenContext": {
"bladeName": "UserDetailsMenuBlade",
"extensionName": "Microsoft_AAD_IAM",
"bladeParameters": [
{
"name": "userId",
"source": "column",
"value": "UserId"
}
]
}
}
},
{
"columnMatch": "UserId",
"formatter": 5
},
{
"columnMatch": "count_",
"formatter": 4,
"formatOptions": {
"palette": "yellowOrangeRed"
}
}
],
"filter": true
},
"sortBy": [],
"mapSettings": {
"locInfo": "LatLong",
"locInfoColumn": "Location",
"latitude": "latitude_",
"longitude": "longitude_",
"sizeSettings": "city_",
"sizeAggregation": "Count",
"labelSettings": "city_",
"legendMetric": "city_",
"numberOfMetrics": 100,
"legendAggregation": "Count",
"itemColorSettings": {
"nodeColorField": "state_",
"colorAggregation": "Count",
"type": "heatmap",
"heatmapPalette": "coldHot"
}
}
},
"customWidth": "50",
"name": "query - 9"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1078Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Valid Accounts",
"styleSettings": {
"showBorder": true
}
}
]
},
"conditionalVisibility": {
"parameterName": "isPEVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Persistence Group"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Privilege Escalation](https://attack.mitre.org/tactics/TA0004/)\r\n---\r\nThe adversary is trying to gain higher-level permissions. Privilege Escalation consists of techniques that adversaries use to gain higher-level permissions on a system or network. Adversaries can often enter and explore a network with unprivileged access but require elevated permissions to follow through on their objectives. Common approaches are to take advantage of system weaknesses, misconfigurations, and vulnerabilities. "
},
"customWidth": "40",
"name": "text - 3"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "10",
"name": "text - 4"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "{\"version\":\"1.0.0\",\"content\":\"[\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1484] Domain Policy Modification\\\", \\\"tab\\\": \\\"T1484\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1078] Valid Accounts\\\", \\\"tab\\\": \\\"T1078\\\" }\\r\\n]\",\"transformers\":null}",
"size": 3,
"exportMultipleValues": true,
"exportedParameters": [
{
"fieldName": "tab",
"parameterName": "Tab",
"parameterType": 1
}
],
"queryType": 8,
"gridSettings": {
"formatters": [
{
"columnMatch": "Section",
"formatter": 8,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "tab",
"formatter": 5
}
]
}
},
"customWidth": "40",
"name": "Control Areas",
"styleSettings": {
"showBorder": true
}
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"parameters": [
{
"id": "a30d01d0-38f1-4a91-9cf6-cdb181d676b5",
"version": "KqlParameterItem/1.0",
"name": "isT1484Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1484",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"id": "a3610691-7141-4f1a-9f86-f01513531ec1",
"version": "KqlParameterItem/1.0",
"name": "isT1078Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1078",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "10",
"name": "Hidden Parameters"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Domain Policy Modification (T1484)](https://attack.mitre.org/techniques/T1484)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Domain Trust Modification (T1484.002)](https://attack.mitre.org/techniques/T1484/002/)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Audit (M1047)](https://attack.mitre.org/mitigations/M1047)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n🟦 [Privileged Account Management (M1026)](https://attack.mitre.org/mitigations/M1026)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Audit) Review Policy/Trust Recommendations](https://docs.microsoft.com/azure/storage/common/storage-account-keys-manage)
\r\n💡 [(Privileged Account Management) Deploy Entra ID Privileged Identity Management (PIM)](https://docs.microsoft.com/azure/active-directory/privileged-identity-management/pim-deployment-plan)
\r\n💡 [(User Account Management) Monitor User Endpoint Activity Alerts](https://docs.microsoft.com/microsoft-365/security/defender-endpoint/manage-alerts)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
🔀 [Privileged Identity Management](https://portal.azure.com/#blade/Microsoft_Azure_PIMCommon/CommonMenuBlade/quickStart)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-2, AC-3, AC-4, AC-5, AC-6, CA-8, CM-2, CM-5, CM-6, CM-7, IA-2, RA-5, SI-4](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1484\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.4.*\", \"AC.5.*\", \"AC.6.*\", \"CA.8.*\", \"CM.2.*\", \"CM.5.*\", \"CM.6.*\", \"CM.7.*\", \"IA.2.*\", \"RA.5.*\", \"SI.4.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1484Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Domain Policy Modification",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Valid Accounts (T1078)](https://attack.mitre.org/techniques/T1078/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Default Accounts (T1078.001)](https://attack.mitre.org/techniques/T1078/001/)
\r\n🟥 ️[Cloud Accounts (T1078.004)](https://attack.mitre.org/techniques/T1078/004/)\r\n\r\n### Recommended Logs\r\n🔷 [SigninLogs](https://docs.microsoft.com/azure/azure-monitor/reference/tables/signinlogs) ✳️ [Microsoft Entra ID](https://azure.microsoft.com/services/active-directory/)
🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) 🔷 [SecurityBaselines](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securitybaseline) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Multi-Factor Authentication (M1032)](https://attack.mitre.org/mitigations/M1032)
\r\n🟦 [Application Developer Guidance (M1013)](https://attack.mitre.org/mitigations/M1013)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n🟦 [Privileged Account Management (M1026)](https://attack.mitre.org/mitigations/M1026)
\r\n🟦 [Password Policies (M1027)](https://attack.mitre.org/mitigations/M1027)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Multi-Factor Authentication) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n💡 [(Application Developer Guidance) Secure Identity with Zero Trust](https://docs.microsoft.com/security/zero-trust/identity)
\r\n💡 [(Application Developer Guidance) Secure Secrets with Azure Key Vault](https://docs.microsoft.com/azure/key-vault/general/basic-concepts)
\r\n💡 [(Privileged Account Management) Deploy Entra ID Privileged Identity Management (PIM)](https://docs.microsoft.com/azure/active-directory/privileged-identity-management/pim-deployment-plan)
\r\n💡 [(Password Policies) Password and Account Lockout Policies on Microsoft Entra ID Domain Services Managed Domains](https://docs.microsoft.com/azure/active-directory-domain-services/password-policy#)
\r\n💡 [(User Account Management) What are Entra ID access reviews?](https://docs.microsoft.com/azure/active-directory/governance/access-reviews-overview)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
\r\n🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
\r\n🔀 [Key Vaults](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.KeyVault%2Fvaults)
\r\n🔀 [Privileged Identity Management](https://portal.azure.com/#blade/Microsoft_Azure_PIMCommon/CommonMenuBlade/quickStart)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-2, AC-3, AC-5, AC-6, CA-7, CA-8, CM-5, CM-6, IA-2, IA-5, RA-5, SA-10, SA-11, SA-12, SA-15, SA-16, SA-17, SA-3, SA-4, SA-8, SC-28, SI-4](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1078\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"CA.7.*\", \"CA.8.*\", \"CM.5.*\", \"CM.6.*\", \"IA.2.*\", \"IA.5.*\", \"RA.5.*\", \"SA.10.*\", \"SA.11.*\", \"SA.12.*\", \"SA.15.*\", \"SA.16.*\", \"SA.17.*\", \"SA.3.*\", \"SA.4.*\", \"SA.8.*\", \"SC.28.*\", \"SI.4.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "let FailedAssets=SecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"password\"\r\n| where AnalyzeResult == \"Failed\"\r\n| summarize FailedAssets = makelist(Computer) by Description;\r\nlet PassedAssets=SecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"password\"\r\n| where AnalyzeResult == \"Passed\"\r\n| summarize PassedAssets = makelist(Computer) by Description;\r\nSecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"password\"\r\n| summarize\r\n Failed = countif(AnalyzeResult == \"Failed\"),\r\n Passed = countif(AnalyzeResult == \"Passed\"),\r\n Total = countif(AnalyzeResult == \"Failed\" or AnalyzeResult == \"Passed\")\r\n by Description\r\n| extend PassedControls = (Passed / todouble(Total)) * 100\r\n| join kind=fullouter(FailedAssets) on Description\r\n| join kind=fullouter(PassedAssets) on Description\r\n| project Description, Total, PassedControls, Passed, Failed, PassedAssets, FailedAssets\r\n| sort by Total, Passed desc\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 ️[Password Policies] Review Security Baselines",
"noDataMessage": "An Empty Panel Provides Opportunity To Explore Further and Implement Hardening. Controls: Confirm Licensing, Availability, and Health of Respective Offerings. Logging: Confirm Log Source is Onboarded to the Log Analytics Workspace. Time: Adjust the Time Parameter for a Larger Data-Set. ",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationDisplayName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "ControlNumber",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "AllServices",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "RecommendationState",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "!=",
"thresholdValue": "Healthy",
"representation": "3",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "success",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "count_",
"formatter": 4,
"formatOptions": {
"palette": "blue"
}
}
],
"filter": true
}
},
"customWidth": "50",
"name": "query - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "let LastObserved = SigninLogs\r\n| where ResultType == 0\r\n| summarize arg_max(TimeGenerated, *) by UserPrincipalName\r\n| project UserPrincipalName, LastSignIn=TimeGenerated;\r\nSigninLogs\r\n| extend UserProfile = strcat(\"/#blade/Microsoft_AAD_IAM/UserDetailsMenuBlade/Profile/userId/\", UserId)\r\n| where ResultType == 0\r\n| summarize count() by UserPrincipalName, UserProfile, UserId\r\n| join (LastObserved) on UserPrincipalName\r\n| project UserPrincipalName, SignInCount=count_, UserProfile, LastSignIn, UserId\r\n| sort by SignInCount desc\r\n| limit 250\r\n",
"size": 0,
"showAnalytics": true,
"title": "🟦 ️[User Account Management] Review Valid Accounts",
"noDataMessage": "An Empty Panel Provides Opportunity To Explore Further and Implement Hardening. Controls: Confirm Licensing, Availability, and Health of Respective Offerings. Logging: Confirm Log Source is Onboarded to the Log Analytics Workspace. Time: Adjust the Time Parameter for a Larger Data-Set. ",
"timeContext": {
"durationMs": 43200000
},
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "UserPrincipalName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Person",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "SignInCount",
"formatter": 4,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "UserProfile",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Entra ID User Profile >>",
"bladeOpenContext": {
"bladeName": "UserDetailsMenuBlade",
"extensionName": "Microsoft_AAD_IAM",
"bladeParameters": [
{
"name": "userId",
"source": "column",
"value": "UserId"
}
]
}
}
},
{
"columnMatch": "UserId",
"formatter": 5
},
{
"columnMatch": "count_",
"formatter": 4,
"formatOptions": {
"palette": "yellowOrangeRed"
}
}
],
"filter": true
},
"sortBy": [],
"mapSettings": {
"locInfo": "LatLong",
"locInfoColumn": "Location",
"latitude": "latitude_",
"longitude": "longitude_",
"sizeSettings": "city_",
"sizeAggregation": "Count",
"labelSettings": "city_",
"legendMetric": "city_",
"numberOfMetrics": 100,
"legendAggregation": "Count",
"itemColorSettings": {
"nodeColorField": "state_",
"colorAggregation": "Count",
"type": "heatmap",
"heatmapPalette": "coldHot"
}
}
},
"customWidth": "50",
"name": "query - 9"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1078Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Valid Accounts",
"styleSettings": {
"showBorder": true
}
}
]
},
"conditionalVisibility": {
"parameterName": "isPRVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Privilege Escalation"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Defense Evasion](https://attack.mitre.org/tactics/TA0005/) \r\n---\r\nThe adversary is trying to avoid being detected. Defense Evasion consists of techniques that adversaries use to avoid detection throughout their compromise. Techniques used for defense evasion include uninstalling/disabling security software or obfuscating/encrypting data and scripts. Adversaries also leverage and abuse trusted processes to hide and masquerade their malware. Other tactics’ techniques are cross-listed here when those techniques include the added benefit of subverting defenses.\r\n"
},
"customWidth": "40",
"name": "Defense Evasion Guide"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "10",
"name": "text - 7"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "{\"version\":\"1.0.0\",\"content\":\"[\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1484] Domain Policy Modification\\\", \\\"tab\\\": \\\"T1484\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1564] Hide Artifacts\\\", \\\"tab\\\": \\\"T1564\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1562] Impair Defenses\\\", \\\"tab\\\": \\\"T1562\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1578] Modify Cloud Compute Infrastructure\\\", \\\"tab\\\": \\\"T1578\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1535] Unused/Unsupported Cloud Regions\\\", \\\"tab\\\": \\\"T1535\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1550] Use Alternate Authentication Material\\\", \\\"tab\\\": \\\"T1550\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1078] Valid Accounts\\\", \\\"tab\\\": \\\"T1078\\\" }\\r\\n\\r\\n]\",\"transformers\":null}",
"size": 3,
"exportMultipleValues": true,
"exportedParameters": [
{
"fieldName": "tab",
"parameterName": "Tab",
"parameterType": 1
}
],
"queryType": 8,
"gridSettings": {
"formatters": [
{
"columnMatch": "Section",
"formatter": 8,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "tab",
"formatter": 5
}
]
}
},
"customWidth": "40",
"name": "Control Areas",
"styleSettings": {
"showBorder": true
}
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"parameters": [
{
"id": "a30d01d0-38f1-4a91-9cf6-cdb181d676b5",
"version": "KqlParameterItem/1.0",
"name": "isT1484Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1484",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1564Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1564",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "2306e2ea-050d-44b9-983a-bc27ab113f6e"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1562Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1562",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "3ac68dca-28dd-4642-ba4d-a3ca52728f07"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1578Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1578",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "d71f5806-15ef-4bbd-950d-46ea034adf43"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1535Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1535",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "ded47c33-0218-442b-9f19-0e6752cd88d6"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1550Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1550",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "ad93283f-e9bb-45f8-9e14-54b4ef5f2843"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1078Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1078",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "3dd218d6-5aac-488c-a2c5-bdaf83d85181"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "10",
"name": "Hidden Parameters"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Domain Policy Modification (T1484)](https://attack.mitre.org/techniques/T1484)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Domain Trust Modification (T1484.002)](https://attack.mitre.org/techniques/T1484/002/)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Audit (M1047)](https://attack.mitre.org/mitigations/M1047)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n🟦 [Privileged Account Management (M1026)](https://attack.mitre.org/mitigations/M1026)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Audit) Review Policy/Trust Recommendations](https://docs.microsoft.com/azure/storage/common/storage-account-keys-manage)
\r\n💡 [(Privileged Account Management) Deploy Entra ID Privileged Identity Management (PIM)](https://docs.microsoft.com/azure/active-directory/privileged-identity-management/pim-deployment-plan)
\r\n💡 [(User Account Management) Monitor User Endpoint Activity Alerts](https://docs.microsoft.com/microsoft-365/security/defender-endpoint/manage-alerts)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
🔀 [Privileged Identity Management](https://portal.azure.com/#blade/Microsoft_Azure_PIMCommon/CommonMenuBlade/quickStart)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-2, AC-3, AC-4, AC-5, AC-6, CA-8, CM-2, CM-5, CM-6, CM-7, IA-2, RA-5, SI-4](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1484\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.4.*\", \"AC.5.*\", \"AC.6.*\", \"CA.8.*\", \"CM.2.*\", \"CM.5.*\", \"CM.6.*\", \"CM.7.*\", \"IA.2.*\", \"RA.5.*\", \"SI.4.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1484Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Domain Policy Modification",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Hide Artifacts (T1564)](https://attack.mitre.org/techniques/T1564)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Hidden Files & Directories (T1564.001)](https://attack.mitre.org/techniques/T1564/001/)
\r\n🟥 ️[Hidden Users (T1564.002)](https://attack.mitre.org/techniques/T1564/002/)
\r\n🟥 ️[Hidden Window (T1564.003)](https://attack.mitre.org/techniques/T1564/003/)
\r\n🟥 ️[NTFS File Attributes (T1564.004)](https://attack.mitre.org/techniques/T1564/004/)
\r\n🟥 ️[Hidden File System (T1564.005)](https://attack.mitre.org/techniques/T1564/005/)
\r\n🟥 ️[Run Virtual Instance (T1564.006)](https://attack.mitre.org/techniques/T1564/006/)
\r\n🟥 ️[VBA Stomping (T1564.007)](https://attack.mitre.org/techniques/T1564/007/)
\r\n🟥 ️[Email Hiding Rules (T1564.008)](https://attack.mitre.org/techniques/T1564/008/)
\r\n🟥 ️[Resource Forking (T1564.009)](https://attack.mitre.org/techniques/T1564/009/)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityBaselines](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securitybaseline) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigations\r\n🟦 [This type of attack technique cannot be easily mitigated with preventive controls since it is based on the abuse of system features.](https://attack.mitre.org/techniques/T1564/)\r\n\r\n### Microsoft Recommendations\r\n💡 [Apply Azure security baselines to machines](https://docs.microsoft.com/azure/defender-for-cloud/apply-security-baseline)
\r\n💡 [Start using Privileged Identity Management](https://docs.microsoft.com/azure/active-directory/privileged-identity-management/pim-getting-started)
\r\n\r\n### Microsoft Portals\r\n🔀 [Security Baselines](https://portal.azure.com/#blade/Microsoft_Intune_DeviceSettings/MemRedirectBlade)
🔀 [Privileged Identity Management](https://portal.azure.com/#blade/Microsoft_Azure_PIMCommon/CommonMenuBlade/quickStart)
🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[N/A](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1564\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "let FailedAssets=SecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"hid\" or Description contains \"fork\" or Description contains \"root\" or Description contains \"VBA\" or Description contains \"/Resources\" or Description contains \"bypass\" or Description contains \"xattr\" or Description contains \"-l@\" or Description contains \"'.'\" or Description contains \"attrib\" or Description contains \"500Users\" or Description contains \"SpecialAccount\" or Description contains \"MFT\" or Description contains \"disk sector\" or Description contains \"partition\" or Description contains \"boot\" or Description contains \"binaries\" or Description contains \"hyper\" or Description contains \"virtual\" or Description contains \"performancecache\" or Description contains \"inboxrule\"\r\n| where AnalyzeResult == \"Failed\"\r\n| summarize FailedAssets = makelist(Computer) by Description;\r\nlet PassedAssets=SecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"hid\" or Description contains \"fork\" or Description contains \"root\" or Description contains \"VBA\" or Description contains \"/Resources\" or Description contains \"bypass\" or Description contains \"xattr\" or Description contains \"-l@\" or Description contains \"'.'\" or Description contains \"attrib\" or Description contains \"500Users\" or Description contains \"SpecialAccount\" or Description contains \"MFT\" or Description contains \"disk sector\" or Description contains \"partition\" or Description contains \"boot\" or Description contains \"binaries\" or Description contains \"hyper\" or Description contains \"virtual\" or Description contains \"performancecache\" or Description contains \"inboxrule\"\r\n| where AnalyzeResult == \"Passed\"\r\n| summarize PassedAssets = makelist(Computer) by Description;\r\nSecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"hid\" or Description contains \"fork\" or Description contains \"root\" or Description contains \"VBA\" or Description contains \"/Resources\" or Description contains \"bypass\" or Description contains \"xattr\" or Description contains \"-l@\" or Description contains \"'.'\" or Description contains \"attrib\" or Description contains \"500Users\" or Description contains \"SpecialAccount\" or Description contains \"MFT\" or Description contains \"disk sector\" or Description contains \"partition\" or Description contains \"boot\" or Description contains \"binaries\" or Description contains \"hyper\" or Description contains \"virtual\" or Description contains \"performancecache\" or Description contains \"inboxrule\"\r\n| summarize\r\n Failed = countif(AnalyzeResult == \"Failed\"),\r\n Passed = countif(AnalyzeResult == \"Passed\"),\r\n Total = countif(AnalyzeResult == \"Failed\" or AnalyzeResult == \"Passed\")\r\n by Description\r\n| extend PassedControls = (Passed / todouble(Total)) * 100\r\n| join kind=fullouter(FailedAssets) on Description\r\n| join kind=fullouter(PassedAssets) on Description\r\n| project Description, Total, PassedControls, Passed, Failed, PassedAssets, FailedAssets\r\n| sort by Total, Passed desc\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Configure Security Baselines",
"noDataMessage": "An Empty Panel Provides Opportunity To Explore Further and Implement Hardening. Controls: Confirm Licensing, Availability, and Health of Respective Offerings. Logging: Confirm Log Source is Onboarded to the Log Analytics Workspace. Time: Adjust the Time Parameter for a Larger Data-Set. ",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Description",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationDisplayName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlNumber",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "AllServices",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "RecommendationState",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "!=",
"thresholdValue": "Healthy",
"representation": "3",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "success",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "count_",
"formatter": 4,
"formatOptions": {
"palette": "blue"
}
}
],
"filter": true
}
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1564Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Hide Artifacts",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Impair Defenses (T1562)](https://attack.mitre.org/techniques/T1562)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Disable or Modify Tools (T1562.001)](https://attack.mitre.org/techniques/T1562/001)
\r\n🟥 ️[Disable or Modify Cloud Firewall (T1562.007)](https://attack.mitre.org/techniques/T1562/007)
\r\n🟥 ️[Disable Cloud Logs (T1562.008)](https://attack.mitre.org/techniques/T1562/008)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Restrict File and Directory Permissions (M1022)](https://attack.mitre.org/mitigations/M1022)
\r\n🟦 [Restrict Registry Permissions (M1024)](https://attack.mitre.org/mitigations/M1024)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Restrict File and Directory Permissions) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n💡 [(Restrict Registry Permissions) File integrity monitoring in Microsoft Defender for Cloud Apps](https://docs.microsoft.com/azure/security-center/security-center-file-integrity-monitoring)
\r\n💡 [(User Account Management) What are Entra ID access reviews?](https://docs.microsoft.com/azure/active-directory/governance/access-reviews-overview)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Entra ID: Access Reviews](https://portal.azure.com/#blade/Microsoft_AAD_ERM/DashboardBlade/Controls)
\r\n🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
🔀 [Azure Information Protection](https://portal.azure.com/#blade/Microsoft_Azure_InformationProtection/DataClassGroupEditBlade/quickstartBlade)
\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-2, AC-3, AC-5, AC-6, CA-7, CA-8, CM-2, CM-5, CM-6, CM-7, IA-2, IA-4, RA-5, SI-3, SI-4, SI-7](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1562\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"CA.7.*\", \"CA.8.*\", \"CM.2.*\", \"CM.5.*\", \"CM.6.*\", \"CM.7.*\", \"IA.2.*\", \"IA.4.*\", \"RA.5.*\", \"SI.3.*\", \"SI.4.*\", \"SI.7.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1562Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Impair Defenses",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Modify Cloud Compute Infrastructure (T1578)](https://attack.mitre.org/techniques/T1578/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Create Snapshot (T1578.001)](https://attack.mitre.org/techniques/T1578/001)
\r\n🟥 ️[Create Cloud Instance (T1578.002)](https://attack.mitre.org/techniques/T1578/002)
\r\n🟥 ️[Delete Cloud Instance(T1578.003)](https://attack.mitre.org/techniques/T1578/003)
\r\n🟥 ️[Revert Cloud Instance (T1578.004)](https://attack.mitre.org/techniques/T1578/004)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Audit (M1047)](https://attack.mitre.org/mitigations/M1047)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Audit) Azure Security Logging and Auditing](https://docs.microsoft.com/azure/security/fundamentals/log-audit)
\r\n💡 [(User Account Management) What are Entra ID access reviews?](https://docs.microsoft.com/azure/active-directory/governance/access-reviews-overview)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview) \r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-2, AC-3, AC-5, AC-6, CA-8, CM-5, IA-2, IA-4, IA-6, RA-5, SI-4](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1578\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"CA.8.*\", \"CM.5.*\", \"IA.2.*\", \"IA.4.*\", \"IA.6.*\", \"RA.5.*\", \"SI.4.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1578Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Modify Cloud Compute Infrastructure",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Unused/Unsupported Cloud Regions (T1535)](https://attack.mitre.org/techniques/T1535/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Software Configuration (M1054)](https://attack.mitre.org/mitigations/M1054)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Software Configuration) How to Create Azure Monitor Alerts for Non-Compliant Azure Policies](https://techcommunity.microsoft.com/t5/itops-talk-blog/how-to-create-azure-monitor-alerts-for-non-compliant-azure/ba-p/713466)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Azure Policy](https://portal.azure.com/#blade/Microsoft_Azure_Policy/PolicyMenuBlade/Overview)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1535\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where RecommendationName contains \"session\" or RecommendationName contains \"identifier\" or RecommendationName contains \"certificate\"\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1535Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Unused/Unsupported Cloud Regions",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Use Alternate Authentication Material (T1550)](https://attack.mitre.org/techniques/T1550/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Application Access Token (T1550.001)](https://attack.mitre.org/techniques/T1550/001)
\r\n🟥 ️[Web Session Cookie (T1550.004)](https://attack.mitre.org/techniques/T1550/004)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Privileged Account Management (M1026)](https://attack.mitre.org/mitigations/M1026)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Privileged Account Management) Deploy Entra ID Privileged Identity Management (PIM)](https://docs.microsoft.com/azure/active-directory/privileged-identity-management/pim-deployment-plan)
\r\n💡 [(User Account Management) Review Access Recommendations](https://docs.microsoft.com/azure/storage/common/storage-account-keys-manage)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
🔀 [Privileged Identity Management](https://portal.azure.com/#blade/Microsoft_Azure_PIMCommon/CommonMenuBlade/quickStart)
"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1550\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"CM.5.*\", \"CM.6.*\", \"IA.2.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1550Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Use Alternate Authentication Material",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Valid Accounts (T1078)](https://attack.mitre.org/techniques/T1078/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Default Accounts (T1078.001)](https://attack.mitre.org/techniques/T1078/001/)
\r\n🟥 ️[Cloud Accounts (T1078.004)](https://attack.mitre.org/techniques/T1078/004/)\r\n\r\n### Recommended Logs\r\n🔷 [SigninLogs](https://docs.microsoft.com/azure/azure-monitor/reference/tables/signinlogs) ✳️ [Microsoft Entra ID](https://azure.microsoft.com/services/active-directory/)
🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) 🔷 [SecurityBaselines](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securitybaseline) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Multi-Factor Authentication (M1032)](https://attack.mitre.org/mitigations/M1032)
\r\n🟦 [Application Developer Guidance (M1013)](https://attack.mitre.org/mitigations/M1013)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n🟦 [Privileged Account Management (M1026)](https://attack.mitre.org/mitigations/M1026)
\r\n🟦 [Password Policies (M1027)](https://attack.mitre.org/mitigations/M1027)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Multi-Factor Authentication) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n💡 [(Application Developer Guidance) Secure Identity with Zero Trust](https://docs.microsoft.com/security/zero-trust/identity)
\r\n💡 [(Application Developer Guidance) Secure Secrets with Azure Key Vault](https://docs.microsoft.com/azure/key-vault/general/basic-concepts)
\r\n💡 [(Privileged Account Management) Deploy Entra ID Privileged Identity Management (PIM)](https://docs.microsoft.com/azure/active-directory/privileged-identity-management/pim-deployment-plan)
\r\n💡 [(Password Policies) Password and Account Lockout Policies on Microsoft Entra ID Domain Services Managed Domains](https://docs.microsoft.com/azure/active-directory-domain-services/password-policy#)
\r\n💡 [(User Account Management) What are Entra ID access reviews?](https://docs.microsoft.com/azure/active-directory/governance/access-reviews-overview)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
\r\n🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
\r\n🔀 [Key Vaults](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.KeyVault%2Fvaults)
\r\n🔀 [Privileged Identity Management](https://portal.azure.com/#blade/Microsoft_Azure_PIMCommon/CommonMenuBlade/quickStart)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-2, AC-3, AC-5, AC-6, CA-7, CA-8, CM-5, CM-6, IA-2, IA-5, RA-5, SA-10, SA-11, SA-12, SA-15, SA-16, SA-17, SA-3, SA-4, SA-8, SC-28, SI-4](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1078\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"CA.7.*\", \"CA.8.*\", \"CM.5.*\", \"CM.6.*\", \"IA.2.*\", \"IA.5.*\", \"RA.5.*\", \"SA.10.*\", \"SA.11.*\", \"SA.12.*\", \"SA.15.*\", \"SA.16.*\", \"SA.17.*\", \"SA.3.*\", \"SA.4.*\", \"SA.8.*\", \"SC.28.*\", \"SI.4.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "let FailedAssets=SecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"password\"\r\n| where AnalyzeResult == \"Failed\"\r\n| summarize FailedAssets = makelist(Computer) by Description;\r\nlet PassedAssets=SecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"password\"\r\n| where AnalyzeResult == \"Passed\"\r\n| summarize PassedAssets = makelist(Computer) by Description;\r\nSecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"password\"\r\n| summarize\r\n Failed = countif(AnalyzeResult == \"Failed\"),\r\n Passed = countif(AnalyzeResult == \"Passed\"),\r\n Total = countif(AnalyzeResult == \"Failed\" or AnalyzeResult == \"Passed\")\r\n by Description\r\n| extend PassedControls = (Passed / todouble(Total)) * 100\r\n| join kind=fullouter(FailedAssets) on Description\r\n| join kind=fullouter(PassedAssets) on Description\r\n| project Description, Total, PassedControls, Passed, Failed, PassedAssets, FailedAssets\r\n| sort by Total, Passed desc\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 ️[Password Policies] Review Security Baselines",
"noDataMessage": "An Empty Panel Provides Opportunity To Explore Further and Implement Hardening. Controls: Confirm Licensing, Availability, and Health of Respective Offerings. Logging: Confirm Log Source is Onboarded to the Log Analytics Workspace. Time: Adjust the Time Parameter for a Larger Data-Set. ",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationDisplayName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "ControlNumber",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "AllServices",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "RecommendationState",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "!=",
"thresholdValue": "Healthy",
"representation": "3",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "success",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "count_",
"formatter": 4,
"formatOptions": {
"palette": "blue"
}
}
],
"filter": true
}
},
"customWidth": "50",
"name": "query - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "let LastObserved = SigninLogs\r\n| where ResultType == 0\r\n| summarize arg_max(TimeGenerated, *) by UserPrincipalName\r\n| project UserPrincipalName, LastSignIn=TimeGenerated;\r\nSigninLogs\r\n| extend UserProfile = strcat(\"/#blade/Microsoft_AAD_IAM/UserDetailsMenuBlade/Profile/userId/\", UserId)\r\n| where ResultType == 0\r\n| summarize count() by UserPrincipalName, UserProfile, UserId\r\n| join (LastObserved) on UserPrincipalName\r\n| project UserPrincipalName, SignInCount=count_, UserProfile, LastSignIn, UserId\r\n| sort by SignInCount desc\r\n| limit 250\r\n",
"size": 0,
"showAnalytics": true,
"title": "🟦 ️[User Account Management] Review Valid Accounts",
"noDataMessage": "An Empty Panel Provides Opportunity To Explore Further and Implement Hardening. Controls: Confirm Licensing, Availability, and Health of Respective Offerings. Logging: Confirm Log Source is Onboarded to the Log Analytics Workspace. Time: Adjust the Time Parameter for a Larger Data-Set. ",
"timeContext": {
"durationMs": 43200000
},
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "UserPrincipalName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Person",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "SignInCount",
"formatter": 4,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "UserProfile",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Entra ID User Profile >>",
"bladeOpenContext": {
"bladeName": "UserDetailsMenuBlade",
"extensionName": "Microsoft_AAD_IAM",
"bladeParameters": [
{
"name": "userId",
"source": "column",
"value": "UserId"
}
]
}
}
},
{
"columnMatch": "UserId",
"formatter": 5
},
{
"columnMatch": "count_",
"formatter": 4,
"formatOptions": {
"palette": "yellowOrangeRed"
}
}
],
"filter": true
},
"sortBy": [],
"mapSettings": {
"locInfo": "LatLong",
"locInfoColumn": "Location",
"latitude": "latitude_",
"longitude": "longitude_",
"sizeSettings": "city_",
"sizeAggregation": "Count",
"labelSettings": "city_",
"legendMetric": "city_",
"numberOfMetrics": 100,
"legendAggregation": "Count",
"itemColorSettings": {
"nodeColorField": "state_",
"colorAggregation": "Count",
"type": "heatmap",
"heatmapPalette": "coldHot"
}
}
},
"customWidth": "50",
"name": "query - 9"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1078Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Valid Accounts",
"styleSettings": {
"showBorder": true
}
}
]
},
"conditionalVisibility": {
"parameterName": "isDEVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Defense Evasion Group"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Credential Access](https://attack.mitre.org/tactics/TA0006/)\r\n---\r\nThe adversary is trying to steal account names and passwords. Credential Access consists of techniques for stealing credentials like account names and passwords. Techniques used to get credentials include keylogging or credential dumping. Using legitimate credentials can give adversaries access to systems, make them harder to detect, and provide the opportunity to create more accounts to help achieve their goals."
},
"customWidth": "40",
"name": "text - 3"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "10",
"name": "text - 8"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "{\"version\":\"1.0.0\",\"content\":\"[\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1110] Brute Force\\\", \\\"tab\\\": \\\"T1110\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1606] Forge Web Credentials\\\", \\\"tab\\\": \\\"T1606\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1528] Steal Application Access Token\\\", \\\"tab\\\": \\\"T1528\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1539] Steal Web Session Cookie\\\", \\\"tab\\\": \\\"T1539\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1552] Unsecured Credentials\\\", \\\"tab\\\": \\\"T1552\\\" }\\r\\n]\",\"transformers\":null}",
"size": 3,
"exportMultipleValues": true,
"exportedParameters": [
{
"fieldName": "tab",
"parameterName": "Tab",
"parameterType": 1
}
],
"queryType": 8,
"gridSettings": {
"formatters": [
{
"columnMatch": "Section",
"formatter": 8,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "tab",
"formatter": 5
}
]
}
},
"customWidth": "40",
"name": "Control Areas",
"styleSettings": {
"showBorder": true
}
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"parameters": [
{
"id": "a30d01d0-38f1-4a91-9cf6-cdb181d676b5",
"version": "KqlParameterItem/1.0",
"name": "isT1110Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1110",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1606Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1606",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "f677db81-bdc9-4ef8-a2f1-b39d01c48769"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1528Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1528",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "23ac827a-8636-454c-a89e-41cc465ff0ff"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1539Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1539",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "6cacd1b3-c55f-48e1-85bd-a9540e34a6b5"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1552Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1552",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "eda72a9e-2ce6-4579-9375-be835cf960d8"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "10",
"name": "Hidden Parameters"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Brute Force (T1110)](https://attack.mitre.org/techniques/T1110/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Password Guessing (T1110.001)](https://attack.mitre.org/techniques/T1110/001)
\r\n🟥 ️[Password Cracking (T1110.002)](https://attack.mitre.org/techniques/T1110/002)
\r\n🟥 ️[Password Spraying (T1110.003)](https://attack.mitre.org/techniques/T1110/003)
\r\n🟥 ️[Credential Stuffing (T1110.004)](https://attack.mitre.org/techniques/T1110/004)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Account Use Policies (M1036)](https://attack.mitre.org/mitigations/M1036)
\r\n🟦 [Multi-factor Authentication (M1032)](https://attack.mitre.org/mitigations/M1032)
\r\n🟦 [Password Policies (M1027)](https://attack.mitre.org/mitigations/M1027)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Account Use Policies) How to Create Azure Monitor Alerts for Non-Compliant Azure Policies](https://techcommunity.microsoft.com/t5/itops-talk-blog/how-to-create-azure-monitor-alerts-for-non-compliant-azure/ba-p/713466)
\r\n💡 [(Multi-Factor Authentication) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n💡 [(Password Policies) Password and Account Lockout Policies on Microsoft Entra ID Domain Services Managed Domains](https://docs.microsoft.com/azure/active-directory-domain-services/password-policy#)
\r\n💡 [(User Account Management) Review Access Recommendations](https://docs.microsoft.com/azure/storage/common/storage-account-keys-manage)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Azure Policy](https://portal.azure.com/#blade/Microsoft_Azure_Policy/PolicyMenuBlade/Overview)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-2, AC-20, AC-3, AC-5, AC-6, AC-7, CA-7, CM-2, CM-6, IA-11, IA-2, IA-4, IA-5, SI-4](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1110\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.20.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"AC.7.*\", \"CA.7.*\", \"CM.2.*\", \"CM.6.*\", \"IA.11.*\", \"IA.2.*\", \"IA.4.*\", \"IA.5.*\", \"SI.4.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1110Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Brute Force",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Forge Web Credentials (T1606)](https://attack.mitre.org/techniques/T1606/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Web Cookies (T1606.001)](https://attack.mitre.org/techniques/T1606/001)
\r\n🟥 ️[SAML tokens (T1606.002)](https://attack.mitre.org/techniques/T1606/002)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Audit (M1047)](https://attack.mitre.org/mitigations/M1047)
\r\n🟦 [Privileged Account Management (M1026)](https://attack.mitre.org/mitigations/M1026)
\r\n🟦 [Software Configuration (M1054)](https://attack.mitre.org/mitigations/M1054)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Audit) Azure Security Logging and Auditing](https://docs.microsoft.com/azure/security/fundamentals/log-audit)
\r\n💡 [(Privileged Account Management) Deploy Entra ID Privileged Identity Management (PIM)](https://docs.microsoft.com/azure/active-directory/privileged-identity-management/pim-deployment-plan)
\r\n💡 [(Software Configuration) How to Create Azure Monitor Alerts for Non-Compliant Azure Policies](https://techcommunity.microsoft.com/t5/itops-talk-blog/how-to-create-azure-monitor-alerts-for-non-compliant-azure/ba-p/713466)
\r\n💡 [(User Account Management) What are Entra ID access reviews?](https://docs.microsoft.com/azure/active-directory/governance/access-reviews-overview)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-2, AC-3, AC-5, AC-6, MA-5, SC-17, SI-2](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1606\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"MA.5.*\", \"SC.17.*\", \"SI.2.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1606Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Forge Web Credentials",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Steal Application Access Token (T1528)](https://attack.mitre.org/techniques/T1528/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Audit (M1047)](https://attack.mitre.org/mitigations/M1047)
\r\n🟦 [Restrict Web-Based Content (M1021)](https://attack.mitre.org/mitigations/M1021)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n🟦 [User Training (M1017)](https://attack.mitre.org/mitigations/M1017)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Audit) Azure Security Logging and Auditing](https://docs.microsoft.com/azure/security/fundamentals/log-audit)
\r\n💡 [(Restrict Web-Based Content) Deploy Microsoft Defender for Endpoint](https://docs.microsoft.com/microsoft-365/security/defender-endpoint/deployment-phases)
\r\n💡 [(User Account Management) What are Entra ID access reviews?](https://docs.microsoft.com/azure/active-directory/governance/access-reviews-overview)
\r\n💡 [(User Training) Leverage Microsoft Learn for Security Training](https://docs.microsoft.com/learn/browse/?terms=security%20threat)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-10, AC-2, AC-3, AC-4, AC-5, AC-6, CA-7, CA-8, CM-2, CM-5, CM-6, IA-2, IA-4, IA-5, IA-8, RA-5, SA-11, SA-15, SI-4](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1528\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"MA.5.*\", \"SC.17.*\", \"SI.2.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1528Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Steal Application Access Token",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Steal Web Session Cookie (T1539)](https://attack.mitre.org/techniques/T1539/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Multi-factor Authentication (M1032)](https://attack.mitre.org/mitigations/M1032)
\r\n🟦 [Software Configuration (M1054)](https://attack.mitre.org/mitigations/M1054)
\r\n🟦 [User Training (M1017)](https://attack.mitre.org/mitigations/M1017)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Multi-Factor Authentication) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n💡 [(Software Configuration) How to Create Azure Monitor Alerts for Non-Compliant Azure Policies](https://techcommunity.microsoft.com/t5/itops-talk-blog/how-to-create-azure-monitor-alerts-for-non-compliant-azure/ba-p/713466)
\r\n💡 [(User Training) Leverage Microsoft Learn for Security Training](https://docs.microsoft.com/learn/browse/?terms=security%20threat)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Azure Policy](https://portal.azure.com/#blade/Microsoft_Azure_Policy/PolicyMenuBlade/Overview)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-20, AC-3, AC-6, CA-7, CM-2, CM-6, IA-2, IA-5, SI-3, SI-4](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1539\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.20.*\", \"AC.3.*\", \"AC.6.*\", \"CA.7.*\", \"CM.2.*\", \"CM.6.*\", \"IA.2.*\", \"IA.5.*\", \"SI.3.*\", \"SI.4.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1539Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Steal Web Session Cookie",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Unsecured Credentials (T1552)](https://attack.mitre.org/techniques/T1552/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Credentials in Files (T1552.001)](https://attack.mitre.org/techniques/T1552/001)
\r\n🟥 ️[Cloud Instance Metadata API (T1552.005)](https://attack.mitre.org/techniques/T1552/005)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Active Directory Configuration (M1015)](https://attack.mitre.org/mitigations/M1015)
\r\n🟦 [Audit (M1047)](https://attack.mitre.org/mitigations/M1047)
\r\n🟦 [Encrypt Sensitive Information (M1041)](https://attack.mitre.org/mitigations/M1041)
\r\n🟦 [Filter Network Traffic (M1037)](https://attack.mitre.org/mitigations/M1037)
\r\n🟦 [Operating System Configuration (M1028)](https://attack.mitre.org/mitigations/M1028)
\r\n🟦 [Password Policies (M1027)](https://attack.mitre.org/mitigations/M1027)
\r\n🟦 [Privileged Account Management (M1026)](https://attack.mitre.org/mitigations/M1026)
\r\n🟦 [Restrict File and Directory Permissions (M1022)](https://attack.mitre.org/mitigations/M1022)
\r\n🟦 [Update Software (M1051)](https://attack.mitre.org/mitigations/M1051)
\r\n🟦 [User Training (M1017)](https://attack.mitre.org/mitigations/M1017)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Secure Credentials) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n💡 [(Secure Credentials) Secure Identity with Zero Trust](https://docs.microsoft.com/security/zero-trust/identity)
\r\n💡 [(Secure Credentials) Secure Secrets with Azure Key Vault](https://docs.microsoft.com/azure/key-vault/general/basic-concepts)
\r\n\r\n### Microsoft Portals \r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
🔀 [Key Vault](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.KeyVault%2Fvaults)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-16, AC-17, AC-18, AC-19, AC-2, AC-20, AC-3, AC-4, AC-5, AC-6, CA-7, CA-8, CM-2, CM-5, CM-6, CM-7, IA-2, IA-3, IA-4, IA-5, RA-5, SA-11, SA-15, SC-12, SC-28, SC-4, SC-7, SI-10, SI-12, SI-15, SI-2, SI-4, SI-7](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1552\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.16.*\", \"AC.17.*\", \"AC.18.*\", \"AC.19.*\", \"AC.2.*\", \"AC.20.*\", \"AC.3.*\", \"AC.4.*\", \"AC.5.*\", \"AC.6.*\", \"CA.7.*\", \"CA.8.*\", \"CM.2.*\", \"CM.5.*\", \"CM.6.*\", \"CM.7.*\", \"IA.2.*\", \"IA.3.*\", \"IA.4.*\", \"IA.5.*\", \"RA.5.*\", \"SA.11.*\", \"SA.15.*\", \"SC.12.*\", \"SC.28.*\", \"SC.4.*\", \"SC.7.*\", \"SI.10.*\", \"SI.12.*\", \"SI.15.*\", \"SI.2.*\", \"SI.4.*\", \"SI.7.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1552Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Unsecured Credentials",
"styleSettings": {
"showBorder": true
}
}
]
},
"conditionalVisibility": {
"parameterName": "isCRVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Credential Access Group"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Discovery](https://attack.mitre.org/tactics/TA0007/) \r\n---\r\nThe adversary is trying to figure out your environment. Discovery consists of techniques an adversary may use to gain knowledge about the system and internal network. These techniques help adversaries observe the environment and orient themselves before deciding how to act. They also allow adversaries to explore what they can control and what’s around their entry point in order to discover how it could benefit their current objective. Native operating system tools are often used toward this post-compromise information-gathering objective.\r\n"
},
"customWidth": "40",
"name": "Discovery Guide"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "10",
"name": "text - 13"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "{\"version\":\"1.0.0\",\"content\":\"[\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1087] Account Discovery\\\", \\\"tab\\\": \\\"T1087\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1580] Cloud Infrastructure Discovery\\\", \\\"tab\\\": \\\"T1580\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1538] Cloud Service Dashboard\\\", \\\"tab\\\": \\\"T1538\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1526] Cloud Service Discovery\\\", \\\"tab\\\": \\\"T1526\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1619] Cloud Storage Object Discovery\\\", \\\"tab\\\": \\\"T1619\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1046] Network Service Scanning\\\", \\\"tab\\\": \\\"T1046\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1201] Password Policy Discovery\\\", \\\"tab\\\": \\\"T1201\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1069] Permission Groups Discovery\\\", \\\"tab\\\": \\\"T1069\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1518] Software Discovery\\\", \\\"tab\\\": \\\"T1518\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1082] System Information Discovery\\\", \\\"tab\\\": \\\"T1082\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1614] System Location Discovery\\\", \\\"tab\\\": \\\"T1614\\\" }\\r\\n]\",\"transformers\":null}",
"size": 3,
"exportMultipleValues": true,
"exportedParameters": [
{
"fieldName": "tab",
"parameterName": "Tab",
"parameterType": 1
}
],
"queryType": 8,
"gridSettings": {
"formatters": [
{
"columnMatch": "Section",
"formatter": 8,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "tab",
"formatter": 5
}
]
}
},
"customWidth": "40",
"name": "Control Areas",
"styleSettings": {
"showBorder": true
}
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"parameters": [
{
"id": "a30d01d0-38f1-4a91-9cf6-cdb181d676b5",
"version": "KqlParameterItem/1.0",
"name": "isT1087Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1087",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1580Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1580",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "caa686e8-215f-427f-983d-24806136c254"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1538Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1538",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "3994ae3f-1c37-4dc9-852f-984ace8ad4bd"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1526Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1526",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "a8d734da-9c7d-42f3-8f84-1665c31cb4eb"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1619Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1619",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "aa6ed732-066e-46b7-97bf-cc14d7f302fd"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1046Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1046",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "d4c52a78-44ce-437e-98a0-9ef447ce0fd5"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1201Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1201",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "f8647d36-5a6e-4412-b33f-a2c33b32f009"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1069Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1069",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "f7824a5b-4d2d-4a24-a807-05d282d493a7"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1518Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1518",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "5c41a1c2-44da-4ca0-a705-a09b741d2e9c"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1082Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1082",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "7a35e677-95e6-452f-b78d-b54cff0b3d27"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1614Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1614",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "2feea22f-133e-4377-9f34-ef2f5dd55e66"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "10",
"name": "Hidden Parameters"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Account Discovery (T1087)](https://attack.mitre.org/techniques/T1087/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Email Account (T1087.003)](https://attack.mitre.org/techniques/T1087/003)
\r\n🟥 ️[Cloud Account (T1087.004)](https://attack.mitre.org/techniques/T1087/004)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Operating System Configuration (M1028)](https://attack.mitre.org/mitigations/M1028)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Operating System Configuration) Tutorial: Monitor Changes and Update a Windows Virtual Machine in Azure](https://docs.microsoft.com/azure/virtual-machines/windows/tutorial-config-management)
\r\n\r\n### Microsoft Portals \r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[CM-6, CM-7, SI-4](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1087\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"CM.6.*\", \"CM.7.*\",\" SI.4.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1087Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Account Discovery",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Cloud Infrastructure Discovery (T1580)](https://attack.mitre.org/techniques/T1580/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(User Account Management) What are Entra ID access reviews?](https://docs.microsoft.com/azure/active-directory/governance/access-reviews-overview)
\r\n\r\n### Microsoft Portals \r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1580\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"IA.2.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1580Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Cloud Infrastructure Discovery",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Cloud Service Dashboard (T1538)](https://attack.mitre.org/techniques/T1538/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(User Account Management) What are Entra ID access reviews?](https://docs.microsoft.com/azure/active-directory/governance/access-reviews-overview)
\r\n\r\n\r\n### Microsoft Portals \r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-2, AC-3, AC-5, AC-6, IA-2, IA-8](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1538\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"IA.2.*\", \"IA.8.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1538Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Cloud Service Dashboard",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Cloud Service Discovery (T1526)](https://attack.mitre.org/techniques/T1526/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[N/A](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1526\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1526Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Cloud Service Discovery",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Data from Cloud Storage Object (T1619)](https://attack.mitre.org/techniques/T1619/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(User Account Management) What are Entra ID access reviews?](https://docs.microsoft.com/azure/active-directory/governance/access-reviews-overview)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-17, AC-2, AC-3, AC-5, AC-6, CM-5, IA-2](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1619\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.17.*\", \"AC.2.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"CM.5.*\", \"IA.2.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1619Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Cloud Storage Object Discovery",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Network Service Scanning (T1046)](https://attack.mitre.org/techniques/T1046/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Disable or Remove Feature or Program (M1042)](https://attack.mitre.org/mitigations/M1042)
\r\n🟦 [Network Intrusion Prevention (M1031)](https://attack.mitre.org/mitigations/M1031)
\r\n🟦 [Network Segmentation (M1030)](https://attack.mitre.org/mitigations/M1030)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Disable or Remove Feature or Program) Deploy Microsoft Defender for Cloud Apps for Integrated Vulnerability Assessments](https://docs.microsoft.com/azure/security-center/deploy-vulnerability-assessment-vm)
\r\n💡 [(Network Intrusion Prevention) Leverage Azure Firewall for Network Intrusion Prevention](https://docs.microsoft.com/azure/firewall/premium-features#idpst)
\r\n💡 [(Network Segmentation) Leverage Network Security Groups](https://docs.microsoft.com/azure/virtual-network/manage-network-security-group)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
🔀 [Firewall Policies](https://portal.azure.com/#blade/HubsExtension/BrowseResourceBlade/resourceType/Microsoft.Network%2FfirewallPolicies)
\r\n🔀 [Network Security Groups](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Network%2FNetworkSecurityGroups)\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-4, CA-7, CM-2, CM-6, CM-7, CM-8, RA-5, SC-7, SI-3, SI-4](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1046\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.4.*\", \"CA.7.*\", \"CM.2.*\", \"CM.6.*\", \"CM.7.*\", \"CM.8.*\", \"RA.5.*\", \"SC.7.*\", \"SI.3.*\", \"SI.4.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1046Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Network Service Scanning",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Password Policy Discovery (T1201)](https://attack.mitre.org/techniques/T1201/)\r\n\r\n### Recommended Logs\r\n🔷 [SigninLogs](https://docs.microsoft.com/azure/azure-monitor/reference/tables/signinlogs) ✳️ [Microsoft Entra ID](https://azure.microsoft.com/services/active-directory/)
🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) 🔷 [SecurityBaselines](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securitybaseline) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation \r\n🟦 [Password Policies (M1027)](https://attack.mitre.org/mitigations/M1027)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Multi-Factor Authentication) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n💡 [(Application Developer Guidance) Secure Secrets with Azure Key Vault](https://docs.microsoft.com/azure/key-vault/general/basic-concepts)
\r\n💡 [(Password Policies) Password and Account Lockout Policies on Microsoft Entra ID Domain Services Managed Domains](https://docs.microsoft.com/azure/active-directory-domain-services/password-policy#)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[CA-7, CM-2, CM-6, SI-3, SI-4](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1201\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"CA.7.*\", \"CM.2.*\", \"CM.6.*\", \"SI.3.*\", \"SI.4.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "let FailedAssets=SecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"password\"\r\n| where AnalyzeResult == \"Failed\"\r\n| summarize FailedAssets = makelist(Computer) by Description;\r\nlet PassedAssets=SecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"password\"\r\n| where AnalyzeResult == \"Passed\"\r\n| summarize PassedAssets = makelist(Computer) by Description;\r\nSecurityBaseline\r\n| summarize arg_max(TimeGenerated, *) by _ResourceId, Description\r\n| where Description contains \"password\"\r\n| summarize\r\n Failed = countif(AnalyzeResult == \"Failed\"),\r\n Passed = countif(AnalyzeResult == \"Passed\"),\r\n Total = countif(AnalyzeResult == \"Failed\" or AnalyzeResult == \"Passed\")\r\n by Description\r\n| extend PassedControls = (Passed / todouble(Total)) * 100\r\n| join kind=fullouter(FailedAssets) on Description\r\n| join kind=fullouter(PassedAssets) on Description\r\n| project Description, Total, PassedControls, Passed, Failed, PassedAssets, FailedAssets\r\n| sort by Total, Passed desc\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 ️[Password Policies] Review Security Baselines",
"noDataMessage": "An Empty Panel Provides Opportunity To Explore Further and Implement Hardening. Controls: Confirm Licensing, Availability, and Health of Respective Offerings. Logging: Confirm Log Source is Onboarded to the Log Analytics Workspace. Time: Adjust the Time Parameter for a Larger Data-Set. ",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationDisplayName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "ControlNumber",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "AllServices",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "RecommendationState",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "!=",
"thresholdValue": "Healthy",
"representation": "3",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "success",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "count_",
"formatter": 4,
"formatOptions": {
"palette": "blue"
}
}
],
"filter": true
}
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1201Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Password Policy Discovery",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Permission Groups Discovery (T1069)](https://attack.mitre.org/techniques/T1069/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Cloud Groups (T1069.003)](https://attack.mitre.org/techniques/T1069/003)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[N/A](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1069\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1069Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Permission Groups Discovery",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Software Discovery (T1518)](https://attack.mitre.org/techniques/T1518/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Security Software Discovery (T1518.001)](https://attack.mitre.org/techniques/T1518/001)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[N/A](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)\r\n"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1518\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1518Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Software Discovery",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [System Information Discovery (T1082)](https://attack.mitre.org/techniques/T1082/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[N/A](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)\r\n"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1082\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1082Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "System Information Discovery",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [System Location Discovery (T1614)](https://attack.mitre.org/techniques/T1614/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[N/A](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1614\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1614Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "System Location Discovery",
"styleSettings": {
"showBorder": true
}
}
]
},
"conditionalVisibility": {
"parameterName": "isDIVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Discovery Group"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Lateral Movement](https://attack.mitre.org/tactics/TA0008/) \r\n---\r\nThe adversary is trying to move through your environment. Lateral Movement consists of techniques that adversaries use to enter and control remote systems on a network. Following through on their primary objective often requires exploring the network to find their target and subsequently gaining access to it. Reaching their objective often involves pivoting through multiple systems and accounts to gain. Adversaries might install their own remote access tools to accomplish Lateral Movement or use legitimate credentials with native network and operating system tools, which may be stealthier.\r\n"
},
"customWidth": "40",
"name": "Lateral Movement Guide"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "10",
"name": "text - 4"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "{\"version\":\"1.0.0\",\"content\":\"[\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1534] Internal Spearphishing\\\", \\\"tab\\\": \\\"T1534\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1080] Taint Shared Content\\\", \\\"tab\\\": \\\"T1080\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1550] Use Alternate Authentication Material\\\", \\\"tab\\\": \\\"T1550\\\" }\\r\\n]\",\"transformers\":null}",
"size": 3,
"exportMultipleValues": true,
"exportedParameters": [
{
"fieldName": "tab",
"parameterName": "Tab",
"parameterType": 1
}
],
"queryType": 8,
"gridSettings": {
"formatters": [
{
"columnMatch": "Section",
"formatter": 8,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "tab",
"formatter": 5
}
]
}
},
"customWidth": "40",
"name": "Control Areas",
"styleSettings": {
"showBorder": true
}
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"parameters": [
{
"id": "a30d01d0-38f1-4a91-9cf6-cdb181d676b5",
"version": "KqlParameterItem/1.0",
"name": "isT1534Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1534",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1080Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1080",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "f2b7db18-acdf-41e4-aa13-85f90e4a5fd8"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1550Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1550",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "ed4a069b-1401-4b3d-8015-e2e76ee29a75"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "10",
"name": "Hidden Parameters"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Internal Spear-Phishing (T1534)](https://attack.mitre.org/techniques/T1534/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[N/A](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1534\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1534Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Internal Spear-Phishing",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Taint Shared Content (T1080)](https://attack.mitre.org/techniques/T1080/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Execution Prevention (M1038)](https://attack.mitre.org/mitigations/M1038)
\r\n🟦 [Exploit Protection (M1050)](https://attack.mitre.org/mitigations/M1050)
\r\n🟦 [Restrict File & Directory Permissions (M1022)](https://attack.mitre.org/mitigations/M1022)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Execution Prevention) Leverage Microsoft Defender Application Guard](https://docs.microsoft.com/windows/security/threat-protection/microsoft-defender-application-guard/md-app-guard-overview)
\r\n💡 [(Exploit Protection) Create and Deploy an Exploit Guard Policy](https://docs.microsoft.com/mem/configmgr/protect/deploy-use/create-deploy-exploit-guard-policy)
\r\n💡 [(Restrict File & Directory Permissions) Best Practices for Azure RBAC](https://docs.microsoft.com/azure/role-based-access-control/best-practices)
\r\n\r\n### Microsoft Portals \r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-3, CA-7, CM-2, CM-7, SC-4, SC-7, SI-10, SI-3, SI-4, SI-7](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1080\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.3.*\", \"CA.7.*\", \"CM.2.*\", \"CM.7.*\", \"SC.4.*\", \"SC.7.*\", \"SI.10.*\", \"SI.3.*\", \"SI.4.*\", \"SI.7.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1080Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Taint Shared Content",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Use Alternate Authentication Material (T1550)](https://attack.mitre.org/techniques/T1550/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Application Access Token (T1550.001)](https://attack.mitre.org/techniques/T1550/001)
\r\n🟥 ️[Web Session Cookie (T1550.004)](https://attack.mitre.org/techniques/T1550/004)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Privileged Account Management (M1026)](https://attack.mitre.org/mitigations/M1026)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Privileged Account Management) Deploy Entra ID Privileged Identity Management (PIM)](https://docs.microsoft.com/azure/active-directory/privileged-identity-management/pim-deployment-plan)
\r\n💡 [(User Account Management) Review Access Recommendations](https://docs.microsoft.com/azure/storage/common/storage-account-keys-manage)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender for Cloud Apps](https://seccxpninja.portal.cloudappsecurity.com/)
🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
🔀 [Privileged Identity Management](https://portal.azure.com/#blade/Microsoft_Azure_PIMCommon/CommonMenuBlade/quickStart)
"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1550\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.2.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"CM.5.*\", \"CM.6.*\", \"IA.2.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1550Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Use Alternate Authentication Material",
"styleSettings": {
"showBorder": true
}
}
]
},
"conditionalVisibility": {
"parameterName": "isLAVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Lateral Movement Group"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Collection](https://attack.mitre.org/tactics/TA0009/) \r\n---\r\nThe adversary is trying to gather data of interest to their goal. Collection consists of techniques adversaries may use to gather information and the sources information is collected from that are relevant to following through on the adversary's objectives. Frequently, the next goal after collecting data is to steal (exfiltrate) the data. Common target sources include various drive types, browsers, audio, video, and email. Common collection methods include capturing screenshots and keyboard input.\r\n"
},
"customWidth": "40",
"name": "Collection Guide"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "10",
"name": "text - 7"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "{\"version\":\"1.0.0\",\"content\":\"[\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1530] Data from Cloud Storage Object\\\", \\\"tab\\\": \\\"T1530\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1213] Data from Information Repositories\\\", \\\"tab\\\": \\\"T1213\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1074] Data Staged\\\", \\\"tab\\\": \\\"T1074\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1114] Email Collection\\\", \\\"tab\\\": \\\"T1114\\\" }\\r\\n]\",\"transformers\":null}",
"size": 3,
"exportMultipleValues": true,
"exportedParameters": [
{
"fieldName": "tab",
"parameterName": "Tab",
"parameterType": 1
}
],
"queryType": 8,
"gridSettings": {
"formatters": [
{
"columnMatch": "Section",
"formatter": 8,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "tab",
"formatter": 5
}
]
}
},
"customWidth": "40",
"name": "Control Areas",
"styleSettings": {
"showBorder": true
}
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"parameters": [
{
"id": "a30d01d0-38f1-4a91-9cf6-cdb181d676b5",
"version": "KqlParameterItem/1.0",
"name": "isT1530Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1530",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1213Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1213",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "e81eb44f-779e-44e1-bf04-a9beba38df97"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1074Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1074",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "9439db20-0d7b-4ba8-8a9b-9f14d78550d5"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1114Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1114",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "de34cbba-7917-4388-bd31-cfcc2561c0cb"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "10",
"name": "Hidden Parameters"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Data from Cloud Storage Object (T1530)](https://attack.mitre.org/techniques/T1530/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Audit (M1047)](https://attack.mitre.org/mitigations/M1047)
\r\n🟦 [Encrypt Sensitive Information (M1041)](https://attack.mitre.org/mitigations/M1041)
\r\n🟦 [Filter Network Traffic (M1037)](https://attack.mitre.org/mitigations/M1037)
\r\n🟦 [Multi-factor Authentication (M1032)](https://attack.mitre.org/mitigations/M1032)
\r\n🟦 [Restrict File and Directory Permissions (M1022)](https://attack.mitre.org/mitigations/M1022)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Audit) Review Policy/Trust Recommendations](https://docs.microsoft.com/azure/storage/common/storage-account-keys-manage)
\r\n💡 [(Encrypt Sensitive Information) Azure Encryption Overview](https://docs.microsoft.com/azure/security/fundamentals/encryption-overview)
\r\n💡 [(Filter Network Traffic) Leverage Network Security Groups](https://docs.microsoft.com/azure/virtual-network/manage-network-security-group)
\r\n💡 [(Multi-Factor Authentication) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n💡 [(Restrict File and Directory Permissions) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n💡 [(User Account Management) What are Entra ID access reviews?](https://docs.microsoft.com/azure/active-directory/governance/access-reviews-overview)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-17, AC-2, AC-3, AC-5, AC-6, CM-5, IA-2](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)\r\n"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1530\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.17.*\", \"AC.2.*\", \"AC.3.*\", \"AC.5.*\", \"AC.6.*\", \"CM.5.*\", \"IA.2.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1530Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Data from Cloud Storage Object",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Data from Information Repositories (T1213)](https://attack.mitre.org/techniques/T1213/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Confluence (T1213.001)](https://attack.mitre.org/techniques/T1213/001)
\r\n🟥 ️[Sharepoint(T1213.002)](https://attack.mitre.org/techniques/T1213/002)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Audit (M1047)](https://attack.mitre.org/mitigations/M1047)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n🟦 [User Training (M1017)](https://attack.mitre.org/mitigations/M1017)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Audit) Azure Security Logging and Auditing](https://docs.microsoft.com/azure/security/fundamentals/log-audit)
\r\n💡 [(User Account Management) What are Entra ID access reviews?](https://docs.microsoft.com/azure/active-directory/governance/access-reviews-overview)
\r\n💡 [(User Training) Leverage Microsoft Learn for Security Training](https://docs.microsoft.com/learn/browse/?terms=security%20threat)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
🔀 [Microsoft Entra ID](https://portal.azure.com/#blade/Microsoft_AAD_IAM/ActiveDirectoryMenuBlade/Overview)
🔀 [Microsoft Learn](https://docs.microsoft.com/learn)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-16, AC-17, AC-2, AC-21, AC-23, AC-3, AC-4, AC-5, AC-6, CA-7, CA-8, CM-2, CM-3, CM-5, CM-6, CM-7, CM-8, IA-2, IA-4, IA-8, RA-5, SC-28, SI-4, SI-7](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1213\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.16.*\", \"AC.17.*\", \"AC.2.*\", \"AC.21.*\", \"AC.23.*\", \"AC.3.*\", \"AC.4.*\", \"AC.5.*\", \"AC.6.*\", \"CA.7.*\", \"CA.8.*\", \"CM.2.*\", \"CM.3.*\", \"CM.5.*\", \"CM.6.*\", \"CM.7.*\", \"CM.8.*\", \"IA.2.*\", \"IA.4.*\", \"IA.8.*\", \"RA.5.*\", \"SC.28.*\", \"SI.4.*\", \"SI.7.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1213Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Data from Information Repositories",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Data Staged (T1074)](https://attack.mitre.org/techniques/T1074/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Remote Data Staging (T1074.002)](https://attack.mitre.org/techniques/T1074/002)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n\r\n### Microsoft Portals\r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[N/A](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1074\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1074Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Data Staged",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Email Collection (T1114)](https://attack.mitre.org/techniques/T1114/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Remote Email Collection (T1114.002)](https://attack.mitre.org/techniques/T1114/002)
\r\n🟥 ️[Email Forwarding Rule (T1114.003)](https://attack.mitre.org/techniques/T1114/003)
\r\n\r\n### Recommended Logs\r\n🔷 [OfficeActivity](https://docs.microsoft.com/azure/azure-monitor/reference/tables/officeactivity) ✳️ [Microsoft Defender for Office 365]( https://www.microsoft.com/microsoft-365/security/office-365-defender)
\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Audit (M1047)](https://attack.mitre.org/mitigations/M1047)
\r\n🟦 [Encrypt Sensitive Information (M1041)](https://attack.mitre.org/mitigations/M1041)
\r\n🟦 [Multi-factor Authentication (M1032)](https://attack.mitre.org/mitigations/M1032)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Audit) Review Policy/Trust Recommendations](https://docs.microsoft.com/azure/storage/common/storage-account-keys-manage)
\r\n💡 [(Encrypt Sensitive Information) Azure Encryption Overview](https://docs.microsoft.com/azure/security/fundamentals/encryption-overview)
\r\n💡 [(Multi-Factor Authentication) Review Your Security Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n\r\n### Microsoft Portals \r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-16, AC-17, AC-19, AC-20, AC-3, AC-4, CM-2, CM-6, IA-2, IA-5, SC-7, SI-12, SI-4, SI-7](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1114\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.16.*\", \"AC.17.*\", \"AC.19.*\", \"AC.20.*\", \"AC.3.*\", \"AC.4.*\", \"CM.2.*\", \"CM.6.*\", \"IA.2.*\", \"IA.5.*\", \"SC.7.*\", \"SI.12.*\", \"SI.4.*\", \"SI.7.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1114Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Email Collection",
"styleSettings": {
"showBorder": true
}
}
]
},
"conditionalVisibility": {
"parameterName": "isCNVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Collection Group"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Exfiltration](https://attack.mitre.org/tactics/TA0010/) \r\n---\r\nThe adversary is trying to steal data. Exfiltration consists of techniques that adversaries may use to steal data from your network. Once they’ve collected data, adversaries often package it to avoid detection while removing it. This can include compression and encryption. Techniques for getting data out of a target network typically include transferring it over their command and control channel or an alternate channel and may also include putting size limits on the transmission."
},
"customWidth": "40",
"name": "Exfiltration Guide"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "10",
"name": "text - 4"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "{\"version\":\"1.0.0\",\"content\":\"[\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1537] Transfer Data to Cloud Account\\\", \\\"tab\\\": \\\"T1537\\\" }\\r\\n]\",\"transformers\":null}",
"size": 3,
"exportMultipleValues": true,
"exportedParameters": [
{
"fieldName": "tab",
"parameterName": "Tab",
"parameterType": 1
}
],
"queryType": 8,
"gridSettings": {
"formatters": [
{
"columnMatch": "Section",
"formatter": 8,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "tab",
"formatter": 5
}
]
}
},
"customWidth": "40",
"name": "Control Areas",
"styleSettings": {
"showBorder": true
}
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"parameters": [
{
"id": "a30d01d0-38f1-4a91-9cf6-cdb181d676b5",
"version": "KqlParameterItem/1.0",
"name": "isT1537Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1537",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "10",
"name": "Hidden Parameters"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Transfer Data to Cloud Account (T1537)](https://attack.mitre.org/techniques/T1537/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Filter Network Traffic (M1037)](https://attack.mitre.org/mitigations/M1037)
\r\n🟦 [Password Policies (M1027)](https://attack.mitre.org/mitigations/M1027)
\r\n🟦 [User Account Management (M1018)](https://attack.mitre.org/mitigations/M1018)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Filter Network Traffic) Review Traffic Recommendations](https://docs.microsoft.com/azure/security-center/security-center-recommendations)
\r\n💡 [(Password Policies) Rotate Storage Access Keys with Azure Key Vault](https://docs.microsoft.com/azure/storage/common/storage-account-keys-manage)
\r\n💡 [(User Account Management) Review Access Recommendations](https://docs.microsoft.com/azure/storage/common/storage-account-keys-manage)
\r\n\r\n### Microsoft Portals \r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-16, AC-17, AC-2, AC-20, AC-3, AC-4, AC-5, AC-6, CA-7, CM-5, CM-6, CM-7, IA-2, IA-3, IA-4, IA-8, SC-7, SI-10, SI-15, SI-4](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1537\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.16.*\", \"AC.17.*\", \"AC.2.*\", \"AC.20.*\", \"AC.3.*\", \"AC.4.*\", \"AC.5.*\", \"AC.6.*\", \"CA.7.*\", \"CM.5.*\", \"CM.6.*\", \"CM.7.*\", \"IA.2.*\", \"IA.3.*\", \"IA.4.*\", \"IA.8.*\", \"SC.7.*\", \"SI.10.*\", \"SI.15.*\", \"SI.4.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1537Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Transfer Data to Cloud Account",
"styleSettings": {
"showBorder": true
}
}
]
},
"conditionalVisibility": {
"parameterName": "isENVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Exfiltration Group"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Impact](https://attack.mitre.org/tactics/TA0040/)\r\n---\r\nThe adversary is trying to manipulate, interrupt, or destroy your systems and data. Impact consists of techniques that adversaries use to disrupt availability or compromise integrity by manipulating business and operational processes. Techniques used for impact can include destroying or tampering with data. In some cases, business processes can look fine, but may have been altered to benefit the adversaries’ goals. These techniques might be used by adversaries to follow through on their end goal or to provide cover for a confidentiality breach."
},
"customWidth": "40",
"name": "Exfiltration Guide"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "10",
"name": "text - 9"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "{\"version\":\"1.0.0\",\"content\":\"[\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1485] Data Destruction\\\", \\\"tab\\\": \\\"T1485\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1486] Data Encrypted for Impact\\\", \\\"tab\\\": \\\"T1486\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1491] Defacement\\\", \\\"tab\\\": \\\"T1491\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1499] Endpoint Denial of Service\\\", \\\"tab\\\": \\\"T1499\\\" },\\r\\n\\t{ \\\"Techniques\\\": \\\"[T1498] Network Denial of Service\\\", \\\"tab\\\": \\\"T1498\\\" }\\r\\n]\",\"transformers\":null}",
"size": 3,
"exportMultipleValues": true,
"exportedParameters": [
{
"fieldName": "tab",
"parameterName": "Tab",
"parameterType": 1
}
],
"queryType": 8,
"gridSettings": {
"formatters": [
{
"columnMatch": "Section",
"formatter": 8,
"formatOptions": {
"palette": "blue"
}
},
{
"columnMatch": "tab",
"formatter": 5
}
]
}
},
"customWidth": "40",
"name": "Control Areas",
"styleSettings": {
"showBorder": true
}
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"parameters": [
{
"id": "a30d01d0-38f1-4a91-9cf6-cdb181d676b5",
"version": "KqlParameterItem/1.0",
"name": "isT1485Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1485",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
}
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1486Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1486",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "2a288a5e-e8e4-4ba0-a44e-80eca1f5ad5e"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1491Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1491",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "a1030220-61fa-4045-8291-a95decb4588e"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1499Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1499",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "4be396a3-1aac-4b1f-86ea-75481dbd6899"
},
{
"version": "KqlParameterItem/1.0",
"name": "isT1498Visible",
"type": 1,
"isHiddenWhenLocked": true,
"criteriaData": [
{
"criteriaContext": {
"leftOperand": "Tab",
"operator": "contains",
"rightValType": "static",
"rightVal": "T1498",
"resultValType": "static",
"resultVal": "true"
}
},
{
"criteriaContext": {
"operator": "Default",
"rightValType": "param",
"resultValType": "static",
"resultVal": "false"
}
}
],
"timeContext": {
"durationMs": 86400000
},
"id": "46ffac92-407a-4545-a2b1-b51493e4c5e3"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "10",
"name": "Hidden Parameters"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Data Destruction (T1485)](https://attack.mitre.org/techniques/T1485/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Data Backup (M1053)](https://attack.mitre.org/mitigations/M1053)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Data Backup) What is the Azure Backup service?](https://docs.microsoft.com/azure/backup/backup-overview)
\r\n\r\n### Microsoft Portals \r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Backup Vaults](https://portal.azure.com/#blade/Microsoft_Azure_Policy/PolicyMenuBlade/Overview)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-3, AC-6, CM-2, CP-10, CP-2, CP-7, CP-9, SI-3, SI-4, SI-7](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1485\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.3.*\", \"AC.6.*\", \"CM.2.*\", \"CP.10.*\", \"CP.2.*\", \"CP.7.*\", \"CP.9.*\", \"SI.3.*\", \"SI.4.*\", \"SI.7.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1485Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Data Destruction",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Data Encrypted for Impact (T1486)](https://attack.mitre.org/techniques/T1486/)\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Data Backup (M1053)](https://attack.mitre.org/mitigations/M1053)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Data Backup) What is the Azure Backup service?](https://docs.microsoft.com/azure/backup/backup-overview)
\r\n\r\n### Microsoft Portals \r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Backup Center](https://portal.azure.com/#blade/Microsoft_Azure_DataProtection/BackupCenterMenuBlade/overview)
\r\n🔀 [Backup Vaults](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.DataProtection%2FBackupVaults)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-3, AC-6, CM-2, CP-10, CP-2, CP-6, CP-7, CP-9, SI-3, SI-4, SI-7](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)\r\n"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1486\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.3.*\", \"AC.6.*\", \"CM.2.*\", \"CP.10.*\", \"CP.2.*\", \"CP.6.*\", \"CP.7.*\", \"CP.9.*\", \"SI.3.*\", \"SI.4.*\", \"SI.7.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1486Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Data Encrypted for Impact",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Defacement (T1491)](https://attack.mitre.org/techniques/T1491/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[External Defacement (T1491.002)](https://attack.mitre.org/techniques/T1491/002)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Data Backup (M1053)](https://attack.mitre.org/mitigations/M1053)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Data Backup) What is the Azure Backup service?](https://docs.microsoft.com/azure/backup/backup-overview)
\r\n\r\n### Microsoft Portals \r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Backup Vaults](https://portal.azure.com/#blade/Microsoft_Azure_Policy/PolicyMenuBlade/Overview)
🔀 [Web Application Firewall Policies](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Network%2FFrontDoorWebApplicationFirewallPolicies)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-3, AC-6, CM-2, CP-10, CP-2, CP-7, CP-9, SI-3, SI-4, SI-7](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1491\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.3.*\", \"AC.6.*\", \"CM.2.*\", \"CP.10.*\", \"CP.2.*\", \"CP.7.*\", \"CP.9.*\", \"SI.3.*\", \"SI.4.*\", \"SI.7.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1491Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Defacement",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Endpoint Denial of Service (T1499)](https://attack.mitre.org/techniques/T1499/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Service Exhaustion Flood (T1499.002)](https://attack.mitre.org/techniques/T1499/002)
\r\n🟥 ️[Application Exhaustion Flood (T1499.003)](https://attack.mitre.org/techniques/T1499/003)
\r\n🟥 ️[Application or System Exploitation (T1499.004)](https://attack.mitre.org/techniques/T1499/004)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Filter Network Traffic (M1037)](https://attack.mitre.org/mitigations/M1037)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Filter Network Traffic) Leverage Network Security Groups](https://docs.microsoft.com/azure/virtual-network/manage-network-security-group)
\r\n\r\n### Microsoft Portals \r\n🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
\r\n🔀 [DDoS Protection Plans](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Network%2FddosProtectionPlans)
\r\n🔀 [Microsoft Defender XDR](https://security.microsoft.com/)
🔀 [Network Security Groups](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Network%2FNetworkSecurityGroups)
🔀 [Virtual Networks](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Network%2FvirtualNetworks)
🔀 [Firewall Manager](https://portal.azure.com/#blade/Microsoft_Azure_HybridNetworking/FirewallManagerMenuBlade/firewallManagerOverview)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-3, AC-4, CA-7, CM-6, CM-7, SC-7, SI-10, SI-15, SI-4](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1499\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.3.*\", \"AC.4.*\", \"CA.7.*\", \"CM.6.*\", \"CM.7.*\", \"SC.7.*\", \"SI.10.*\", \"SI.15.*\", \"SI.4.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1499Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Endpoint Denial of Service",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Network Denial of Service (T1498)](https://attack.mitre.org/techniques/T1498/)\r\n\r\n### Sub-Techniques\r\n🟥 ️[Direct Network Flood (T1498.001)](https://attack.mitre.org/techniques/T1498/001)
\r\n🟥 ️[Reflection Amplification (T1498.002)](https://attack.mitre.org/techniques/T1498/002)
\r\n\r\n### Recommended Logs\r\n🔷 [SecurityIncident](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityincident) ✳️ [Microsoft Sentinel](https://azure.microsoft.com/services/microsoft-sentinel/)
\r\n🔷 [SecurityRegulatoryCompliance](https://docs.microsoft.com/azure/azure-monitor/reference/tables/securityregulatorycompliance) ✳️ [Microsoft Defender for Cloud](https://azure.microsoft.com/services/security-center/)
\r\n\r\n### Mitigation\r\n🟦 [Filter Network Traffic (M1037)](https://attack.mitre.org/mitigations/M1037)
\r\n\r\n### Microsoft Recommendations\r\n💡 [(Filter Network Traffic) Create and configure Azure DDoS Protection Standard](https://docs.microsoft.com/azure/ddos-protection/manage-ddos-protection)
\r\n\r\n### Microsoft Portals\r\n🔀 [DDoS Protection Plans](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Network%2FddosProtectionPlans)
🔀 [Microsoft Sentinel](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/microsoft.securityinsightsarg%2Fsentinel)
🔀 [Microsoft Defender for Cloud](https://portal.azure.com/#blade/Microsoft_Azure_Security/SecurityMenuBlade/0)
🔀 [Network Security Groups](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Network%2FNetworkSecurityGroups)
🔀 [Virtual Networks](https://portal.azure.com/#blade/HubsExtension/BrowseResource/resourceType/Microsoft.Network%2FvirtualNetworks)
🔀 [Firewall Manager](https://portal.azure.com/#blade/Microsoft_Azure_HybridNetworking/FirewallManagerMenuBlade/firewallManagerOverview)
\r\n\r\n### NIST 800-53 Controls to ATT&CK Mappings\r\n[AC-3, AC-4, CA-7, CM-6, CM-7, SC-7, SI-10, SI-15](https://ctid.mitre-engenuity.org/our-work/nist-800-53-control-mappings/)"
},
"customWidth": "50",
"name": "text - 5",
"styleSettings": {
"maxWidth": "50"
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "SecurityIncident\r\n| extend Techniques = tostring(parse_json(tostring(AdditionalData.techniques)))\r\n| extend Tactics = tostring(parse_json(tostring(AdditionalData.tactics)))\r\n| where Techniques <> \"\"\r\n| where Techniques contains \"T1498\"\r\n| summarize arg_max(TimeGenerated, *) by IncidentNumber\r\n| parse IncidentUrl with * '/#asset/Microsoft_Azure_Security_Insights/Incident' IncidentBlade\r\n| extend SeverityRank=iff(Severity == \"High\", 3, iff(Severity == \"Medium\", 2, iff(Severity == \"Low\", 1, iff(Severity == \"Informational\", 0, 0))))\r\n| sort by SeverityRank, TimeGenerated desc\r\n| project ['Incident Name']=Title, IncidentNumber, Severity, IncidentUrl, FirstActivityTime, IncidentBlade\r\n| limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟥 ️[Attack] Security Incidents by Technique",
"noDataMessage": "No Incidents Observed For This Technique Within These Thresholds",
"timeContext": {
"durationMs": 1209600000
},
"timeContextFromParameter": "TimeRange",
"showExportToExcel": true,
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "Incident Name",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Alert",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "IncidentUrl",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Go to Incident >>",
"bladeOpenContext": {
"bladeName": "CaseBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "id",
"source": "column",
"value": "IncidentBlade"
}
]
}
}
},
{
"columnMatch": "IncidentBlade",
"formatter": 5
}
],
"filter": true
}
},
"name": "query - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "521d368e-c46e-41b5-bea0-fd07dc96b511",
"linkTarget": "OpenBlade",
"linkLabel": "Review Current MITRE ATT&CK® Coverage >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "MitrePage.ReactView",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"name": "links - 8"
}
]
},
"customWidth": "50",
"name": "group - 3"
},
{
"type": 3,
"content": {
"version": "KqlItem/1.0",
"query": "securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | join kind = leftouter(\r\n securityresources\r\n | where type == \"microsoft.security/assessments\") on subscriptionId, name\r\n | extend complianceState = properties.state\r\n | extend resourceSource = tolower(tostring(properties1.resourceDetails.Source))\r\n | extend recommendationId = id1\r\n | extend resourceId = trim(' ', tolower(tostring(case(resourceSource =~ 'azure', properties1.resourceDetails.Id,\r\n resourceSource =~ 'gcp', properties1.resourceDetails.GcpResourceId,\r\n resourceSource =~ 'aws', properties1.resourceDetails.AwsResourceId,\r\n extract('^(.+)/providers/Microsoft.Security/assessments/.+$',1,recommendationId)))))\r\n | extend regexResourceId = extract_all(@\"/providers/[^/]+(?:/([^/]+)/[^/]+(?:/[^/]+/[^/]+)?)?/([^/]+)/([^/]+)$\", resourceId)[0]\r\n | extend resourceType = iff(regexResourceId[1] != \"\", regexResourceId[1], iff(regexResourceId[0] != \"\", regexResourceId[0], \"subscriptions\"))\r\n | extend resourceName = regexResourceId[2]\r\n | extend recommendationName = name\r\n | extend RecommendationName = properties1.displayName\r\n | extend description = properties1.metadata.description\r\n | extend remediationSteps = properties1.metadata.remediationDescription\r\n | extend Severity = properties1.metadata.severity\r\n | extend state = properties1.status.code\r\n | extend notApplicableReason = properties1.status.cause\r\n | extend RecommendationLink = properties1.links.azurePortal\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | extend complianceControlId = extract(@\"/regulatoryComplianceControls/([^/]*)\", 1, id)\r\n | join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend controlName = tostring(properties.description)\r\n | project controlId = name, controlName\r\n | distinct *) on $right.controlId == $left.complianceControlId\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend ControlFamily=iff(controlId contains \"AC.\", \"Access Control\", iff(controlId contains \"AT.\", \"Security Awareness & Training\", iff(controlId contains \"AU.\", \"Audit & Accountability\", iff(controlId contains \"CA.\", \"Security Assessment\", iff(controlId contains \"CM.\", \"Configuration Management\", iff(controlId contains \"CP.\", \"Contingency Planning\", iff(controlId contains \"IA.\", \"Identification & Authentication\", iff(controlId contains \"IR.\", \"Incident Response\", iff(controlId contains \"MA.\", \"System Maintenance\", iff(controlId contains \"MP.\", \"Media Protection\", iff(controlId contains \"PE.\", \"Physical Protection\", iff(controlId contains \"PL.\", \"Security Planning\", iff(controlId contains \"PS.\", \"Personnel Security\",iff(controlId contains \"RA.\", \"Risk Assessment\",iff(controlId contains \"SA.\", \"System & Services Acquisition\",iff(controlId contains \"SC.\", \"System & Communications Protection\",iff(controlId contains \"SI.\", \"System & Information Integrity\",\"Other\")))))))))))))))))\r\n | summarize Failed = countif(state == \"Unhealthy\"), Passed = countif(state == \"Healthy\" or complianceState == \"Passed\"), Total = countif(state == \"Unhealthy\" or state == \"Healthy\" or complianceState == \"Passed\") by RecommendationName, ['NIST SP 800-53 Control ID'] = controlId, ControlFamily, tostring(Severity)\r\n | extend PassedControls = (Passed/todouble(Total))*100\r\n| join kind = leftouter (securityresources\r\n | where type == \"microsoft.security/regulatorycompliancestandards/regulatorycompliancecontrols/regulatorycomplianceassessments\"\r\n | extend complianceStandardId = replace( \"-\", \" \", extract(@'/regulatoryComplianceStandards/([^/]*)', 1, id))\r\n | where complianceStandardId contains \"NIST SP 800 53 R4\"\r\n | extend RecommendationName = tostring(properties.description)\r\n | extend RecommendationLink = tostring(properties.assessmentDetailsLink)\r\n | project RecommendationName, RecommendationLink, name) on RecommendationName\r\n | distinct RecommendationName, ['NIST SP 800-53 Control ID'], ControlFamily, Severity, Total, RecommendationLink,PassedControls, Passed, Failed, name\r\n | where RecommendationName !startswith \"Microsoft Managed\"\r\n | where ['NIST SP 800-53 Control ID'] in~ (\"AC.3.*\", \"AC.4.*\", \"CA.7.*\", \"CM.6.*\", \"CM.7.*\", \"SC.7.*\", \"SI.10.*\", \"SI.15.*\")\r\n | where Total > 0\r\n | sort by Total, Passed desc\r\n | limit 250",
"size": 0,
"showAnalytics": true,
"title": "🟦 [Defense] Security Recommendations ",
"noDataMessage": "Confirm Microsoft Defender for Cloud: Regulatory Compliance Initiative for NIST SP 800-53 R4 is enabled. For more information, see https://docs.microsoft.com/azure/defender-for-cloud/update-regulatory-compliance-packages ",
"showExportToExcel": true,
"queryType": 1,
"resourceType": "microsoft.resourcegraph/resources",
"crossComponentResources": [
"{Workspace}"
],
"gridSettings": {
"formatters": [
{
"columnMatch": "RecommendationName",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Gear",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "ControlFamily",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "Default",
"thresholdValue": null,
"representation": "Persistence",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Severity",
"formatter": 18,
"formatOptions": {
"thresholdsOptions": "icons",
"thresholdsGrid": [
{
"operator": "==",
"thresholdValue": "High",
"representation": "Sev0",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Medium",
"representation": "Sev1",
"text": "{0}{1}"
},
{
"operator": "==",
"thresholdValue": "Low",
"representation": "Sev2",
"text": "{0}{1}"
},
{
"operator": "Default",
"thresholdValue": null,
"representation": "Sev3",
"text": "{0}{1}"
}
]
}
},
{
"columnMatch": "Total",
"formatter": 22,
"formatOptions": {
"compositeBarSettings": {
"labelText": "",
"columnSettings": [
{
"columnName": "Passed",
"color": "green"
},
{
"columnName": "Failed",
"color": "redBright"
}
]
}
}
},
{
"columnMatch": "PassedControls",
"formatter": 0,
"numberFormat": {
"unit": 1,
"options": {
"style": "decimal",
"useGrouping": true,
"maximumFractionDigits": 2
}
}
},
{
"columnMatch": "RecommendationLink",
"formatter": 7,
"formatOptions": {
"linkTarget": "OpenBlade",
"linkLabel": "Remediate >>",
"linkIsContextBlade": false,
"bladeOpenContext": {
"bladeName": "RecommendationsBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": [
{
"name": "assessmentKey",
"source": "column",
"value": "name"
}
]
}
}
},
{
"columnMatch": "name",
"formatter": 5
}
],
"filter": true
},
"sortBy": []
},
"name": "query - 3"
}
]
},
"conditionalVisibility": {
"parameterName": "isT1498Visible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Network Denial of Service",
"styleSettings": {
"showBorder": true
}
}
]
},
"conditionalVisibility": {
"parameterName": "isIMVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Impact Group"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Recommended Data Connectors](https://docs.microsoft.com/azure/sentinel/connect-data-sources)\r\n---\r\n\r\nAfter onboarding Microsoft Sentinel into your workspace, connect data sources to start ingesting your data into Microsoft Sentinel. Microsoft Sentinel comes with many connectors for Microsoft products, available out of the box and providing real-time integration. For example, service-to-service connectors include Microsoft Defender XDR connectors and Microsoft 365 sources, such as Office 365, Microsoft Entra ID (Entra ID), Microsoft Defender for Identity, and Microsoft Defender for Cloud Apps. Check out these references if you're new to Microsoft Sentinel."
},
"customWidth": "40",
"name": "NS Guide"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "10",
"name": "text - 2"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "b1cd1f8a-e807-4deb-93f4-7812e5ed014a",
"linkTarget": "OpenBlade",
"linkLabel": "Data Connectors >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "DataConnectorsBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": []
}
}
]
},
"customWidth": "20",
"name": "EL0"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "nav",
"links": [
{
"id": "b9a6293e-1c7b-4ec2-ad2a-d72b5ee01722",
"cellValue": "https://docs.microsoft.com/azure/sentinel/best-practices",
"linkTarget": "Url",
"linkLabel": "Best Practices",
"style": "link"
},
{
"id": "1bad541e-219a-4277-9510-876b0e8cad51",
"cellValue": "https://techcommunity.microsoft.com/t5/microsoft-sentinel-blog/azure-sentinel-all-in-one-accelerator/ba-p/1807933",
"linkTarget": "Url",
"linkLabel": "Microsoft Sentinel All-In-One Accelerator",
"style": "link"
},
{
"id": "7e8ff8aa-f632-4a4d-90cf-a71da0dc6b31",
"cellValue": "https://docs.microsoft.com/learn/browse/?wt.mc_id=resilience_skilling_webpage_gdc&terms=sentinel",
"linkTarget": "Url",
"linkLabel": "Microsoft Sentinel Training",
"style": "link"
}
]
},
"customWidth": "40",
"name": "links - 29"
}
],
"exportParameters": true
},
"name": "group - 7"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "## Foundational Connectors",
"style": "info"
},
"name": "text - 13"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "### [Azure Activity Connector](https://docs.microsoft.com/azure/azure-monitor/essentials/activity-log)"
},
"customWidth": "33",
"name": "text - 2"
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"crossComponentResources": [
"{Workspace}"
],
"parameters": [
{
"id": "909d0019-23cb-43ad-8285-9f1dca1cd1be",
"version": "KqlParameterItem/1.0",
"name": "AzureActivity",
"label": "Status",
"type": 1,
"query": "AzureActivity\r\n| limit 1\r\n| summarize count()\r\n| extend Results = iff(count_ ==0, \"❌ Not Connected\", \"✅ Connected\")\r\n| project Results",
"crossComponentResources": [
"{Workspace}"
],
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "33",
"name": "Azure Activity Connector"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "58cc25ab-a9af-4516-99e1-fa22e0637a76",
"linkTarget": "OpenBlade",
"linkLabel": "Enable Connector",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "DataConnectorBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "dataConnectorId",
"source": "static",
"value": "AzureActivity"
}
]
}
}
]
},
"customWidth": "33",
"name": "EL0"
}
],
"exportParameters": true
},
"name": "33",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "### [Microsoft Entra ID (Entra ID) Connector](https://docs.microsoft.com/azure/sentinel/connect-azure-active-directory)"
},
"customWidth": "33",
"name": "text - 2"
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"crossComponentResources": [
"{Workspace}"
],
"parameters": [
{
"id": "23ba579d-c894-43be-9fe1-d1b04bc34d7a",
"version": "KqlParameterItem/1.0",
"name": "SignInLogs",
"label": "Status",
"type": 1,
"query": "SigninLogs\r\n| limit 1\r\n| summarize count()\r\n| extend Results = iff(count_ ==0, \"❌ Not Connected\", \"✅ Connected\")\r\n| project Results",
"crossComponentResources": [
"{Workspace}"
],
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "33",
"name": "Azure Active Directory"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "7c97e893-29f3-4d4c-a379-f220bb82518c",
"linkTarget": "OpenBlade",
"linkLabel": "Enable Connector",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "DataConnectorBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "dataConnectorId",
"source": "static",
"value": "AzureActiveDirectory"
}
]
}
}
]
},
"customWidth": "33",
"name": "EL0"
}
],
"exportParameters": true
},
"name": "Azure Active Directory (AAD) Connector",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "### [Office 365 Connector](https://docs.microsoft.com/azure/sentinel/data-connectors-reference#microsoft-office-365)"
},
"customWidth": "33",
"name": "text - 2"
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"crossComponentResources": [
"{Workspace}"
],
"parameters": [
{
"id": "68bd12c8-e473-45d1-8bbc-2dd9f326ea69",
"version": "KqlParameterItem/1.0",
"name": "OfficeActivity",
"label": "Status",
"type": 1,
"query": "OfficeActivity\r\n| limit 1\r\n| summarize count()\r\n| extend Results = iff(count_ ==0, \"❌ Not Connected\", \"✅ Connected\")\r\n| project Results",
"crossComponentResources": [
"{Workspace}"
],
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "33",
"name": "Azure Activity Connector - Copy - Copy"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "6a86eb8d-5487-4aad-ae7b-b526e68a249f",
"linkTarget": "OpenBlade",
"linkLabel": "Enable Connector",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "DataConnectorBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "dataConnectorId",
"source": "static",
"value": "Office365"
}
]
}
}
]
},
"customWidth": "33",
"name": "EL0"
}
],
"exportParameters": true
},
"name": "Office 365 Connector",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "### [Microsoft Defender for Cloud Connector](https://docs.microsoft.com/azure/sentinel/data-connectors-reference#microsoft-defender-for-cloud)"
},
"customWidth": "33",
"name": "text - 2"
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"crossComponentResources": [
"{Workspace}"
],
"parameters": [
{
"id": "1673e4cf-354f-4a42-bed2-2374be47779e",
"version": "KqlParameterItem/1.0",
"name": "MDfC",
"label": "Status",
"type": 1,
"query": "SecurityAlert\r\n| where ProviderName == \"Azure Security Center\"\r\n| limit 1\r\n| summarize count()\r\n| extend Results = iff(count_ ==0, \"❌ Not Connected\", \"✅ Connected\")\r\n| project Results",
"crossComponentResources": [
"{Workspace}"
],
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "33",
"name": "Azure Activity Connector - Copy - Copy - Copy"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "56600b70-0e55-433a-be86-b7c561bced8b",
"linkTarget": "OpenBlade",
"linkLabel": "Enable Connector",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "DataConnectorBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "dataConnectorId",
"source": "static",
"value": "AzureSecurityCenter"
}
]
}
}
]
},
"customWidth": "33",
"name": "EL0"
}
],
"exportParameters": true
},
"name": "Microsoft Defender for Cloud Connector",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "### [Amazon Web Services (AWS) Connector](https://docs.microsoft.com/azure/sentinel/connect-aws?tabs=s3)"
},
"customWidth": "33",
"name": "text - 2"
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"crossComponentResources": [
"{Workspace}"
],
"parameters": [
{
"id": "18ed59f0-c497-44b1-94b7-8700051cf189",
"version": "KqlParameterItem/1.0",
"name": "AWS",
"label": "Status",
"type": 1,
"query": "AWSCloudTrail\r\n| limit 1\r\n| summarize count()\r\n| extend Results = iff(count_ ==0, \"❌ Not Connected\", \"✅ Connected\")\r\n| project Results",
"crossComponentResources": [
"{Workspace}"
],
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "33",
"name": "Azure Activity Connector - Copy - Copy - Copy - Copy - Copy - Copy - Copy - Copy - Copy - Copy - Copy"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "393c465e-4398-428b-8da2-87ac07d8a987",
"linkTarget": "OpenBlade",
"linkLabel": "Enable Connector",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "DataConnectorBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "dataConnectorId",
"source": "static",
"value": "AWS"
}
]
}
}
]
},
"customWidth": "33",
"name": "EL0"
}
],
"exportParameters": true
},
"name": "Amazon Web Services (AWS) Connector",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "### [Google Cloud Platform IAM Connector](https://docs.microsoft.com/azure/sentinel/data-connectors-reference#google-workspace-g-suite-preview)"
},
"customWidth": "33",
"name": "text - 2"
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"crossComponentResources": [
"{Workspace}"
],
"parameters": [
{
"id": "548cdd92-87c3-4e69-be08-52ecca0f76a8",
"version": "KqlParameterItem/1.0",
"name": "GCP",
"label": "Status",
"type": 1,
"query": "GCP_IAM_CL\r\n| limit 1\r\n| summarize count()\r\n| extend Results = iff(count_ ==0, \"❌ Not Connected\", \"✅ Connected\")\r\n| project Results",
"crossComponentResources": [
"{Workspace}"
],
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "33",
"name": "parameters - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "d9b9144c-69bc-4eb2-a747-a9e0d206780b",
"linkTarget": "OpenBlade",
"linkLabel": "Enable Connector",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "DataConnectorBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "dataConnectorId",
"source": "static",
"value": "1f2ba663-dd7a-49b6-87ba-0b8adf6d2d34"
}
]
}
}
]
},
"customWidth": "33",
"name": "EL0"
}
],
"exportParameters": true
},
"name": "Amazon Web Services (AWS) S3 Connector - Copy",
"styleSettings": {
"showBorder": true
}
}
],
"exportParameters": true
},
"name": "group - 5",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "## Basic Connectors",
"style": "info"
},
"name": "text - 13"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "### [Microsoft Defender XDR Connector](https://docs.microsoft.com/azure/sentinel/connect-microsoft-365-defender?tabs=MDE)"
},
"customWidth": "33",
"name": "text - 2"
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"crossComponentResources": [
"{Workspace}"
],
"parameters": [
{
"id": "548cdd92-87c3-4e69-be08-52ecca0f76a8",
"version": "KqlParameterItem/1.0",
"name": "M365Defender",
"label": "Status",
"type": 1,
"query": "AlertEvidence\r\n| limit 1\r\n| summarize count()\r\n| extend Results = iff(count_ ==0, \"❌ Not Connected\", \"✅ Connected\")\r\n| project Results",
"crossComponentResources": [
"{Workspace}"
],
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "33",
"name": "parameters - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "d9b9144c-69bc-4eb2-a747-a9e0d206780b",
"linkTarget": "OpenBlade",
"linkLabel": "Enable Connector",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "DataConnectorBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "dataConnectorId",
"source": "static",
"value": "MicrosoftThreatProtection"
}
]
}
}
]
},
"customWidth": "33",
"name": "EL0"
}
],
"exportParameters": true
},
"name": "Microsoft 365 Defender Connector",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "### [Microsoft Defender for Endpoint Connector](https://docs.microsoft.com/azure/sentinel/data-connectors-reference#microsoft-defender-for-endpoint)"
},
"customWidth": "33",
"name": "text - 2"
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"crossComponentResources": [
"{Workspace}"
],
"parameters": [
{
"id": "548cdd92-87c3-4e69-be08-52ecca0f76a8",
"version": "KqlParameterItem/1.0",
"name": "MDE",
"label": "Status",
"type": 1,
"query": "SecurityAlert\r\n| where ProviderName == \"MDATP\"\r\n| limit 1\r\n| summarize count()\r\n| extend Results = iff(count_ ==0, \"❌ Not Connected\", \"✅ Connected\")\r\n| project Results",
"crossComponentResources": [
"{Workspace}"
],
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "33",
"name": "parameters - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "d9b9144c-69bc-4eb2-a747-a9e0d206780b",
"linkTarget": "OpenBlade",
"linkLabel": "Enable Connector",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "DataConnectorBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "dataConnectorId",
"source": "static",
"value": "MicrosoftDefenderAdvancedThreatProtection"
}
]
}
}
]
},
"customWidth": "33",
"name": "EL0"
}
],
"exportParameters": true
},
"name": "Microsoft 365 Defender Connector - Copy",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "### [Azure DDoS Connector](https://docs.microsoft.com/azure/sentinel/data-connectors-reference#azure-ddos-protection)"
},
"customWidth": "33",
"name": "text - 2"
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"crossComponentResources": [
"{Workspace}"
],
"parameters": [
{
"id": "548cdd92-87c3-4e69-be08-52ecca0f76a8",
"version": "KqlParameterItem/1.0",
"name": "DDoS",
"label": "Status",
"type": 1,
"query": "AzureDiagnostics | where ResourceType == \"PUBLICIPADDRESSES\"\r\n| limit 1\r\n| summarize count()\r\n| extend Results = iff(count_ ==0, \"❌ Not Connected\", \"✅ Connected\")\r\n| project Results",
"crossComponentResources": [
"{Workspace}"
],
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "33",
"name": "Azure Activity Connector - Copy - Copy - Copy - Copy - Copy - Copy - Copy - Copy - Copy - Copy"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "d9b9144c-69bc-4eb2-a747-a9e0d206780b",
"linkTarget": "OpenBlade",
"linkLabel": "Enable Connector",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "DataConnectorBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "dataConnectorId",
"source": "static",
"value": "DDOS"
}
]
}
}
]
},
"customWidth": "33",
"name": "EL0"
}
],
"exportParameters": true
},
"name": "Azure DDoS Connector",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "### [Microsoft Defender for Cloud: Continuous Export](https://docs.microsoft.com/azure/defender-for-cloud/continuous-export?tabs=azure-portal)"
},
"customWidth": "33",
"name": "text - 2"
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"crossComponentResources": [
"{Workspace}"
],
"parameters": [
{
"id": "548cdd92-87c3-4e69-be08-52ecca0f76a8",
"version": "KqlParameterItem/1.0",
"name": "SecurityRecommendation",
"label": "Status",
"type": 1,
"query": "SecurityRecommendation\r\n| limit 1\r\n| summarize count()\r\n| extend Results = iff(count_ ==0, \"❌ Not Connected\", \"✅ Connected\")\r\n| project Results",
"crossComponentResources": [
"{Workspace}"
],
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "33",
"name": "parameters - 3"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "d9b9144c-69bc-4eb2-a747-a9e0d206780b",
"linkTarget": "OpenBlade",
"linkLabel": "Enable Feature",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "SecurityMenuBlade",
"extensionName": "Microsoft_Azure_Security",
"bladeParameters": []
}
}
]
},
"customWidth": "33",
"name": "EL0"
}
],
"exportParameters": true
},
"name": "Continuous Export Connector",
"styleSettings": {
"showBorder": true
}
}
],
"exportParameters": true
},
"name": "group - 6",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "## Advanced Connectors",
"style": "info"
},
"name": "text - 13"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "### [Microsoft Entra ID Identity Protection Connector](https://docs.microsoft.com/azure/sentinel/data-connectors-reference#azure-active-directory-identity-protection)"
},
"customWidth": "33",
"name": "text - 2"
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"crossComponentResources": [
"{Workspace}"
],
"parameters": [
{
"id": "548cdd92-87c3-4e69-be08-52ecca0f76a8",
"version": "KqlParameterItem/1.0",
"name": "AADIP",
"label": "Status",
"type": 1,
"query": "SecurityAlert | where ProductName == \"Azure Active Directory Identity Protection\"\r\n| limit 1\r\n| summarize count()\r\n| extend Results = iff(count_ ==0, \"❌ Not Connected\", \"✅ Connected\")\r\n| project Results",
"crossComponentResources": [
"{Workspace}"
],
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "33",
"name": "parameters - 1"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "d9b9144c-69bc-4eb2-a747-a9e0d206780b",
"linkTarget": "OpenBlade",
"linkLabel": "Enable Connector",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "DataConnectorBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "dataConnectorId",
"source": "static",
"value": "AzureActiveDirectoryIdentityProtection"
}
]
}
}
]
},
"customWidth": "33",
"name": "EL0"
}
],
"exportParameters": true
},
"name": "Azure Active Directory Identity Protection Connector",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "### [Microsoft Defender for IoT Connector](https://docs.microsoft.com/azure/sentinel/data-connectors-reference#microsoft-defender-for-iot)"
},
"customWidth": "33",
"name": "text - 2"
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"crossComponentResources": [
"{Workspace}"
],
"parameters": [
{
"id": "548cdd92-87c3-4e69-be08-52ecca0f76a8",
"version": "KqlParameterItem/1.0",
"name": "MD4IOT",
"label": "Status",
"type": 1,
"query": "SecurityAlert | where ProductName == \"Azure Security Center for IoT\"\r\n| limit 1\r\n| summarize count()\r\n| extend Results = iff(count_ ==0, \"❌ Not Connected\", \"✅ Connected\")\r\n| project Results",
"crossComponentResources": [
"{Workspace}"
],
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "33",
"name": "parameters - 1"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "d9b9144c-69bc-4eb2-a747-a9e0d206780b",
"linkTarget": "OpenBlade",
"linkLabel": "Enable Connector",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "DataConnectorBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "dataConnectorId",
"source": "static",
"value": "IoT"
}
]
}
}
]
},
"customWidth": "33",
"name": "EL0"
}
],
"exportParameters": true
},
"name": "Microsoft Defender for IoT Connector",
"styleSettings": {
"showBorder": true
}
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"loadType": "always",
"items": [
{
"type": 1,
"content": {
"json": "### [Microsoft Purview: Insider Risk Management Connector](https://docs.microsoft.com/azure/sentinel/data-connectors-reference#microsoft-purview-insider-risk-management-irm-preview)"
},
"customWidth": "33",
"name": "text - 2"
},
{
"type": 9,
"content": {
"version": "KqlParameterItem/1.0",
"crossComponentResources": [
"{Workspace}"
],
"parameters": [
{
"id": "548cdd92-87c3-4e69-be08-52ecca0f76a8",
"version": "KqlParameterItem/1.0",
"name": "IRM",
"label": "Status",
"type": 1,
"query": "SecurityAlert\r\n| where ProductName == \"Microsoft 365 Insider Risk Management\"\r\n| limit 1\r\n| summarize count()\r\n| extend Results = iff(count_ ==0, \"❌ Not Connected\", \"✅ Connected\")\r\n| project Results",
"crossComponentResources": [
"{Workspace}"
],
"timeContext": {
"durationMs": 0
},
"timeContextFromParameter": "TimeRange",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
}
],
"style": "pills",
"queryType": 0,
"resourceType": "microsoft.operationalinsights/workspaces"
},
"customWidth": "33",
"name": "parameters - 1"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "d9b9144c-69bc-4eb2-a747-a9e0d206780b",
"linkTarget": "OpenBlade",
"linkLabel": "Enable Connector",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "DataConnectorBlade",
"extensionName": "Microsoft_Azure_Security_Insights",
"bladeParameters": [
{
"name": "dataConnectorId",
"source": "static",
"value": "OfficeIRM"
}
]
}
}
]
},
"customWidth": "33",
"name": "EL0"
}
],
"exportParameters": true
},
"name": "Microsoft Purview: Insider Risk Management Connector",
"styleSettings": {
"showBorder": true
}
}
]
},
"name": "group - 6"
}
],
"exportParameters": true
},
"conditionalVisibility": {
"parameterName": "isDCVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Recommended Data Connectors"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Recommended Content](https://docs.microsoft.com/azure/sentinel/sentinel-solutions-catalog)\r\n---\r\n\r\nThe following content packages provide utility for regulated industries use cases."
},
"name": "NS Guide"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "nav",
"links": [
{
"id": "b9a6293e-1c7b-4ec2-ad2a-d72b5ee01722",
"cellValue": "https://docs.microsoft.com/azure/sentinel/sentinel-solutions",
"linkTarget": "Url",
"linkLabel": "About Microsoft Sentinel Content & Solutions",
"style": "link"
},
{
"id": "1bad541e-219a-4277-9510-876b0e8cad51",
"cellValue": "https://docs.microsoft.com/azure/sentinel/sentinel-solutions-catalog",
"linkTarget": "Url",
"linkLabel": "Content Hub Catalog",
"style": "link"
}
]
},
"name": "links - 29"
}
]
},
"customWidth": "40",
"name": "group - 4"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "10",
"name": "text - 2"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "list",
"links": [
{
"id": "76c7831e-386d-4289-8145-486f52cba8ec",
"linkTarget": "OpenBlade",
"linkLabel": "Content Hub >>",
"style": "secondary",
"bladeOpenContext": {
"bladeName": "ContentHub.ReactView",
"extensionName": "Microsoft_Azure_SentinelUS",
"bladeParameters": []
}
}
]
},
"customWidth": "40",
"name": "EL0"
}
]
},
"name": "group - 7"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Zero Trust (TIC 3.0) Solution](https://docs.microsoft.com/security/zero-trust/integrate/sentinel-solution)\r\n\r\n---\r\nThe Microsoft Sentinel Zero Trust (TIC 3.0) Solution provides a mechanism for viewing log queries aligned to Zero Trust and Trusted Internet Connections models across the Microsoft and partner ecosystem. This solution enables governance and compliance teams to design, build, monitor, and respond to Zero Trust (TIC 3.0) requirements across cloud, multi-cloud, 1st/3rd party workloads. The solution includes the new Zero Trust (TIC 3.0) Workbook, (1) Analytics Rule, and (3) Playbooks. While only Microsoft Sentinel and Microsoft Defender for Cloud are required to get started, the solution is enhanced with numerous Microsoft offerings.
\r\n\r\n---\r\n \r\n
 "
},
"name": "text - 0"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "nav",
"links": [
{
"id": "1bad541e-219a-4277-9510-876b0e8cad51",
"cellValue": "https://techcommunity.microsoft.com/t5/microsoft-sentinel-blog/next-evolution-of-the-microsoft-sentinel-zero-trust-tic-3-0/ba-p/3278097",
"linkTarget": "Url",
"linkLabel": "Solution Blog",
"style": "link"
},
{
"id": "b9a6293e-1c7b-4ec2-ad2a-d72b5ee01722",
"cellValue": "https://youtu.be/CxLzTRPuw-4",
"linkTarget": "Url",
"linkLabel": "Video Demo",
"style": "link"
},
{
"id": "7e8ff8aa-f632-4a4d-90cf-a71da0dc6b31",
"cellValue": "https://github.com/Azure/Azure-Sentinel/tree/master/Solutions/ZeroTrust(TIC3.0)",
"linkTarget": "Url",
"linkLabel": "GitHub Repo",
"style": "link"
}
]
},
"name": "links - 29"
},
{
"type": 1,
"content": {
"json": "\r\n\r\n"
},
"customWidth": "80",
"name": "text - 2"
}
]
},
"customWidth": "50",
"name": "Zero Trust Solution"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [NIST SP 800-53 Solution](https://docs.microsoft.com/security/zero-trust/integrate/sentinel-solution)\r\n\r\n---\r\nThis solution is designed to augment staffing through automation, machine learning, query/alerting generation, and visualizations. This workbook leverages Azure Policy, Azure Resource Graph, and Azure Log Analytics to align with NIST SP 800-53 control requirements. This offering telemetry from 25+ Microsoft Security products (1P/3P/Multi-Cloud/Hybrid/On-Premises). Each NIST SP 800-53 control includes a Control Card detailing an overview of requirements, primary/secondary controls, deep-links to referenced product pages/portals, recommendations, implementation guides, compliance cross-walks and tooling telemetry for building situational awareness of cloud workloads.
\r\n\r\n---\r\n\r\n"
},
"name": "text - 0"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "nav",
"links": [
{
"id": "1bad541e-219a-4277-9510-876b0e8cad51",
"cellValue": "https://techcommunity.microsoft.com/t5/microsoft-sentinel-blog/announcing-the-microsoft-sentinel-nist-sp-800-53-solution/ba-p/3381485",
"linkTarget": "Url",
"linkLabel": "Solution Blog",
"style": "link"
},
{
"id": "b9a6293e-1c7b-4ec2-ad2a-d72b5ee01722",
"cellValue": "https://youtu.be/ju9hxtYnj7s",
"linkTarget": "Url",
"linkLabel": "Video Demo",
"style": "link"
},
{
"id": "7e8ff8aa-f632-4a4d-90cf-a71da0dc6b31",
"cellValue": "https://github.com/Azure/Azure-Sentinel/tree/master/Solutions/NISTSP80053",
"linkTarget": "Url",
"linkLabel": "GitHub Repo",
"style": "link"
}
]
},
"name": "links - 29"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "90",
"name": "text - 2"
}
]
},
"customWidth": "50",
"name": "group - 10"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Cybersecurity Maturity Model Certification (CMMC) 2.0](https://www.acq.osd.mil/cmmc/index.html)\r\n---\r\n\r\nThis solution enables Compliance Teams, Architects, SecOps Analysts, and Consultants to gain situational awareness for cloud workload security posture. This solution is designed to augment staffing through automation, visibility, assessment, monitoring and remediation. This solution includes (1) Workbook for build/design/assessment/reporting, (2) Analytics rules for monitoring and (3) Playbooks for response/remediation. CMMC 2.0 is the next iteration of the Department’s CMMC cybersecurity model. It streamlines requirements to three levels of cybersecurity – Foundational, Advanced and Expert – and aligns the requirements at each level with well-known and widely accepted NIST cybersecurity standards.
\r\n\r\n---\r\n\r\n"
},
"name": "text - 0"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "nav",
"links": [
{
"id": "1bad541e-219a-4277-9510-876b0e8cad51",
"cellValue": "https://techcommunity.microsoft.com/t5/microsoft-sentinel-blog/announcing-the-microsoft-sentinel-cybersecurity-maturity-model/ba-p/3295095",
"linkTarget": "Url",
"linkLabel": "Solution Blog",
"style": "link"
},
{
"id": "b9a6293e-1c7b-4ec2-ad2a-d72b5ee01722",
"cellValue": "https://youtu.be/-_a5HxJgriE",
"linkTarget": "Url",
"linkLabel": "Video Demo",
"style": "link"
},
{
"id": "7e8ff8aa-f632-4a4d-90cf-a71da0dc6b31",
"cellValue": "https://github.com/Azure/Azure-Sentinel/tree/master/Solutions/CybersecurityMaturityModelCertification(CMMC)2.0",
"linkTarget": "Url",
"linkLabel": "GitHub Repo",
"style": "link"
}
]
},
"name": "links - 29"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "75",
"name": "text - 2"
}
]
},
"customWidth": "50",
"name": "group - 9"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Azure Security Benchmark v3](https://docs.microsoft.com/security/benchmark/azure/)\r\n---\r\n\r\nEnables Cloud Architects, Security Engineers, and Governance Risk Compliance Professionals to gain situational awareness for cloud security posture and hardening. Benchmark recommendations provide a starting point for selecting specific security configuration settings and facilitate risk reduction. The Azure Security Benchmark includes a collection of high-impact security recommendations for improving posture. This workbook provides visibility and situational awareness for security capabilities delivered with Microsoft technologies in predominantly cloud-based environments. Customer experience will vary by user and some panels may require additional configurations for operation.
\r\n\r\n---\r\n\r\n"
},
"name": "text - 0"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "nav",
"links": [
{
"id": "1bad541e-219a-4277-9510-876b0e8cad51",
"cellValue": "https://techcommunity.microsoft.com/t5/microsoft-defender-for-cloud/azure-security-benchmark-v3-workbook/ba-p/3257673",
"linkTarget": "Url",
"linkLabel": "Announce Blog",
"style": "link"
},
{
"id": "b9a6293e-1c7b-4ec2-ad2a-d72b5ee01722",
"cellValue": "https://youtu.be/v57gWjvcY4o",
"linkTarget": "Url",
"linkLabel": "Video Demo",
"style": "link"
},
{
"id": "cc5f4830-f090-4f5e-afb2-47adba6be532",
"cellValue": "https://youtu.be/qVJjwOipHDA",
"linkTarget": "Url",
"linkLabel": "ASC in the Field",
"style": "link"
},
{
"id": "7e8ff8aa-f632-4a4d-90cf-a71da0dc6b31",
"cellValue": "https://github.com/Azure/Microsoft-Defender-for-Cloud/tree/main/Workbooks/Azure%20Security%20Benchmark%20v3",
"linkTarget": "Url",
"linkLabel": "GitHub Repo",
"style": "link"
}
]
},
"name": "links - 29"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "86",
"name": "text - 2"
}
]
},
"customWidth": "50",
"name": "group - 9"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Microsoft Insider Risk Management Solution](https://techcommunity.microsoft.com/t5/microsoft-sentinel-blog/announcing-the-microsoft-sentinel-microsoft-insider-risk/ba-p/2955786)\r\n---\r\n\r\nInsider risk management helps minimize internal risks by enabling you to detect, investigate, and act on malicious and inadvertent activities in your organization. Insider risk policies allow you to define the types of risks to identify and detect in your organization, including acting on cases and escalating cases to Microsoft Advanced eDiscovery. Risk analysts in your organization can quickly take appropriate actions to make sure users are compliant with your organization's compliance standards. Insider risks come in various forms including both witting (intentional) and unwitting (unintentional). This workbook provides an automated visualization of Insider risk behavior cross walked to Microsoft security offerings.
\r\n\r\n---\r\n\r\n"
},
"name": "text - 0"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "nav",
"links": [
{
"id": "1bad541e-219a-4277-9510-876b0e8cad51",
"cellValue": "https://techcommunity.microsoft.com/t5/microsoft-sentinel-blog/announcing-the-microsoft-sentinel-microsoft-insider-risk/ba-p/2955786",
"linkTarget": "Url",
"linkLabel": "Solution Blog",
"style": "link"
},
{
"id": "7e8ff8aa-f632-4a4d-90cf-a71da0dc6b31",
"cellValue": "https://github.com/Azure/Azure-Sentinel/tree/master/Solutions/MicrosoftPurviewInsiderRiskManagement",
"linkTarget": "Url",
"linkLabel": "GitHub Repo",
"style": "link"
}
]
},
"name": "links - 29"
},
{
"type": 1,
"content": {
"json": ""
},
"customWidth": "75",
"name": "text - 2"
}
]
},
"customWidth": "50",
"name": "group - 9"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [IT/OT Threat Monitoring Solution](https://techcommunity.microsoft.com/t5/microsoft-sentinel-blog/defending-critical-infrastructure-with-the-microsoft-sentinel-it/ba-p/3061184)\r\n---\r\n\r\nThis solution provides the foundation for building a SOC for monitoring IoT/ OT and includes (1) workbook for visibility/reporting, (14) analytics rules for monitoring, and (4) playbooks for response. The workbook leverages Microsoft Sentinel telemetry to create visualization to understand, analyze, and respond to IoT/OT threats. Understanding alerts over time provides unprecedented insights into security posture and where teams need to focus to harden against threats. Deep links directly to Microsoft Defender for IoT alerts empower analysts to focus on remediating threats rather than pivoting between tools.
\r\n\r\n---\r\n\r\n"
},
"name": "text - 0"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "nav",
"links": [
{
"id": "1bad541e-219a-4277-9510-876b0e8cad51",
"cellValue": "https://techcommunity.microsoft.com/t5/microsoft-sentinel-blog/defending-critical-infrastructure-with-the-microsoft-sentinel-it/ba-p/3061184",
"linkTarget": "Url",
"linkLabel": "Solution Blog",
"style": "link"
},
{
"id": "8f7dce97-a41c-42b3-b62f-a21fbf5a1420",
"cellValue": "https://youtu.be/hZS2aplJoy8",
"linkTarget": "Url",
"linkLabel": "YouTube Demo",
"style": "link"
},
{
"id": "7e8ff8aa-f632-4a4d-90cf-a71da0dc6b31",
"cellValue": "https://github.com/Azure/Azure-Sentinel/blob/master/Solutions/IoTOTThreatMonitoringwithDefenderforIoT/readme.md",
"linkTarget": "Url",
"linkLabel": "GitHub Repo",
"style": "link"
}
]
},
"name": "links - 29"
},
{
"type": 1,
"content": {
"json": "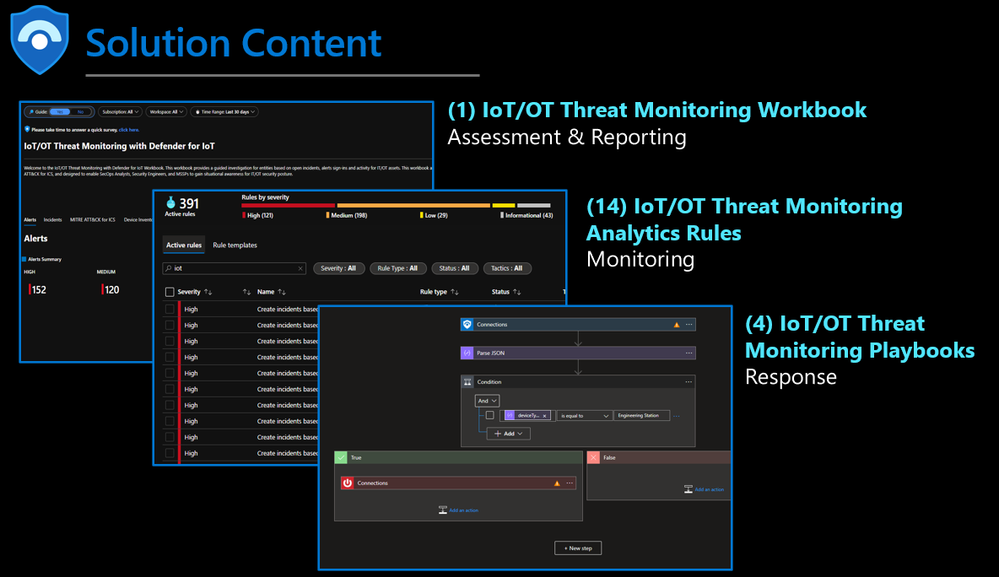"
},
"customWidth": "75",
"name": "text - 2"
}
]
},
"customWidth": "50",
"name": "group - 9"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Maturity Model for Event Log Management Solution](https://techcommunity.microsoft.com/t5/microsoft-sentinel-blog/modernize-log-management-with-the-maturity-model-for-event-log/ba-p/3072842)\r\n---\r\n\r\nThis solution is designed to enable Cloud Architects, Security Engineers, and Governance Risk Compliance Professionals to increase visibility before, during, and after a cybersecurity incident.\"Executive Order 14028, Improving the Nation's Cybersecurity, directs decisive action to improve the Federal Government’s investigative and remediation capabilities. This memorandum was developed in accordance with and addresses the requirements in section 8 of the Executive Order for logging, log retention, and log management, with a focus on ensuring centralized access and visibility for the highest-level enterprise security operations center (SOC) of each agency.\" For more information, see 💡[OMB's M-21-31 Memorandum](https://www.whitehouse.gov/wp-content/uploads/2021/08/M-21-31-Improving-the-Federal-Governments-Investigative-and-Remediation-Capabilities-Related-to-Cybersecurity-Incidents.pdf)\r\n\r\n---\r\n\r\n"
},
"name": "text - 0"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "nav",
"links": [
{
"id": "1bad541e-219a-4277-9510-876b0e8cad51",
"cellValue": "https://techcommunity.microsoft.com/t5/microsoft-sentinel-blog/modernize-log-management-with-the-maturity-model-for-event-log/ba-p/3072842",
"linkTarget": "Url",
"linkLabel": "Solution Blog",
"style": "link"
},
{
"id": "b9a6293e-1c7b-4ec2-ad2a-d72b5ee01722",
"cellValue": "https://youtu.be/quV_80ts__k",
"linkTarget": "Url",
"linkLabel": "Video Demo",
"style": "link"
},
{
"id": "7e8ff8aa-f632-4a4d-90cf-a71da0dc6b31",
"cellValue": "https://github.com/Azure/Azure-Sentinel/tree/master/Solutions/MaturityModelForEventLogManagementM2131",
"linkTarget": "Url",
"linkLabel": "GitHub Repo",
"style": "link"
}
]
},
"name": "links - 29"
},
{
"type": 1,
"content": {
"json": "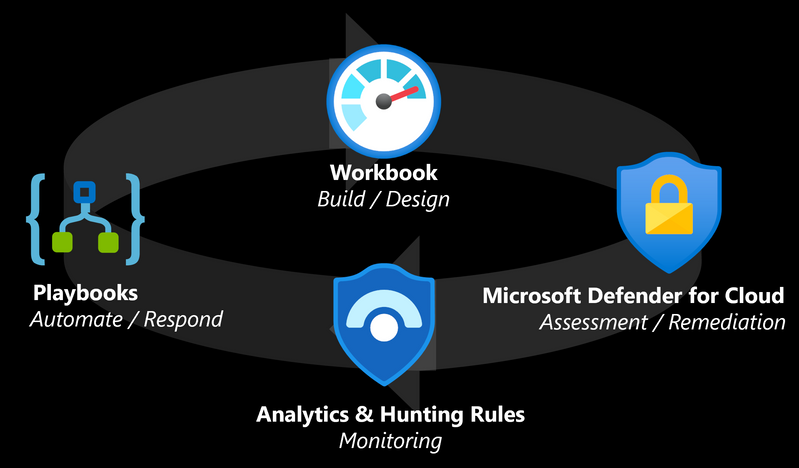"
},
"customWidth": "75",
"name": "text - 2"
}
]
},
"customWidth": "50",
"name": "group - 8"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Threat Analysis & Response Solution](https://github.com/Azure/Azure-Sentinel/tree/master/Solutions/ThreatAnalysis%26Response)\r\n---\r\n\r\nThis solution enables SecOps Analysts, Threat Intelligence Professional, and Threat Hunters to gain situational awareness for threats in cloud environment. The Solution includes (2) Workbooks designed to enable threat hunting programs. Threat analysis provides an understanding of where the attacker is in the cycle which often drives both a historic lens of where the threat may have progressed, but also predictive analytics on the threat’s objectives. This approach is adversarial as understanding of the threat’s attack cycle drives defense actions in a red versus blue model. The Threat Analysis & Response Solution augments the customer burden of building threat hunting programs.\r\n\r\n---\r\n\r\n"
},
"name": "text - 0"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "nav",
"links": [
{
"id": "7e8ff8aa-f632-4a4d-90cf-a71da0dc6b31",
"cellValue": "https://github.com/Azure/Azure-Sentinel/tree/master/Solutions/ThreatAnalysis%26Response",
"linkTarget": "Url",
"linkLabel": "GitHub Repo",
"style": "link"
}
]
},
"name": "links - 29"
},
{
"type": 1,
"content": {
"json": "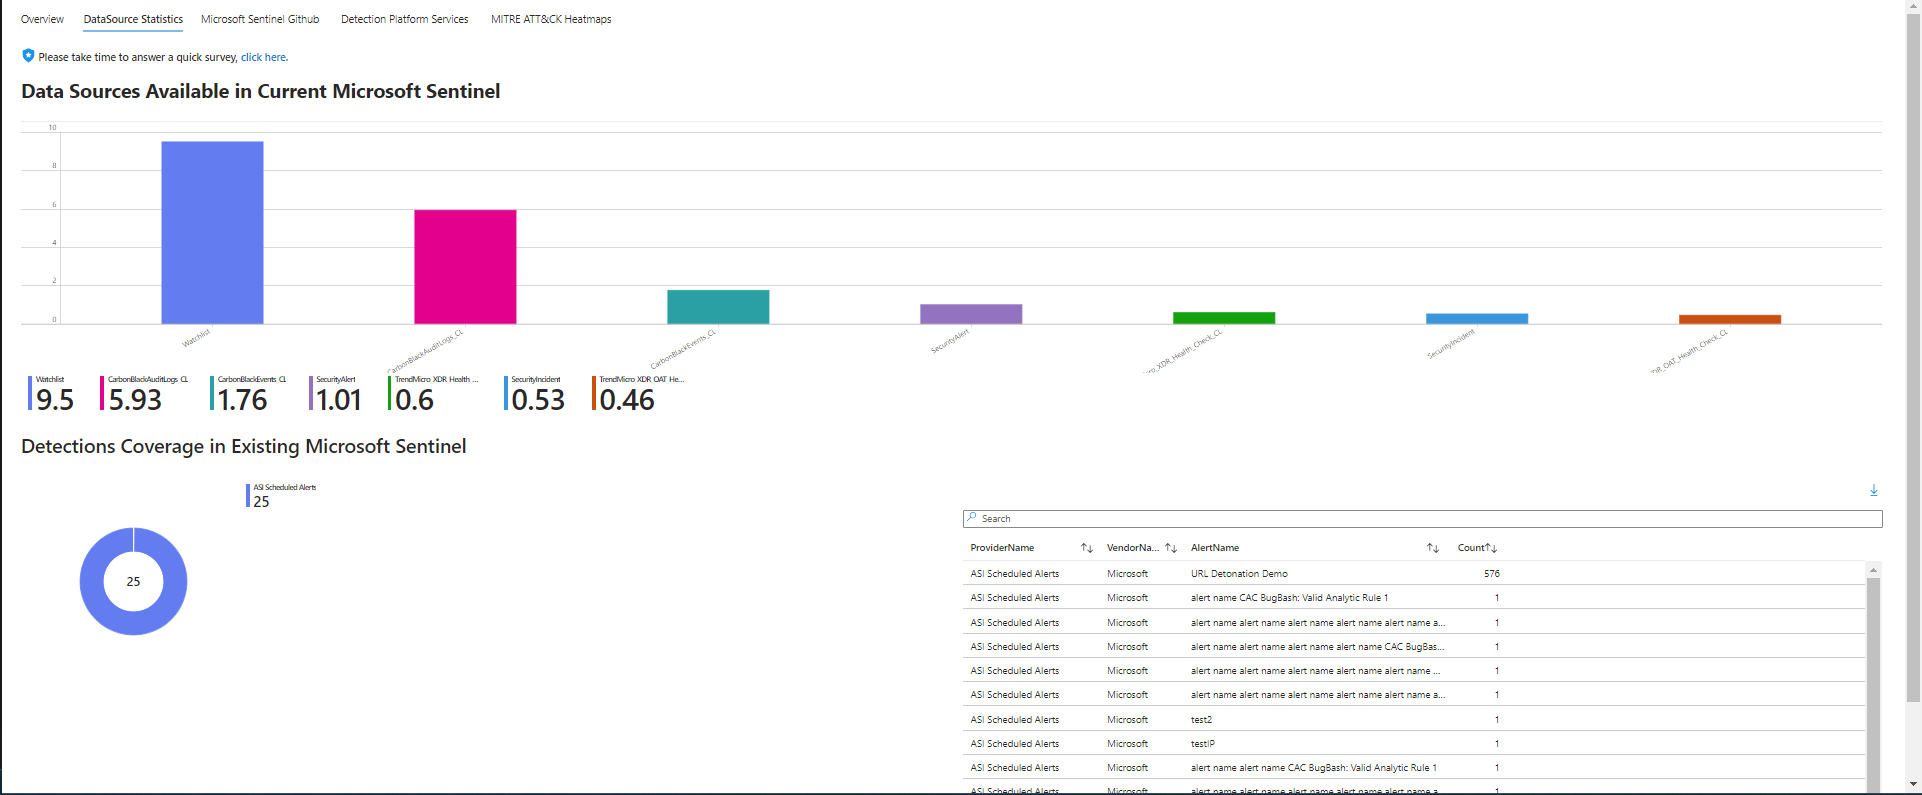"
},
"customWidth": " 100",
"name": "text - 2"
}
]
},
"customWidth": "50",
"name": "group - 9"
},
{
"type": 12,
"content": {
"version": "NotebookGroup/1.0",
"groupType": "editable",
"items": [
{
"type": 1,
"content": {
"json": "# [Threat Intelligence Workbook](https://docs.microsoft.com/security/benchmark/azure/)\r\n---\r\n\r\nThe most commonly used form of CTI is threat indicators, also known as Indicators of Compromise or IoCs. Threat indicators are data that associate observed artifacts such as URLs, file hashes, or IP addresses with known threat activity such as phishing, botnets, or malware. This form of threat intelligence is often called tactical threat intelligence because it can be applied to security products and automation in large scale to detect potential threats to an organization and protect against them. In Microsoft Sentinel, you can use threat indicators to help detect malicious activity observed in your environment and provide context to security investigators to help inform response decisions.
\r\n\r\n---"
},
"name": "text - 0"
},
{
"type": 11,
"content": {
"version": "LinkItem/1.0",
"style": "nav",
"links": [
{
"id": "1bad541e-219a-4277-9510-876b0e8cad51",
"cellValue": "https://techcommunity.microsoft.com/t5/microsoft-sentinel-blog/what-s-new-azure-sentinel-threat-intelligence-workbook/ba-p/2858265",
"linkTarget": "Url",
"linkLabel": "Workbook Blog",
"style": "link"
},
{
"id": "b9a6293e-1c7b-4ec2-ad2a-d72b5ee01722",
"cellValue": "https://youtu.be/SjEG7iVVBbI",
"linkTarget": "Url",
"linkLabel": "Video Demo",
"style": "link"
},
{
"id": "7e8ff8aa-f632-4a4d-90cf-a71da0dc6b31",
"cellValue": "https://github.com/Azure/Azure-Sentinel/blob/master/Workbooks/ThreatIntelligence.json",
"linkTarget": "Url",
"linkLabel": "GitHub Repo",
"style": "link"
}
]
},
"name": "links - 29"
},
{
"type": 1,
"content": {
"json": "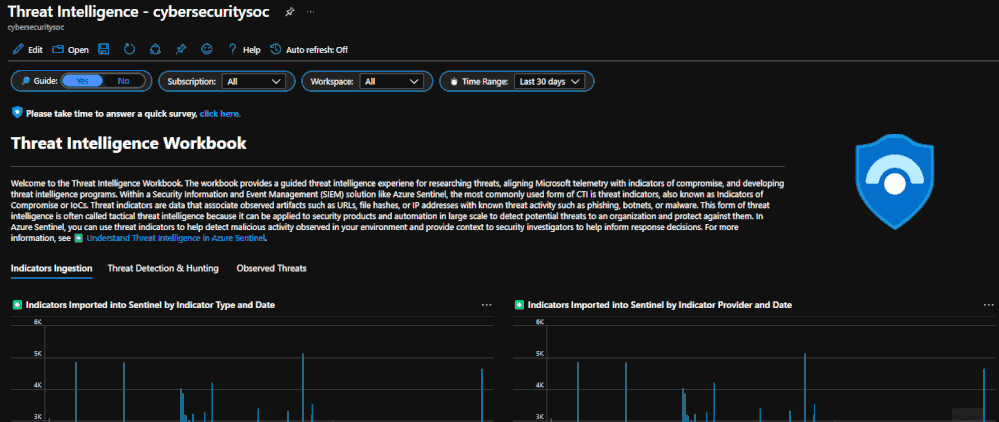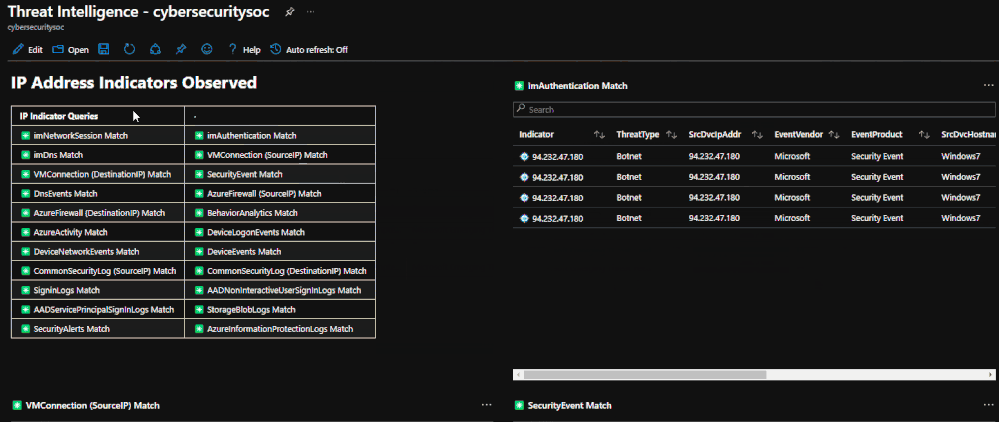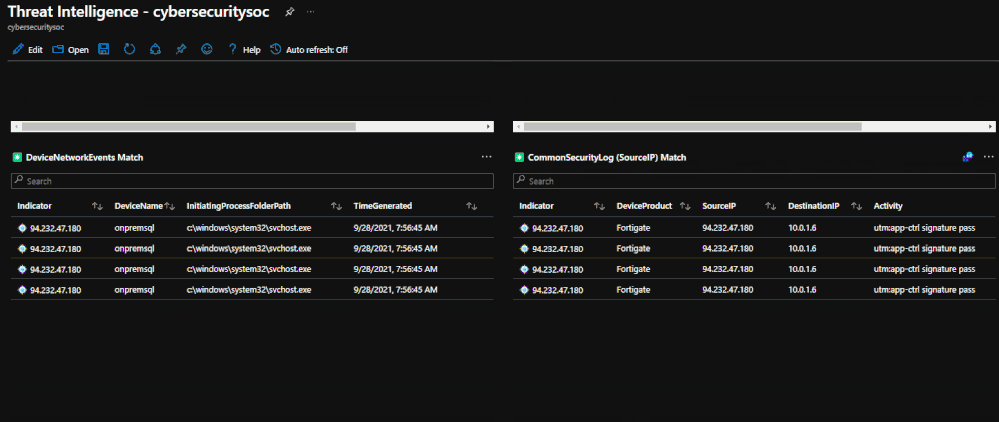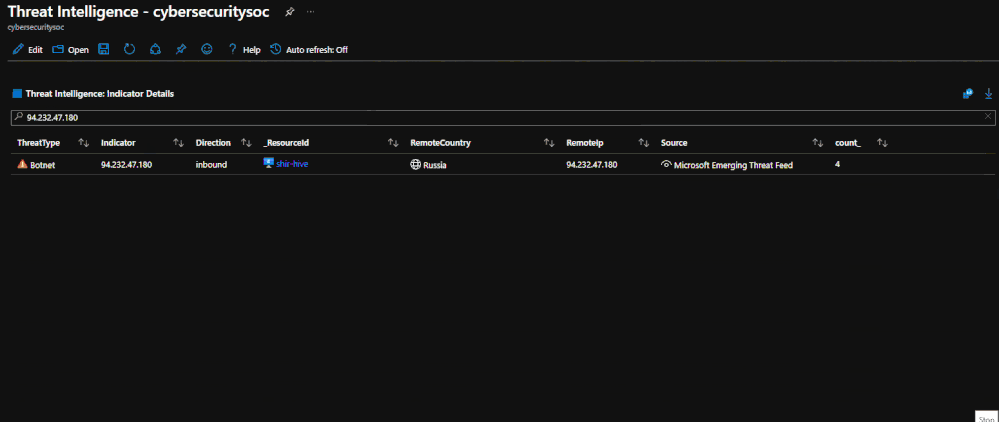"
},
"name": "text - 2"
}
]
},
"customWidth": "50",
"name": "Zero Trust Solution - Copy - Copy - Copy"
}
]
},
"conditionalVisibility": {
"parameterName": "isGCVisible",
"comparison": "isEqualTo",
"value": "true"
},
"name": "Recommended Content"
}
],
"fromTemplateId": "sentinel-DynamicThreatModeling&Response",
"$schema": "https://github.com/Microsoft/Application-Insights-Workbooks/blob/master/schema/workbook.json"
}